
 Do Son
A new report reveals Noisy Bear, an APT group targeting Kazakhstan’s oil and gas sector with spear-phishing and multi-stage malware, mimicking internal communications.
spear-phishing

An Iranian-aligned group abused a compromised Omani Foreign Ministry mailbox to send spear-phishing emails to diplomats and international organizations in a global campaign.

A new report reveals that the Pakistan-based APT36 is targeting Indian government entities using spear-phishing and Linux-specific malware to steal sensitive data.

A new report reveals a sophisticated spear-phishing campaign targeting finance executives. The attack uses social engineering and legitimate tools to evade detection.

A new report reveals a North Korean espionage campaign targeting embassies with spear phishing and a sophisticated C2 channel hidden on GitHub.

IBM X-Force warns that Russian-aligned Hive0156 is intensifying spear-phishing campaigns against Ukrainian government and military, delivering Remcos RAT via LNK/PowerShell files.

Greedy Sponge, a financially motivated group, is back with an upgraded AllaKore RAT and SystemBC, targeting Mexican organizations for banking credentials and financial fraud.

North Korean APT Kimsuky is evolving its ClickFix tactics, using deceptive social engineering, fake job portals, and obfuscated PowerShell to compromise targets via spear-phishing campaigns.

Iranian APT "Educated Manticore" (APT42) uses AI-assisted spear-phishing via email/WhatsApp to target critics with React-based phishing kits, bypassing MFA and stealing credentials.

Kimsuky APT is using HWP documents and stealthy AnyDesk backdoors in a new phishing campaign to infiltrate systems under the guise of academic collaboration.
CISA adds two critical vulnerabilities to KEV: Erlang/OTP (RCE) and Roundcube (XSS). Actively exploited, these flaws pose severe risks to systems and email accounts.

APT41 is leveraging Google Calendar as a covert C2 channel in a new multi-stage malware campaign targeting a Taiwanese government website.

CERT Polska warns of a critical Roundcube XSS flaw (CVE-2024-42009) exploited by UNC1151 in spear phishing, stealing credentials and compromising Polish organizations.

A sophisticated spear-phishing campaign using Signal targeted Armenian civil society and government in March 2025, linked to threat actor UNC5792.
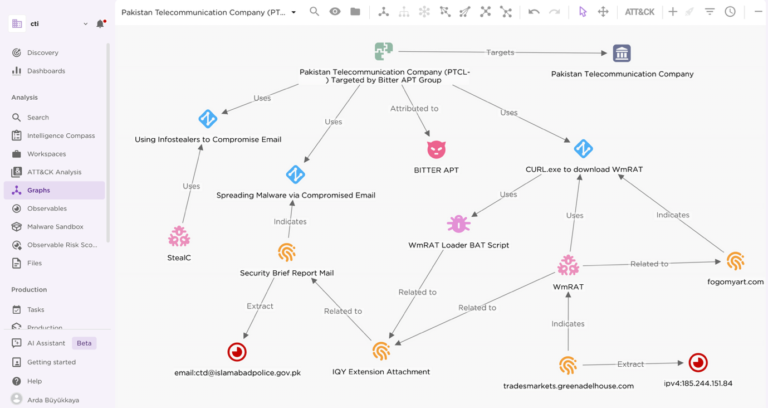
Amidst India-Pakistan tensions, Bitter APT launched a spear phishing campaign against Pakistan Telecommunication Company, using WmRAT for espionage.

A stealthy spear-phishing campaign uses fake Rothschild job offers to trick finance execs into installing NetBird RAT, gaining remote access.

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.
Earth Kasha targets Taiwan and Japan in a March 2025 spear-phishing campaign using ANEL and NOOPDOOR backdoors for stealthy cyber espionage.

Kimsuky revives PebbleDash malware using spear-phishing and patched RDP DLLs for stealthy access and control, warns new ASEC March 2025 report.
The NCSC reveals DAMASCENED PEACOCK, a sophisticated malware targeting the UK MOD, using spear-phishing, code signing, and COM Hijacking.

GOFFEE APT is actively targeting Russian organizations with updated tactics, including the new PowerModul implant, sophisticated spear phishing, and lateral movement via custom Mythic agents

The FlowerPower campaign ingeniously masquerades as interview requests from foreign news channels, leveraging the widely used Korean HWP