 Do Son
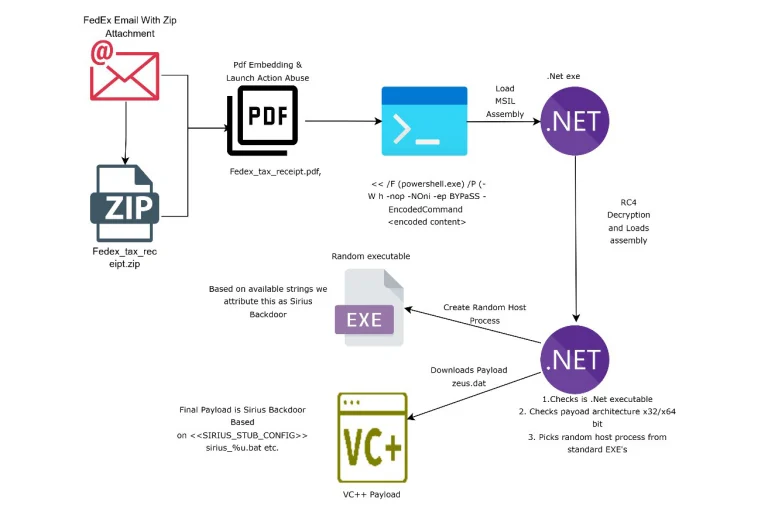
Trellix uncovers the Sirius Backdoor in fake FedEx tax invoices. See how the fileless Sirius Backdoor blinds EDRs and survives Windows OS resets.
spear-phishing
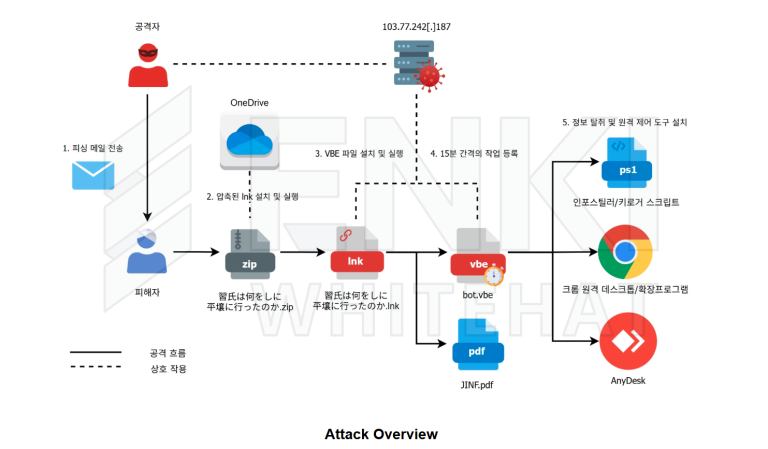
Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.

The DoNot APT hit Bangladesh military targets with a fake officer biography. Cyderes traced a live, multi-stage implant to active C2 servers.
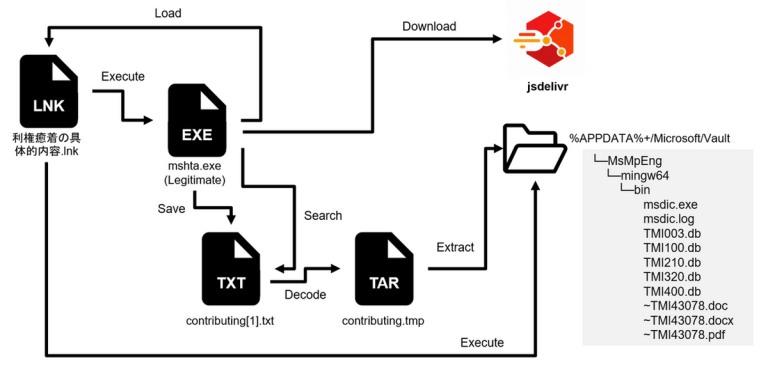
JPCERT/CC details new APT-C-60 attacks on Japan. The group abuses Proton Drive, LNK files, and GitHub to deploy SpyGlace malware.
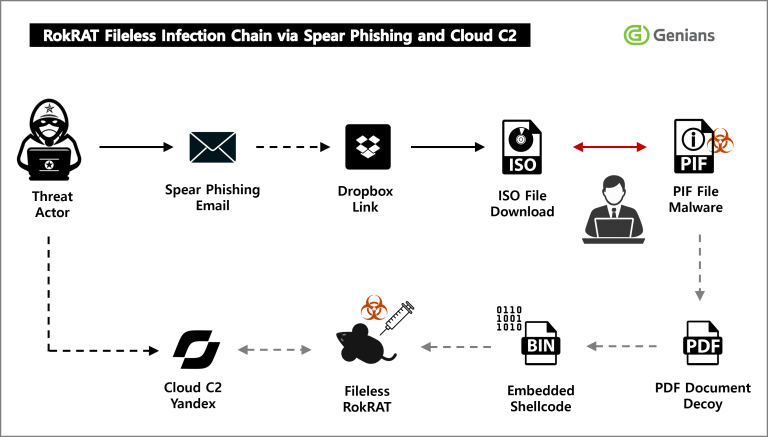
Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.

Seqrite ties a Rare Werewolf phishing campaign to Russian aerospace firms, using a fake invoice to plant AnyDesk for stealthy remote access.
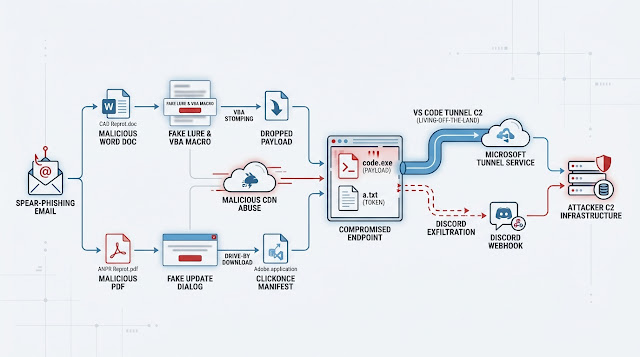
Learn how a sophisticated phishing campaign leverages VS Code Remote Tunnels abuse to bypass security and control enterprise networks.
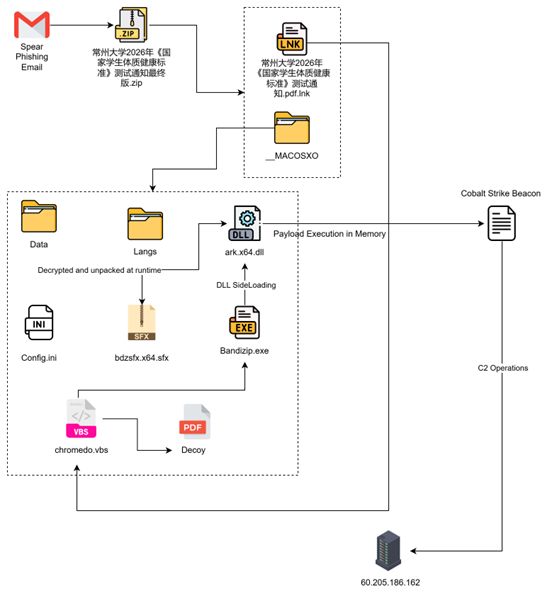
Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.
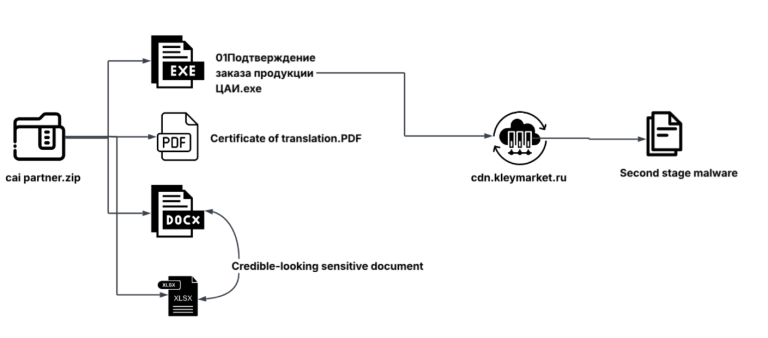
SEQRITE Labs uncovers Operation Silent Rotor, a targeted Rust-based cyberattack on the Eurasian unmanned aviation sector ahead of the 2026 Moscow forum.
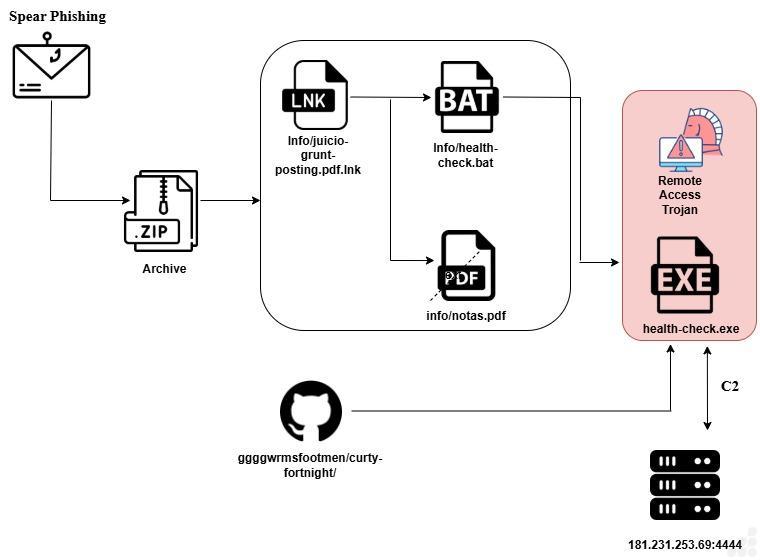
Lat61 Threat Intelligence uncovers a stealthy Rust RAT targeting Argentina's legal sector via weaponized judicial PDFs. Learn about its evasion tactics.
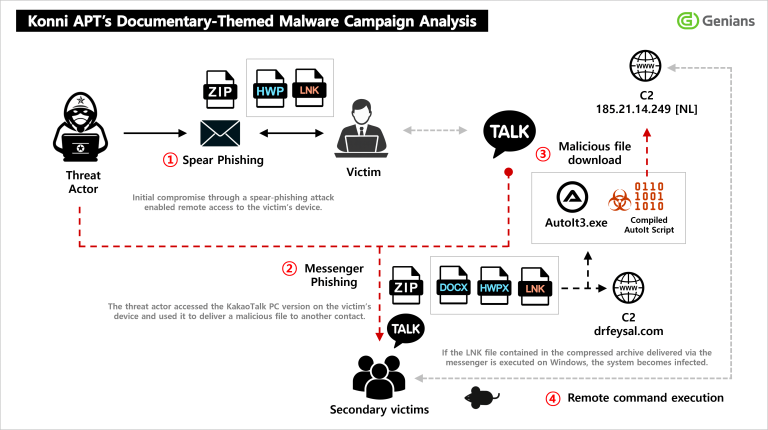
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.
Seqrite exposes "Operation Covert Access": A Rust RAT targeting Argentina's legal system via fake court rulings. Includes anti-analysis & encryption tools.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.

CYFIRMA exposes APT-36 weaponizing a fake NCERT WhatsApp advisory to deliver a stealthy backdoor and seize long-term control of government systems.

SHADOW-VOID-042 impersonated Trend Micro via fake security advisories to breach defense, energy, and chemical firms. Tactics align with Void Rabisu (ROMCOM), using HR lures and targeted exploits.
FortiGuard exposed UDPGangster, a custom UDP backdoor deployed by MuddyWater APT. The malware evades network defenses and analysis by using UDP for C2 and checking for single-core CPUs/low RAM.

SEQRITE exposed Operation DUPEHIKE targeting Russian HR with a malicious LNK bonus lure. The DUPERUNNER implant uses PowerShell and process injection into explorer.exe to deploy the Adaptix C2 Beacon.
Bloody Wolf APT is targeting Central Asia using custom Java droppers to deploy the NetSupport RAT. The group uses geo-fencing and fake Ministry of Justice lures to achieve stealthy, persistent access for espionage.

SEQRITE exposed CAPI, a .NET trojan targeting Russian FinTech with malicious LNK resumes. It uses rundll32 for execution and a hidden "Security" scheduled task for persistence.
Volexity found China-aligned APT UTA0388 used ChatGPT to generate multilingual spear-phishing lures and assist in GOVERSHELL malware development for espionage.

An Iranian state-aligned APT, Nimbus Manticore, is targeting European defense and telecom firms with sophisticated spear-phishing campaigns and new malware.

North Korean threat group Kimsuky is using AI-generated deepfakes in a new spear-phishing campaign, signaling a new frontier in cyber warfare.