 Do Son
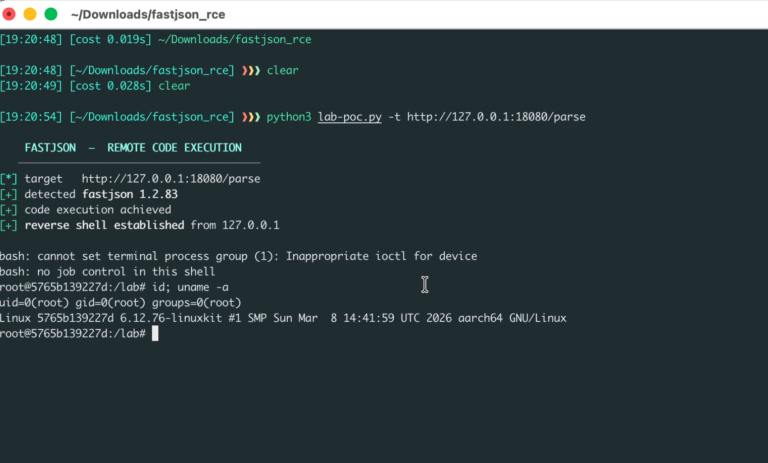
FastJson RCE vulnerability CVE-2026-16723 is exploited in the wild. Details and PoC exploit code are public for this critical remote code execution flaw.
Spring Boot
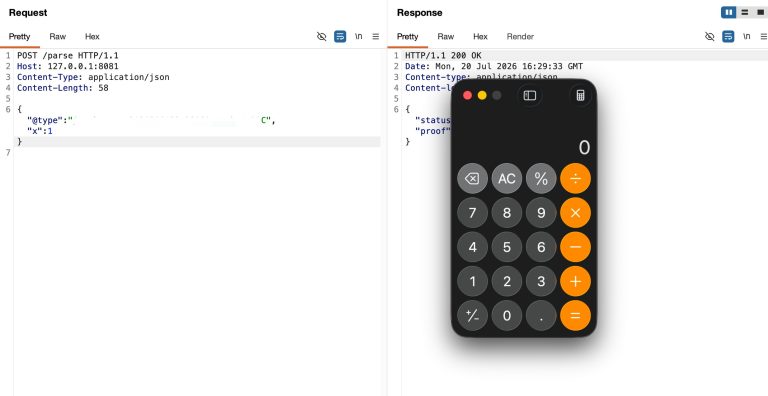
A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.
Spring Cloud Config fixes a 9.1 CVSS directory traversal (CVE-2026-40982) and a GCP secret leak. Secure your distributed system—upgrade to the latest patches!
New Spring Boot flaws (CVSS 9.1) bypass security filters and enable RCE via timing attacks. Impacting versions 2.7.x to 4.0.x—secure your Java apps now.
Two high-severity flaws (CVE-2026-22731 & CVE-2026-22733) in Spring Boot Actuators allow authentication bypass. Update your framework today to stay secure.

The CVE-2023-20883 vulnerability could trigger a DoS attack when Spring MVC is used along with a reverse proxy cache

CVE-2023-20873 affects multiple versions of Spring Boot, specifically 3.0.0 - 3.0.5, 2.7.0 - 2.7.10, and older unsupported versions