 Do Son
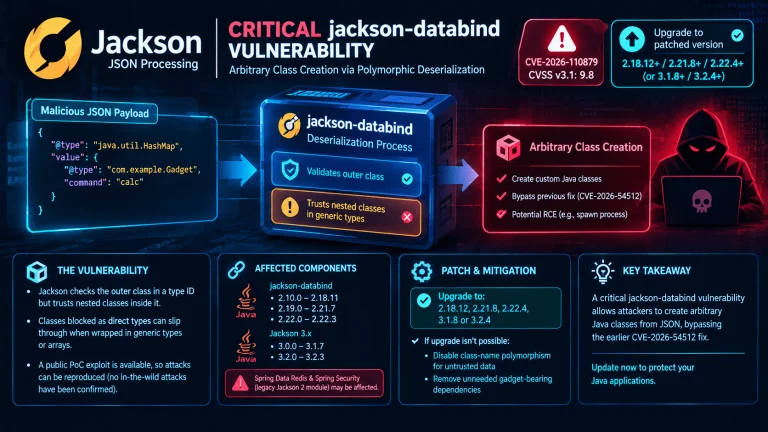
Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
Spring
Four Spring vulnerabilities hit Spring Data REST and Spring AI, including CVE-2026-47849, a privilege escalation flaw. Patch to the fixed versions now.

A critical flaw in Spring Cloud Gateway (CVE-2025-41243) has a CVSS 10.0 score. The bug allows property modification when actuator endpoints are exposed. Update now.