 Do Son
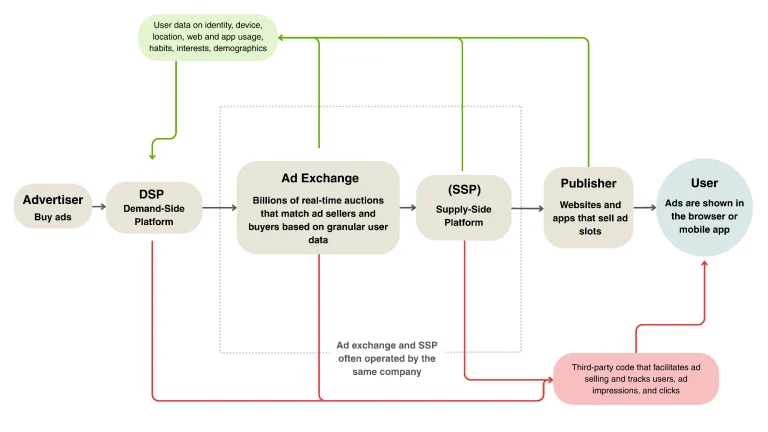
Citizen Lab exposes the AdFection spyware attack, a zero-click ad-bidding exploit that targeted at least 45 Al Jazeera devices.
spyware
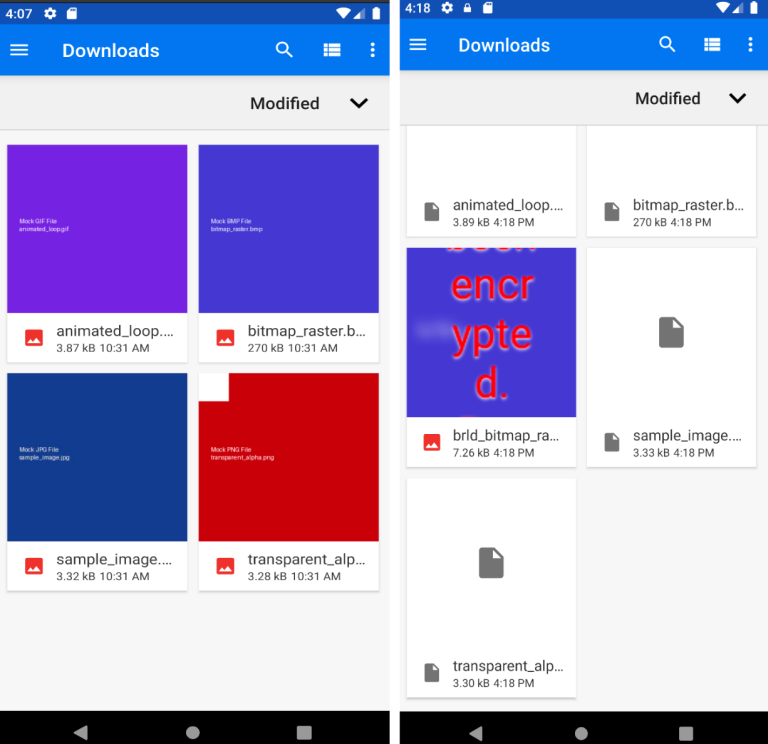
Zimperium zLabs discovered Mantax Otax Android malware, a fierce Indonesian mobile ransomware integrating spyware to hijack, record, and extort victims.
Python NodeStealer now adds keylogging, clipboard, and screenshot spyware plus dual Telegram C2. See how the NodeStealer spyware upgrade works.
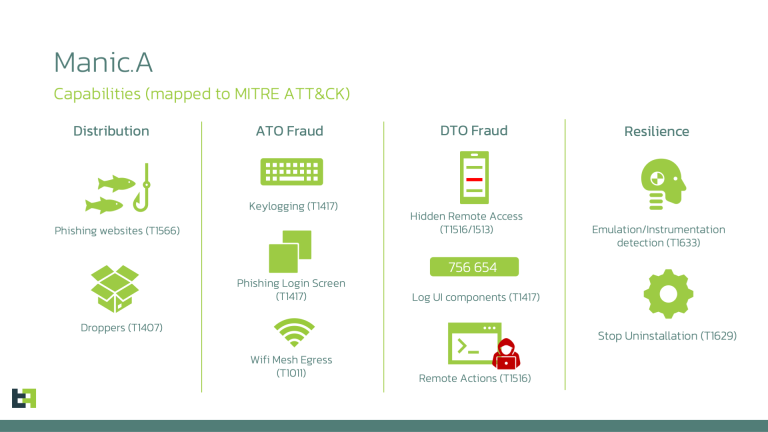
A new Manic Android malware campaign combines banking fraud and spyware, using a unique offline mesh relay to steal data even without internet access.

Apple has issued mercenary spyware attack warnings to users across 110+ countries, urging immediate security action and device hardening.

A Reddit user discovered hidden spyware in Claude Code that tracks users' locations, particularly targeting Chinese developers and proxy usage. Read more.
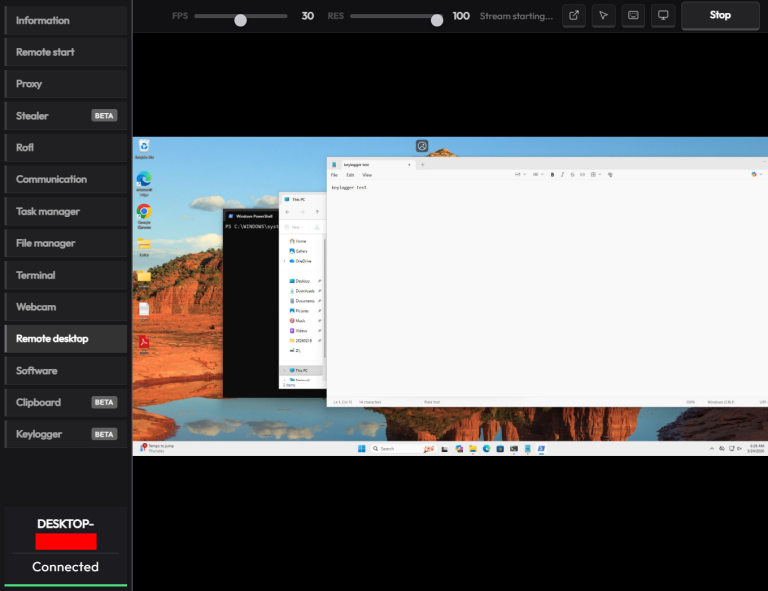
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?
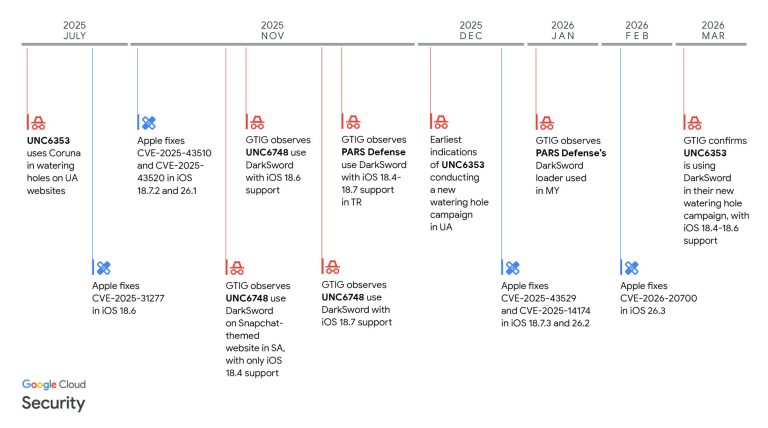
Google uncovers DarkSword, a sophisticated iOS full-chain exploit used globally to deploy spyware via zero-day vulnerabilities. Update to iOS 26.3 now.
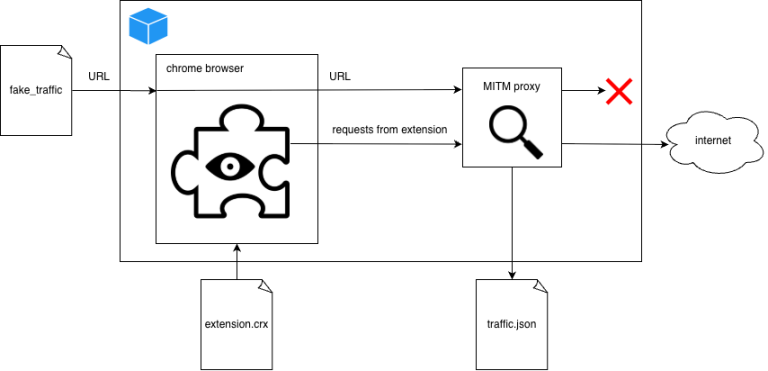
Q Continuum finds 287 Chrome extensions spying on 37M users. "Super PiP" & others exfiltrate history via Google Analytics. Check your browser now.
Urgent: Apple patches zero-day CVE-2026-20700 in dyld. The flaw is being exploited in the wild against specific targets. Update to iOS 26.3 now.

Jamf reveals Predator spyware's advanced anti-analysis tactics. It now detects Corellium, hides recording icons, and tracks why infections fail.

iVerify exposes Cellik, a $150/mo Android RAT that wraps malicious code inside Play Store apps to grant attackers total device control.

RSF uncovers ResidentBat, a Belarusian KGB spyware physically installed during interrogations to hijack encrypted messages and monitor journalists.

Frogblight, a new Android banking Trojan, is targeting Turkey via smishing with fake e-government apps. It uses WebView to steal credentials and is linked to the Coper MaaS family. It is being actively developed.

Koi Security exposed ShadyPanda, which infected 4.3M+ users by weaponizing trusted browser extensions (WeTab, Clean Master) through auto-updates. The malware performs RCE and exfiltrates data to China.

Unit 42 exposed LANDFALL, commercial-grade spyware that exploited a Samsung zero-day (CVE-2025-21042) in the image library libimagecodec.quram.so to compromise Galaxy phones via DNG images sent over WhatsApp.

Zimperium exposed Fantasy Hub, a Russian MaaS Android RAT. It uses a Telegram bot for subscriptions and WebRTC to covertly stream live video and audio, targeting Russian banks with dynamic overlays.

Kaspersky found a Chrome zero-day (CVE-2025-2783) and sandbox bypass being exploited by Operation ForumTroll to deploy Memento Labs (Hacking Team) commercial Dante spyware against Russian targets.

An iOS exploit developer was shocked to receive an Apple warning after being targeted by the same kind of state-sponsored mercenary spyware he researches.

Apple overhauled its Security Bounty program, offering a $2M base reward (up to $5M with bonuses) for zero-click exploits that match mercenary spyware attacks and bypass Lockdown Mode.

The US-sanctioned NSO Group, maker of Pegasus spyware, was acquired by an American investment firm for "tens of millions." The deal will keep operations in Israel but may lift sanctions.