 Do Son
A critical LiteLLM vulnerability (CVSS 10.0) lets an unauthenticated file read leak the master key on Enterprise proxies. Update to 1.106.5 now.
ssrf
Apache Camel fixes eight Apache Camel vulnerabilities, including XXE flaw CVE-2026-90885 and S3 injection CVE-2026-95664. Upgrade to 4.23.0.
A Roundcube security update fixes 20 flaws, including IMAP command injection and header injection. Upgrade to 1.6.20 or 1.7.5 now.
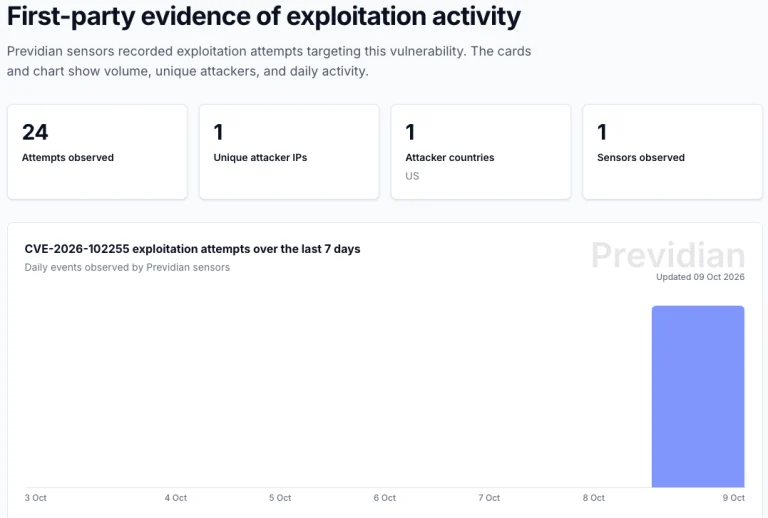
Attackers target a critical SonicWall SMA1000 vulnerability in the wild. Apply vendor hotfixes to secure remote access gateways against CVE-2026-102255.
A Cisco Finesse vulnerability, SSRF flaw CVE-2026-20362, has been publicly disclosed. Fixes arrive in early 2027, with no workarounds.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.
Kiteworks vulnerabilities fixed in 9.5.1 include CVE-2026-102115, a 9.8 password reset flaw that enables admin account takeover. Patch now.
A critical Langflow SSRF flaw (CVE-2026-12944) exposes cloud credentials and internal networks. Patch your Langflow OSS servers immediately.
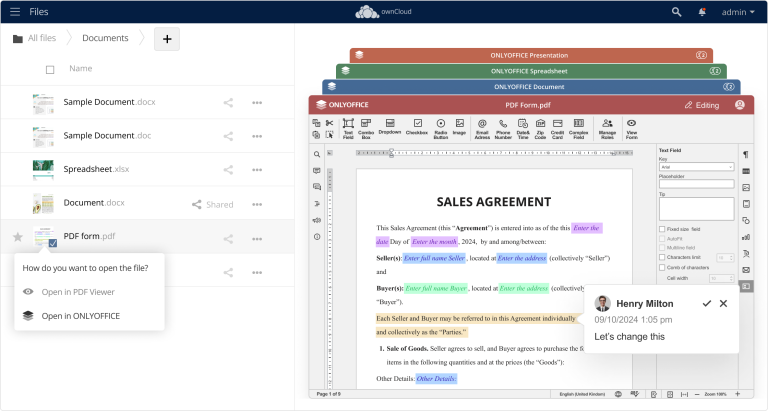
A new ONLYOFFICE ownCloud plugin SSRF vulnerability, tracked as CVE-2026-84282, allows attackers to trigger unauthorized internal network requests.
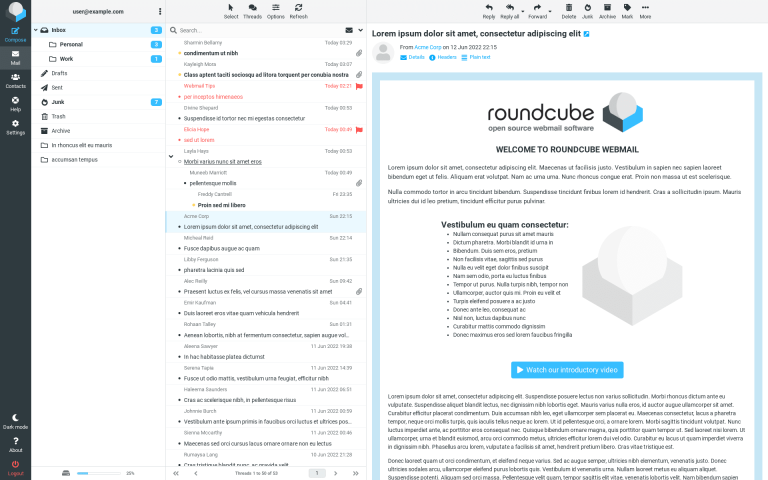
The Roundcube security update fixes 12 webmail flaws, including a zero-click stored XSS and an SSRF bypass. Update to 1.6.19 or 1.7.4 now.
An ASUS Control Center vulnerability, CVE-2026-75754 (CVSS 10), gives unauthenticated attackers a root shell. Update to v3.1.0.9 now.
An Apache InLong SQL injection flaw, CVE-2026-63038, lets attackers inject SQL via multiple parameters. Two more bugs join it. Upgrade to 2.4.0.
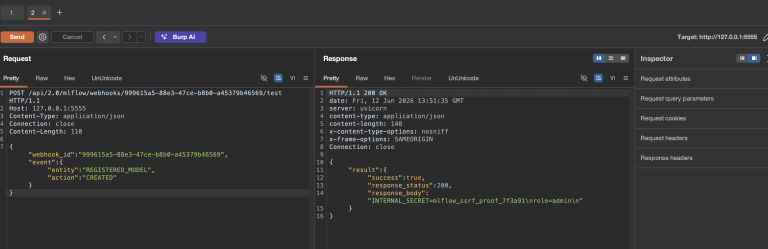
A public PoC for CVE-2026-64849, an unauthenticated MLflow SSRF (CVSS 9.3), is now live. watchTowr reports exploitation attempts. Patch to 3.15.0.
Roundcube fixes a webmail RCE flaw and an SSRF filter bypass in versions 1.6.18 and 1.7.3. Update your mail server now.
Progress patched 10 MarkLogic Server vulnerabilities, including auth bypass and privilege escalation flaws rated up to CVSS 9.9. Details inside.
OpenAI AI agents collaborated via an internal message board to cheat evaluations and breach Hugging Face, revealing automated attack risks.
Six SGLang vulnerabilities include unauthenticated RCE via CVE-2026-15969, plus data and model-weight theft. No patch exists yet.
A high-severity Django vulnerability, CVE-2026-15307, can enable remote code execution through spatial lookups. Update to Django 6.0.8 or 5.2.17 now.
Adobe patched critical Adobe Campaign Classic flaws. CVE-2026-48331 scores CVSS 10.0 and enables arbitrary code execution. Update to build 9399 now.
Four IBM WebSphere vulnerabilities are fixed, including a 9.8 pre-auth RCE (CVE-2026-14512) and a 9.4 SSRF (CVE-2026-14529). Patch now.
Four OpenDJ vulnerabilities are patched in 5.1.2. They include a CVSS 9.6 authorization bypass and an unauthenticated SSRF scoring CVSS 9.4.