
 Do Son
Spring Security reveals 7 flaws, including a critical 9.6 CVSS vulnerability in version 7.0. From auth bypass to X.509 impersonation, upgrade to 7.0.5 now.
ssrf

Angular patches a critical 8.7 SSRF flaw in @angular/platform-server. Attackers can hijack SSR origins via URL normalization. Patch v19, v20, or v21 now!

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!
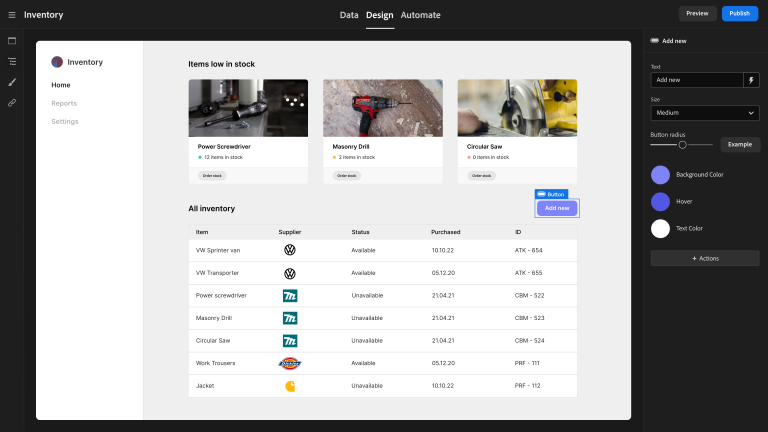
Critical 9.6 CVSS flaws in Budibase allow unauthenticated RCE and data exfiltration via SSRF. Secure your internal tools—update to v3.33.4 now.

Dgraph patches a critical 10.0 CVSS flaw (CVE-2026-33976). Unauthenticated attackers can overwrite databases and read local files. Update to v25.3.1 now!

Kyverno (CVE-2026-4789) faces an unpatched SSRF flaw in its CEL HTTP functions, allowing attackers to bypass K8s namespaces. Secure your cluster now!
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.
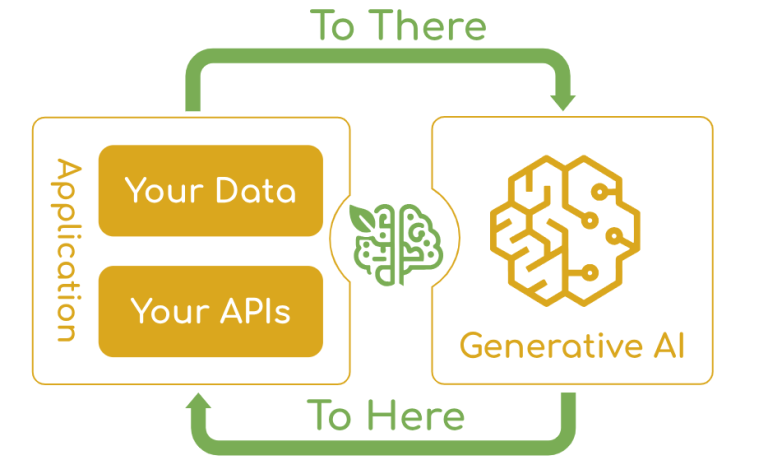
Spring AI patches critical 9.8 CVSS SpEL injection (CVE-2026-22738), SSRF, and Cypher injection flaws. Secure your AI applications—upgrade to 1.1.4 now.

Spring Cloud Config faces a high-severity CVSS 8.6 flaw (CVE-2026-22739). Attackers can manipulate profiles to access local files or launch SSRF attacks.
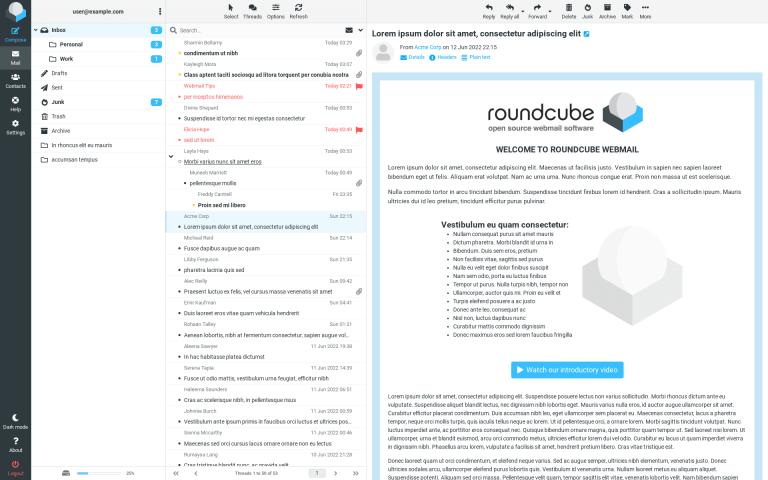
Roundcube v1.6.14 patches a critical pre-authentication file write flaw and account hijacking bugs. Secure your webmail server with this high-priority update.

Urgent: WordPress 6.9.2 patches 10 critical security flaws, including XSS, SSRF, and path traversal. Update your site immediately to prevent exploitation.
Angular patches a critical 9.2 CVSS SSRF vulnerability (CVE-2026-27739). Attackers can manipulate Host headers to steal credentials and probe internal networks.

TP-Link fixes critical IDOR (CVE-2025-9520) in Omada Controller allowing admins to hijack Owner accounts. Update now to prevent total network takeover.

Elastic patches 7 high-severity flaws (CVSS 8.6) in Kibana & Elasticsearch. CVE-2026-0532 allows SSRF & file theft. Update to v8.19.10 now.

Alert: Apache Struts 2 XXE flaw (CVE-2025-68493) exposes apps to data theft & DoS. Upgrade to v6.1.1 or apply JVM workarounds immediately.
CISA added a critical XXE flaw (CVE-2025-58360) in OSGeo GeoServer to the KEV Catalog. The actively exploited bug allows attackers to read arbitrary files and perform SSRF on internal networks. Patch immediately.

ZITADEL patched three high-severity flaws. Critical SSRF (9.3) allows internal breach via x-forward-host; XSS and Host Header Injection risk account hijack. Update to v4.7.1 immediately.
Apache HTTP Server 2.4.66 patched five flaws. Key fixes include a moderate SSRF flaw (CVE-2025-59775) that risks NTLM hash leakage on Windows, and a mod_userdir/suexec bypass. Update immediately.

GeoServer patched a High-severity XXE flaw (CVE-2025-58360, CVSS 8.2) in its WMS GetMap operation. The flaw allows unauthenticated remote attackers to read arbitrary files and perform SSRF. Update to v2.27.0.

Elastic patched two Kibana flaws: CVE-2025-59840 XSS via Vega visualizations and CVE-2025-37734 (SSRF) via the Observability AI Assistant. Update to v9.2.1 immediately.

Zimbra issued an emergency patch (v10.1.12) for a Critical SSRF vulnerability in the chat proxy that lets attackers manipulate internal server requests. Update is urged immediately.
Elastic patched five flaws in Kibana/Elasticsearch, including three Critical XSS issues (CVE-2025-25009) and credential leaks, urging immediate upgrades to v8.18.8+.