 Do Son
Go 1.27.4 and 1.26.11 deliver 12 Go security fixes, blocking cgo code execution at build time (CVE-2026-97033) and an HTTP/1 server crash.
Supply Chain Security
Composer 2.11.2 and 2.2.32 fix three Composer vulnerabilities, including command execution via a crafted composer.lock file (CVSS 8.8).
Won a contract but missing proof? Fast Cyber Essentials and a fast pen test help suppliers satisfy procurement without losing momentum.
Wiz Research uncovered the Gheist campaign, a Gheist GitHub campaign planting 13,500 rogue branches across 850+ accounts to steal private repo secrets.
GitHub now expires npm trusted publishing setups that miss a first publish within 48 hours, closing a repo name reuse flaw in 1,500+ packages.
A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
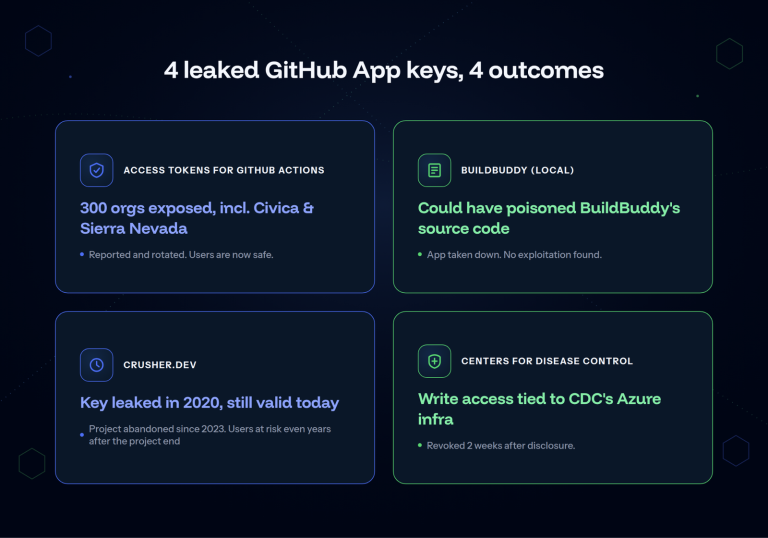
GitGuardian discovered 474 leaked GitHub App private keys still active. Learn how exposed GitHub App private keys threaten organizations like the CDC.
Microsoft will require a Windows driver SBOM and VEX statement for signing from March 2027, aligning WHCP with the EU CRA.
The Broadcom TrueSource project provides verified, secure, and commercially supported open-source software builds to combat supply chain attacks.

A distributed npm supply chain attack dropped a cross-platform RAT on Alibaba developers. Socket found malicious npm packages hiding loader code.

CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.

A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.
A decompress npm vulnerability (CVE-2026-53486, CVSS 9.1) lets crafted archives write files outside the target folder via path traversal. Patch now.

Python fixed a python.org authentication bypass in its release metadata API. The flaw, dormant since 2014, let attackers alter download URLs.
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!
Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.

Two critical CVSS 10.0 RCE flaws in Spinnaker's Clouddriver and Echo services allow full JVM and shell access. Patch your multi-cloud pipelines immediately.
Sonatype Nexus Repository (CVE-2026-5189) faces a critical 9.2 CVSS flaw. A hardcoded database credential grants full host access. Patch to v3.71.0 now!

Critical Remote Command Injection flaws in PHP Composer's Perforce integration (CVE-2026-40176 & CVE-2026-40261) could lead to full system compromise. Patch now.

April 2026 Alert: CPUID downloads for CPU-Z and HWMonitor were poisoned with STX RAT via DLL sideloading. Check your systems for CRYPTBASE.dll now!

Sonatype patches a critical 9.4 CVSS RCE in Nexus Repository 3 (CVE-2026-3199). Secure your supply chain—upgrade to version 3.91.0 immediately!

Node.js library basic-ftp patches a critical 9.1 CVSS path traversal flaw (CVE-2026-27699). Malicious FTP servers can overwrite any file on the client machine.