 Do Son
Microsoft ties a JADEPUFFER Azure attack to Storm-3168, the agentic ransomware actor that tried to delete 100+ storage accounts in seven minutes.
Sysdig
Sysdig documented JADEPUFFER, the first agentic ransomware run end-to-end by an AI agent. It breached Langflow via CVE-2025-3248 and extorted a database.
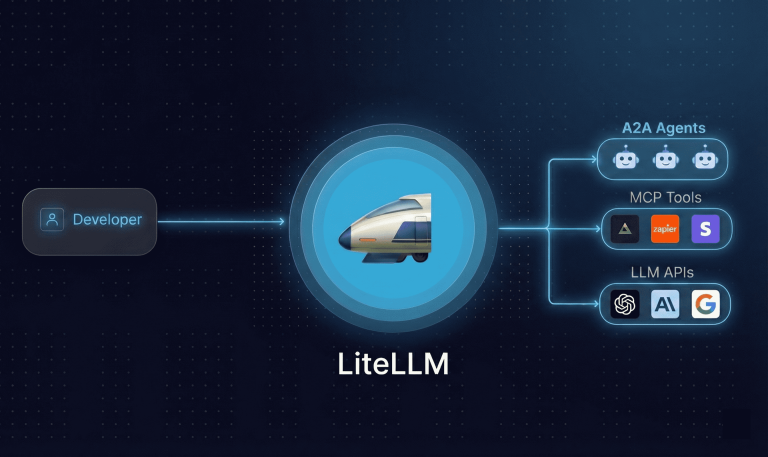
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.
Unauthenticated RCE in marimo (CVE-2026-39987) exploited in the wild in record time. Attackers gained root access in under 10 hours. Patch to v0.23.0 now!

Sysdig uncovers a campaign exploiting misconfigured Open WebUI instances to deploy AI-assisted cryptominers and infostealers, showcasing new threat vectors.