 Do Son
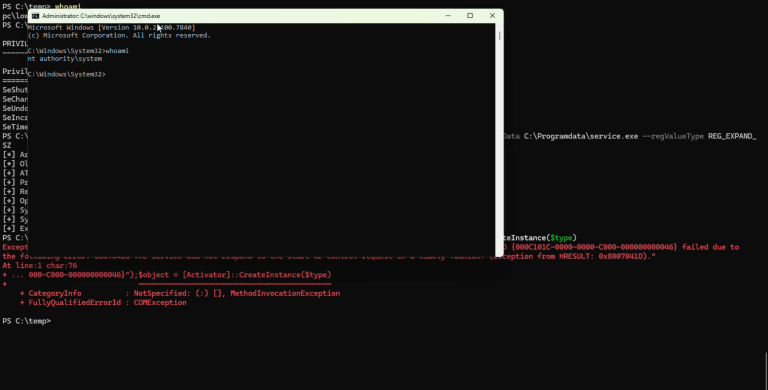
Exploit code and details for RegPwn (CVE-2026-24291) are publicly disclosed. The Windows local privilege escalation flaw grants attackers SYSTEM access.
SYSTEM access

ASUS urges users to patch a high-severity LPE flaw (CVE-2025-59373) in its System Control Interface Service, which allows low-privileged users to escalate to full SYSTEM control.

A flaw (CVE-2025-58726) allows SYSTEM privilege escalation via Kerberos authentication reflection using "Ghost SPNs" and disabled SMB signing. Patch immediately.

CVE-2025-49144 lets attackers gain NT AUTHORITY\SYSTEM via Notepad++ v8.8.1 installer flaw. PoC available—secure paths and signatures urged.
Weaponizing Group Policy: Custom Client-Side Extensions as a Stealthy Backdoor into Active Directory

Weaponizing Group Policy: Custom Client-Side Extensions as a Stealthy Backdoor into Active Directory
A new, stealthy AD persistence technique abuses custom Group Policy Client-Side Extensions (CSEs) for SYSTEM-level access. Learn how to detect it!
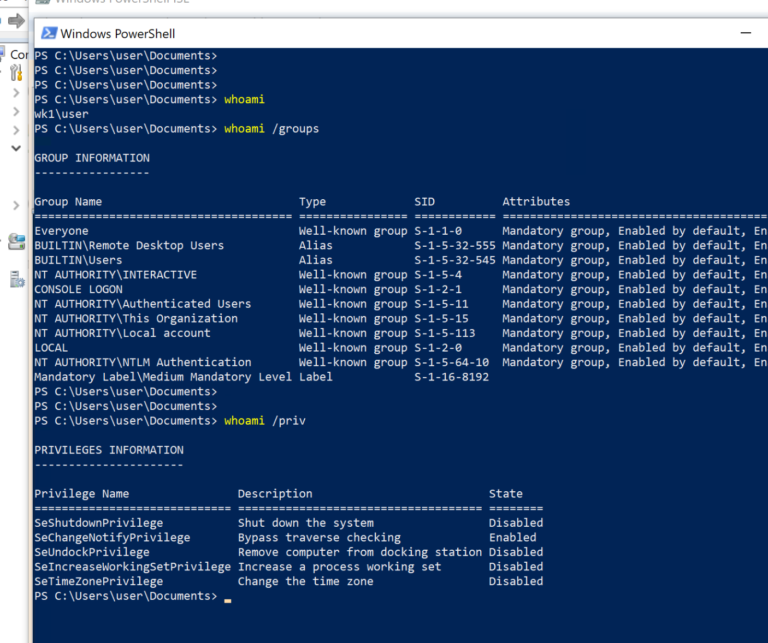
A critical flaw (CVE-2025-21204) in the Windows Update Stack allows local privilege escalation. Details and proof-of-concept exploit released.