
 Do Son
A public PoC for CVE-2026-66804 escalates a standard Windows user to SYSTEM via the Cross Device Service. Details and exploit code are now disclosed.
SYSTEM privileges

Details and proof-of-concept exploit code for CVE-2026-50343 are now public. The Windows privilege escalation flaw hands standard users SYSTEM privileges.
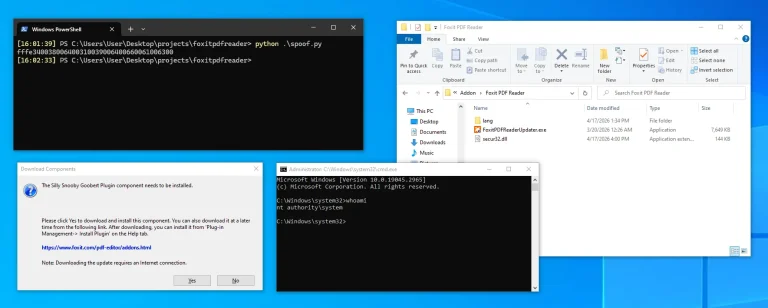
A public proof-of-concept for CVE-2026-57239 turns a Foxit PDF Reader vulnerability into full SYSTEM privileges via local privilege escalation.

Public PoC released for Windows Storage flaw CVE-2026-21508. Attackers can gain SYSTEM privileges via WUDFHost.exe. Patch Windows 11 immediately.

Exploit code released for Zabbix flaw CVE-2025-27237. Low-level users can gain SYSTEM privileges on Windows via OpenSSL config. Update now.

Public PoC released for Trend Micro Apex Central RCE (CVE-2025-69258). Unauthenticated attackers can gain SYSTEM access. Update to Build 7190 now.
Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)

Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)
Citrix warns of a high-severity local privilege escalation flaw (CVE-2025-6759, CVSSv4 7.3) in Windows VDA, allowing low-privileged users to gain SYSTEM access.

TeamViewer disclosed a high-severity flaw (CVE-2025-36537, CVSS 7.0) in its Remote Management for Windows, allowing local unprivileged users to delete files with SYSTEM privileges

A critical Windows SMB client flaw (CVE-2025-33073, CVSS 8.8) allows remote SYSTEM privilege escalation via Kerberos authentication. PoC available.

Zero-day CVE-2025-33073 allows remote privilege escalation to SYSTEM on Windows via SMB. PoC available. Fixed in June 10, 2025 Patch Tuesday.

Uncover a high-severity vulnerability in Windows 11: learn how local users can escalate their privileges through the CLFS driver.