 Do Son
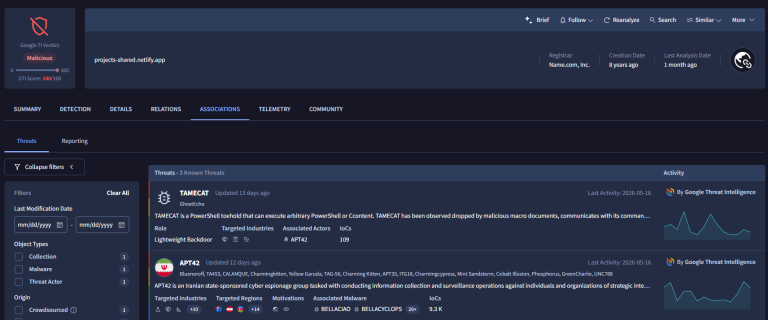
APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.
TA453
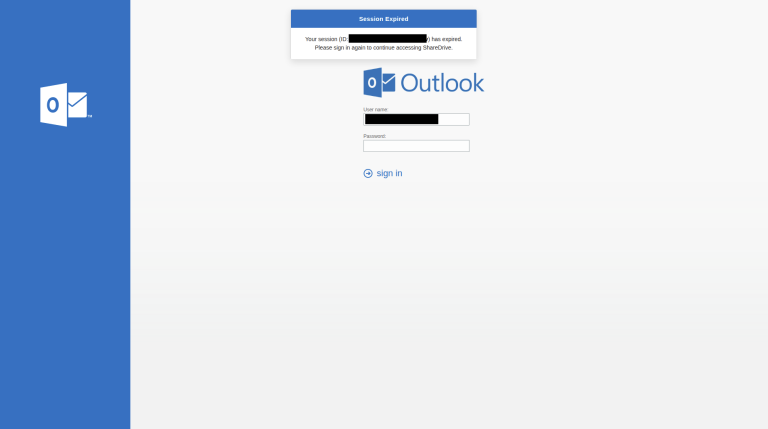
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.
Discover the sophisticated tactics used by the Iranian-backed threat actor TA453 in their latest phishing campaign. Learn how they impersonated a think tank to target a high-profile individual.

One notable aspect of CharmingCypress's tactics is their use of unusual social-engineering tactics in their phishing campaigns