 Do Son
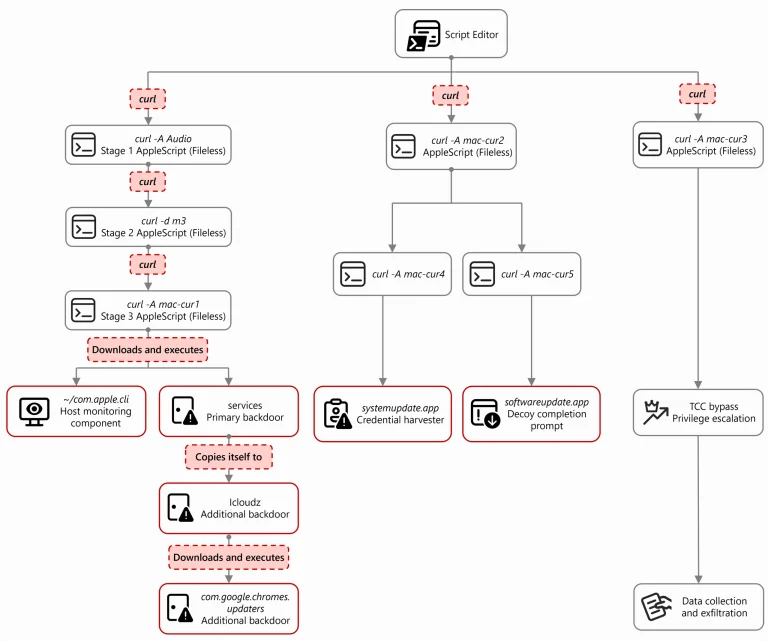
Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.
TCC Bypass

Darktrace finds Mac malware using a fake "Compatibility Wizard" to trick users. The AppleScript attack bypasses TCC to drop a Node.js backdoor.

Researcher Mickey Jin uncovers CVE-2025-43530, a critical TCC bypass in macOS allowing attackers to hijack user data via accessibility tools.

A critical flaw (CVSS 9.8) in macOS file copy APIs allows apps to bypass sandboxing and TCC protections to access protected user data. A PoC is public.

A critical macOS flaw (CVE-2025-24204) in gcore allows a user to read any process memory and bypass TCC. A PoC is public, and patching is urgent.

A critical flaw (CVE-2025-24103) in macOS InstallAssistant allows a normal user to bypass TCC, exposing private data. A PoC is public, urging users to update to 15.3.

Microsoft discovered "Sploitlight" (CVE-2025-31199), a macOS flaw exploiting Spotlight plugins to bypass TCC, leading to private data exfiltration, including Apple Intelligence cached info.

Discover the high-severity vulnerability CVE-2024-55950 in Tabby, a widely used terminal emulator for Windows, macOS, and Linux.