
 Do Son
A macOS ClickFix campaign now uses a browser fingerprinting gate to hide AMOS infostealer lures from researchers. See how it works.
TDS
ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.

Discover how malicious traffic routing hijacks open-source downloads in this new Check Point research report on global malware distribution.

Infoblox uncovers a novel phishing tactic abusing the .arpa TLD. Attackers hijack internet "plumbing" to bypass firewalls and deliver brand-impersonation scams.
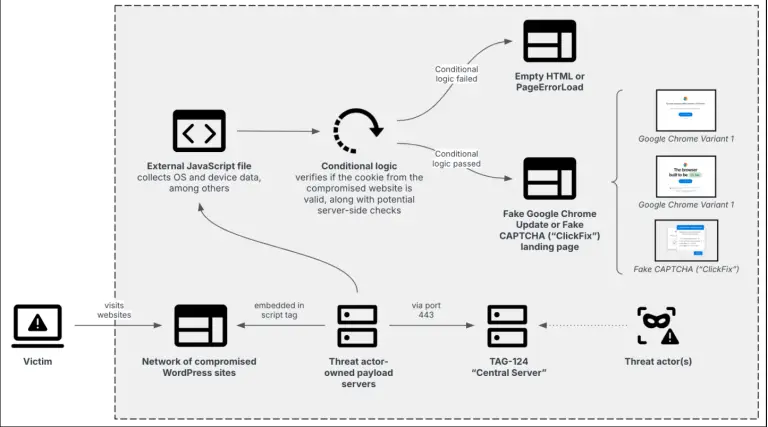
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.

Infoblox unmasks VexTrio, a sprawling malicious adtech ecosystem intertwined with DNS-based malware campaigns and global website compromises, fueled by commercial operators

HelloTDS is a sophisticated traffic direction system delivering millions to FakeCaptcha and other malware via advanced fingerprinting and evasive tactics.
Infoblox uncovers $5.7B lost to investment scams in 2024, driven by RDGAs, DNS abuse, and fake profit platforms run by sophisticated threat actors.