 Do Son
Discover the latest JetBrains software vulnerabilities, including TeamCity RCE bugs and Exposed SQLi flaws. Apply security patches immediately.
TeamCity
An unpatched JetBrains Cadence server exposed cloud infrastructure, AWS credentials, and critical developer secrets. Discover the details of this severe breach.
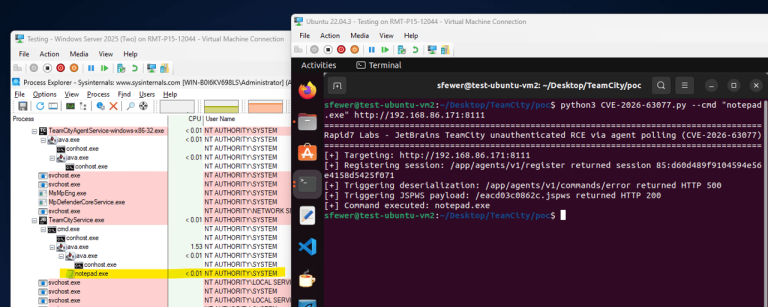
TeamCity CVE-2026-63077 enables unauthenticated remote code execution. Exploited in the wild with a public PoC. Patch your servers now.

CVE-2026-63077, an unauthenticated RCE in JetBrains TeamCity, is exploited in the wild. PoC exploit code and full details are now public.
CVE-2026-63077 is a critical TeamCity RCE rated CVSS 9.8. Unauthenticated attackers can run OS commands. Update TeamCity On-Premises to a fixed build.

JetBrains patched 18 vulnerabilities across its IDEs. CVE-2026-64812 and CVE-2026-64813 reach CVSS 10, and most of the rest allow arbitrary code execution.
JetBrains vulnerabilities patched: CVE-2026-62422 (CVSS 10) YouTrack authentication bypass, IntelliJ IDEA RCE CVE-2026-59792, and four TeamCity flaws.
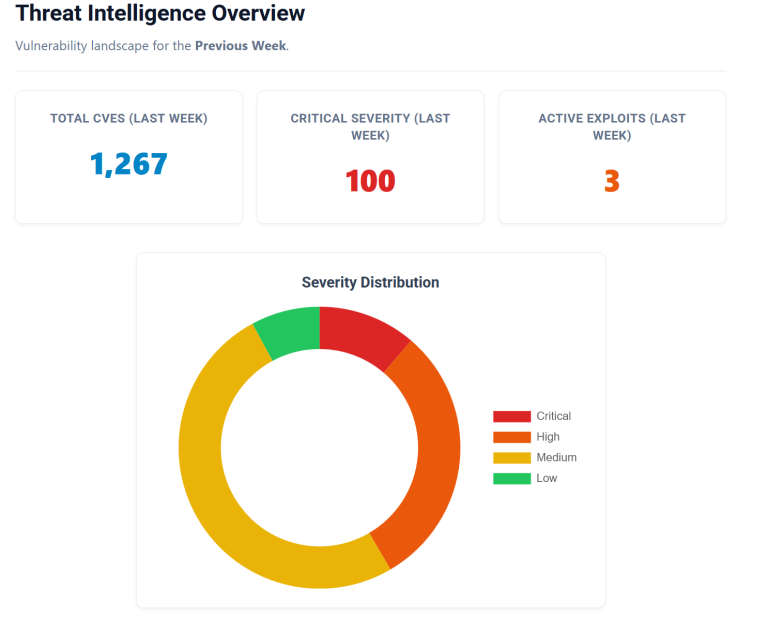
Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20,Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20, 2026. 2026.

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

Wiz Research Team uncovers rapid exploitation of exposed JDWP interfaces, deploying XMRig cryptominers in TeamCity and other Java environments within hours of exposure.

JetBrains TeamCity has been found to contain a high-severity security vulnerability (CVE-2024-41827, CVSS 7.4).

A wave of cyberattacks is crashing down on organizations using the TeamCity CI/CD platform, exploiting recently disclosed vulnerabilities

The vulnerabilities, identified as CVE-2024-27198 and CVE-2024-27199, expose the underbelly of TeamCity's security mechanisms