 Do Son
Discover the details of the TeamPCP hackers arrested in Australia for executing devastating open-source supply chain attacks using the Mini Shai-Hulud worm.
TeamPCP
The FBI issued an alert about a TeamPCP supply chain attack. The group uses malicious code to conduct a software supply chain compromise against developers.
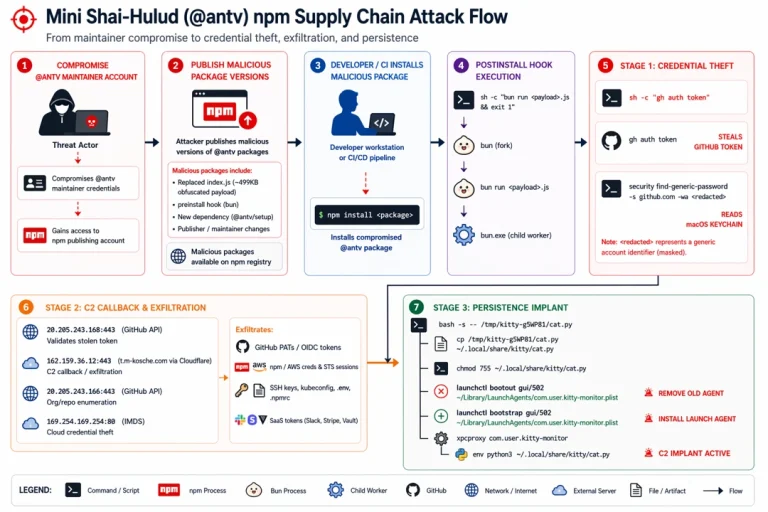
Microsoft warns of an aggressive Mini Shai-Hulud worm attack targeting the @antv npm ecosystem and stealing secrets from cloud-connected CI/CD pipelines.
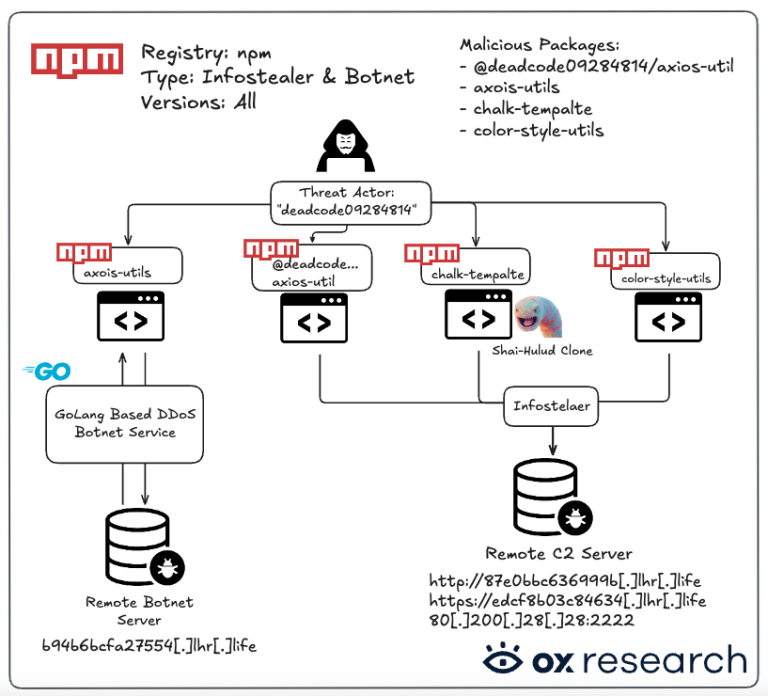
TeamPCP has open-sourced the Shai-Hulud supply chain worm. Multiple malicious typosquatted NPM packages are already weaponizing the AI-synthesized code.
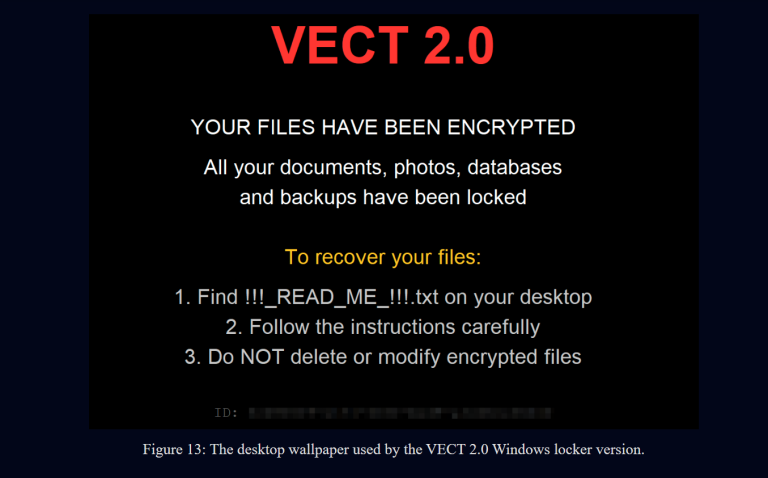
Check Point Research reveals VECT 2.0 ransomware is a broken wiper. A critical flaw makes file recovery impossible for files over 128KB. Read the analysis.
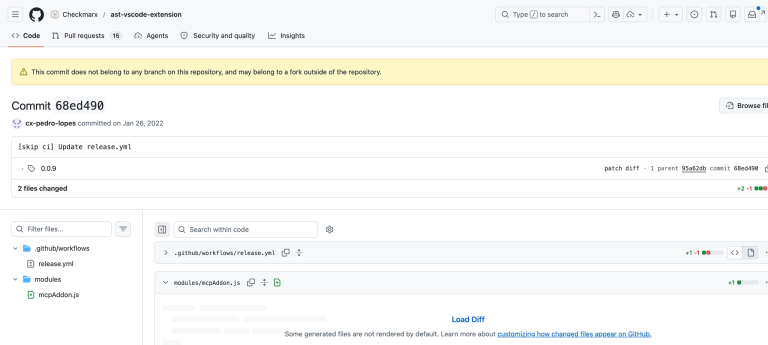
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
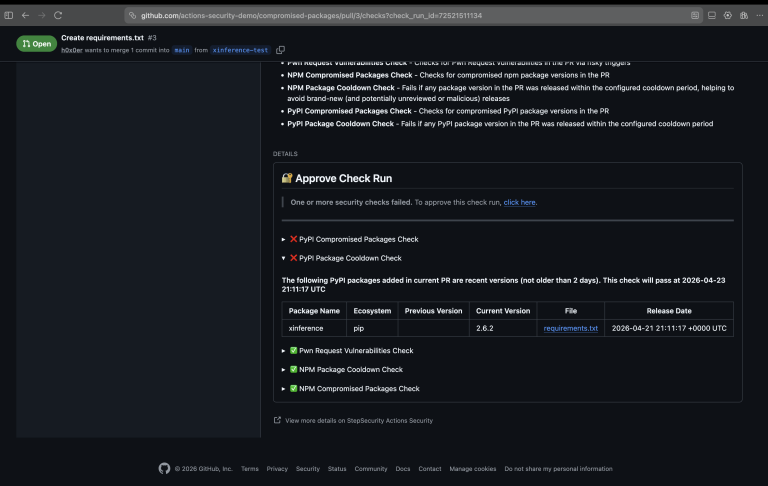
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.

A massive supply-chain attack hit the European Commission via a compromised Trivy update. 340GB of data was leaked by ShinyHunters. Rotate your AWS keys!
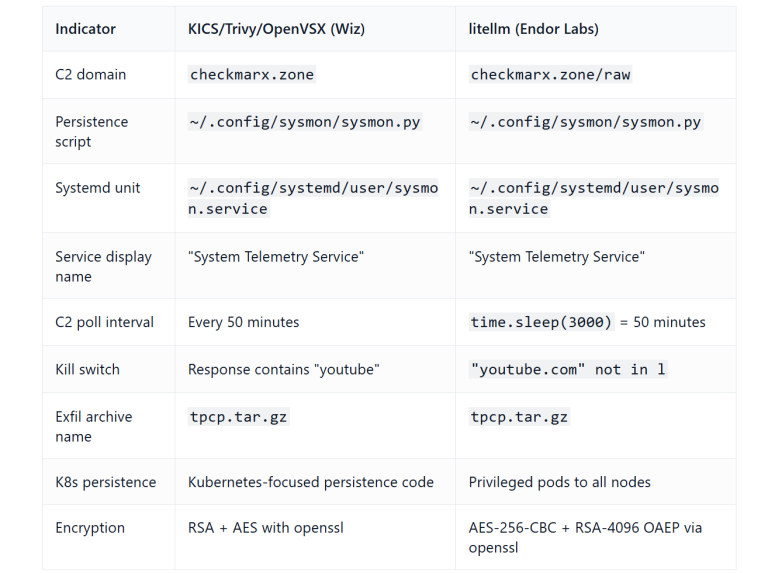
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.