 Do Son
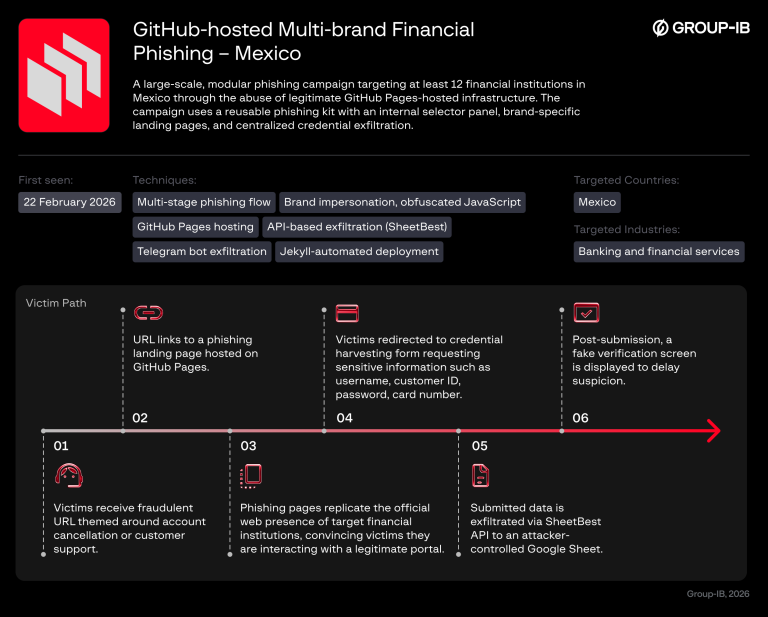
The GitBait phishing campaign abuses GitHub Pages and the SheetBest API to steal banking credentials from at least 12 Mexican financial institutions.
Telegram bot
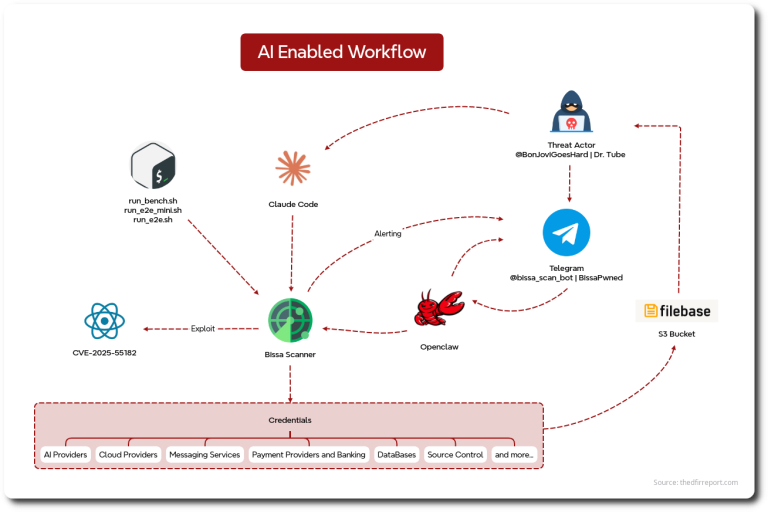
Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.

Sophisticated phishing abuses Vercel Blob & PDFs to bypass filters. Stolen credentials are exfiltrated via Telegram bots. Learn how to spot this attack.

Researcher Anurag uncovers a WordPress phishing campaign that steals credit cards and 3-D Secure OTPs, exfiltrating data directly via Telegram bots.

Group-IB uncovers "Wonderland," a bidirectional Android SMS stealer in Uzbekistan that uses Telegram droppers to drain bank accounts and hijack sessions.

Zimperium exposed Fantasy Hub, a Russian MaaS Android RAT. It uses a Telegram bot for subscriptions and WebRTC to covertly stream live video and audio, targeting Russian banks with dynamic overlays.

Imperva uncovered a PyPI supply chain attack: "cloudscrapersafe" disguised as a legitimate Python library, stealing credit card data and exfiltrating it to a Telegram bot.

Attackers exploit fake AI video tools to deploy Noodlophile Stealer and XWorm, stealing credentials and data via Telegram bots.

New lightweight PupkinStealer malware silently steals browser data, messaging sessions, and desktop files, sending it all via Telegram.

Uncover the details of Xiū Gǒu, a new phishing kit targeting organizations in the public sector, postal, digital services, and banking sectors.