 Do Son
ThreatFabric uncovers the Hirudo banking trojan. The Android Hirudo banking trojan replaces real banking apps with patched copies to steal funds.
ThreatFabric
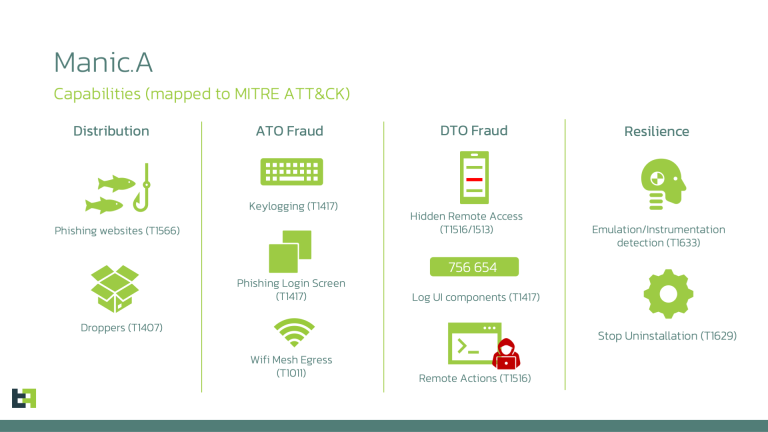
A new Manic Android malware campaign combines banking fraud and spyware, using a unique offline mesh relay to steal data even without internet access.
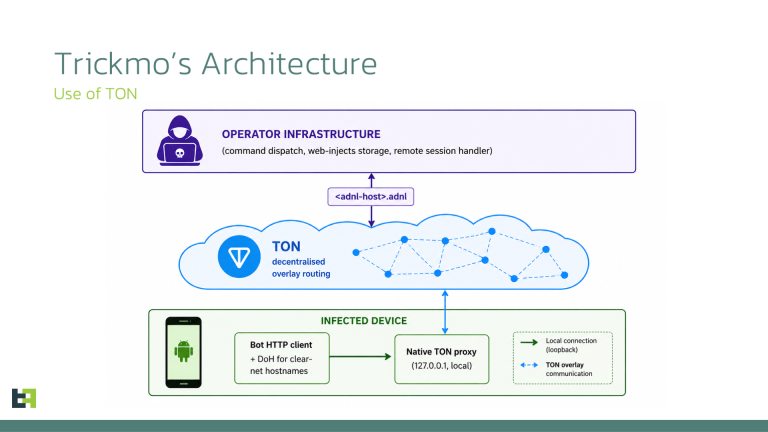
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
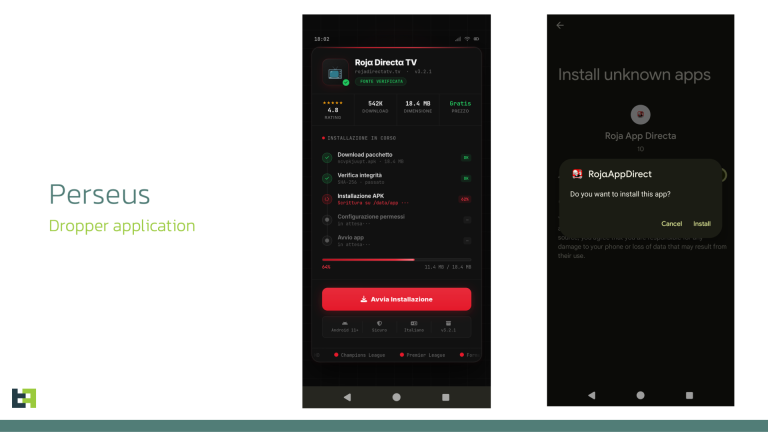
ThreatFabric uncovers "Perseus," an evolved Android malware targeting note-taking apps to steal recovery phrases and private data via accessibility services.
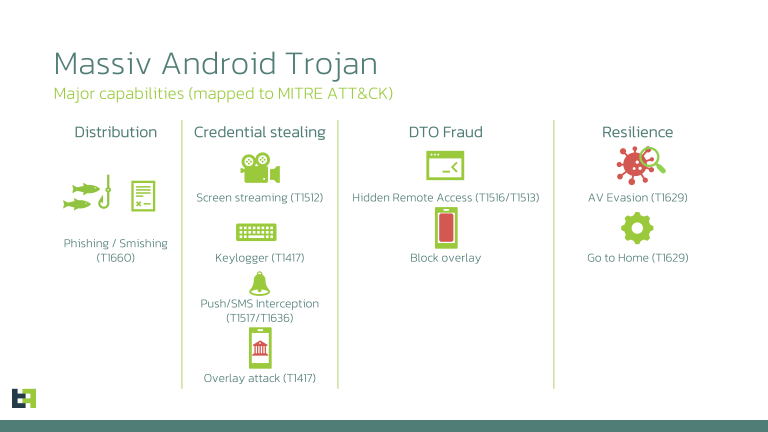
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

The new Sturnus Android banking trojan bypasses end-to-end encryption on WhatsApp & Signal and enables full device takeover for hidden financial fraud.

The Datzbro Android Trojan is targeting seniors via fake Facebook groups and AI content. The hybrid malware can remotely control devices and steal banking credentials.

A new Android banking trojan, RatOn, merges overlay fraud with NFC relay attacks, automated money transfers, and crypto wallet theft, posing a new threat to users.

ThreatFabric researchers have uncovered PhantomCard, an Android Trojan that uses an NFC relay attack to steal contactless card data and enable fraudulent payments.

Anatsa, an advanced Android banking trojan, is targeting North America via Google Play. It steals credentials and conducts remote fraud through disguised apps and overlay attacks.

Crocodilus, a rapidly evolving Android banking trojan, now targets global users, stealing crypto seed phrases and bypassing defenses.