 Do Son
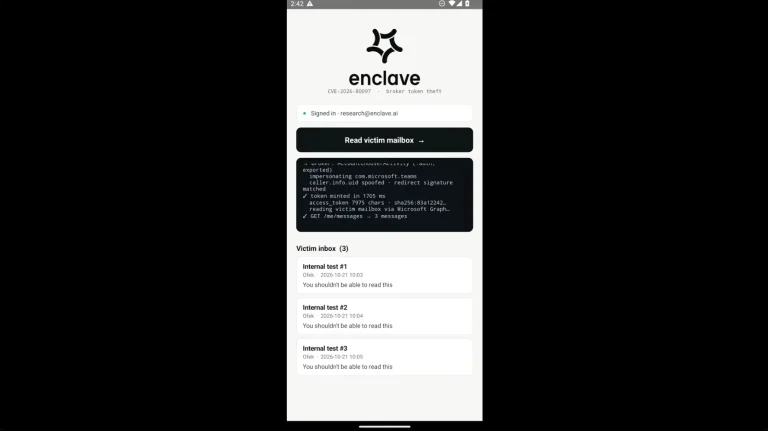
The Microsoft Authenticator AuthMask flaw allowed rogue Android apps to impersonate trusted software and hijack enterprise tokens and passkeys.
Token Theft
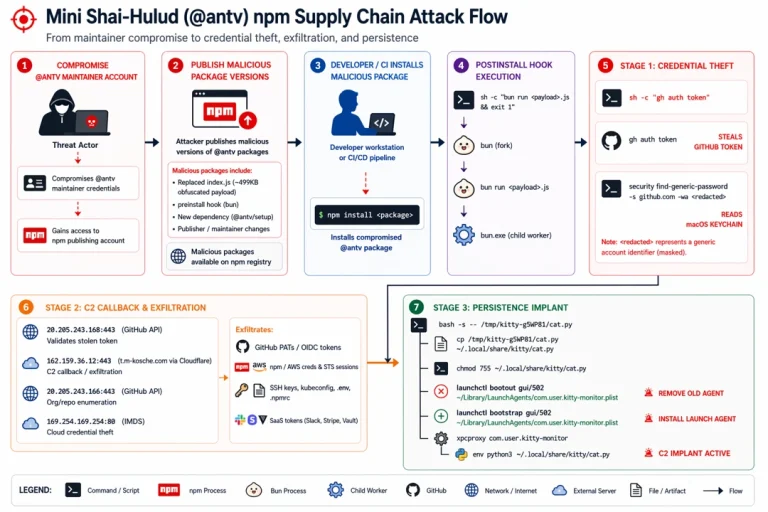
Microsoft warns of an aggressive Mini Shai-Hulud worm attack targeting the @antv npm ecosystem and stealing secrets from cloud-connected CI/CD pipelines.
Coder patches a critical 9.1 CVSS signature bypass (CVE-2026-46354) in Azure identities that allows unauthenticated workspace token theft. Patch now!

Keycloak 26.5.7 fixes an MFA bypass that could let attackers skip two-factor checks. Upgrade your identity server to close the gap.

GitLab fixes critical CVE-2025-7659 (CVSS 8.0). Unauthenticated attackers can steal tokens via Web IDE. Update to v18.8.4 now to secure your code.

Proofpoint warns of a surge in device code phishing where attackers abuse Microsoft 365 OAuth flows to hijack accounts and bypass MFA.

ASUS has patched two high-severity flaws (CVE-2025-4569, CVE-2025-4570) in MyASUS, stemming from insecure token storage that could lead to unauthorized access. Update immediately!

Socket discovered 10 malicious npm packages from Toptal's GitHub, exfiltrating GitHub tokens and wiping systems. The compromise vector is under investigation.

Beware of the malicious PyPI package targeting Discord developers. Learn how typosquatting can lead to token theft and backdoor installation.