
 Do Son
CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!
Trojan

Kaspersky reveals a fileless Trojan campaign targeting Proxifier searches. Learn how this "ClipBanker" hijacks crypto wallets via search engine poisoning.

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.

Malwarebytes uncovers a trojanized FileZilla campaign using DLL hijacking and DNS-over-HTTPS to silently steal FTP credentials and bypass security.

Warning: 7zip [.] com has been hijacked to spread residential proxy malware. Learn how to identify this 7-Zip impersonator and protect your system.
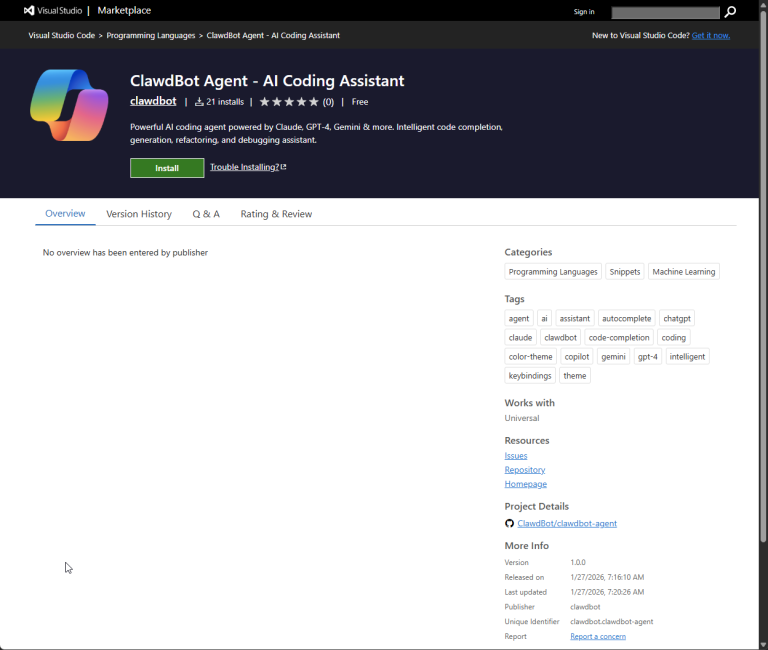
Malicious "ClawdBot Agent" VS Code extension exposed. Functioning as a real AI tool, it silently dropped malware. Microsoft removed it after 21 installs.

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.

ThreatFabric researchers have uncovered PhantomCard, an Android Trojan that uses an NFC relay attack to steal contactless card data and enable fraudulent payments.

Kaspersky exposes Efimer, a new crypto-stealer using fake legal threats and malicious torrents from compromised WordPress sites to hijack wallets and brute-force other sites.

IBM X-Force exposes CastleBot, a new MaaS framework that deploys infostealers and backdoors like NetSupport and WarmCookie via trojanized installers and phishing.

A critical server-side template injection flaw (CVE-2024-23692) in Rejetto HFS 2.x is actively exploited to deploy ransomware and trojans at scale. Update or retire the service immediately.

SentinelOne uncovers a new macOS.ZuRu variant using a trojanized Termius app. It gains persistence via LaunchDaemon and deploys a Khepri C2 beacon for remote control.

SonicWall and Microsoft uncover a campaign distributing a trojanized NetExtender VPN client that steals credentials by bypassing certificate validation.

AntiDot, an Android trojan from LARVA-398, is infecting thousands of devices via MaaS, using MediaProjection API and Accessibility Services to steal financial and personal data.

A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.

New email campaign uses tricky tactics and legitimate services to deliver the RATty Trojan in Spain, Italy, and Portugal. Stay alert for invoice scams!

Attackers are using SourceForge to distribute malware, including a ClipBanker Trojan and a cryptocurrency miner, disguised as a Microsoft Office enhancement suite.

The Grandoreiro banking trojan is being spread through phishing campaigns. Learn about the attack methods and how to stay safe.

A new banking Trojan named "CarnavalHeist" is targeting Brazilian users, exploiting the country's festive spirit to steal financial data
A potent new banking trojan dubbed "Coyote" is sweeping through Brazil's financial sector, prompting urgent warnings