 Do Son
Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.
unauthenticated RCE
CVE-2026-73749, a critical HPE AOS-CX vulnerability, enables unauthenticated remote code execution at CVSS 9.8. HPE patched 31 flaws across its switches.
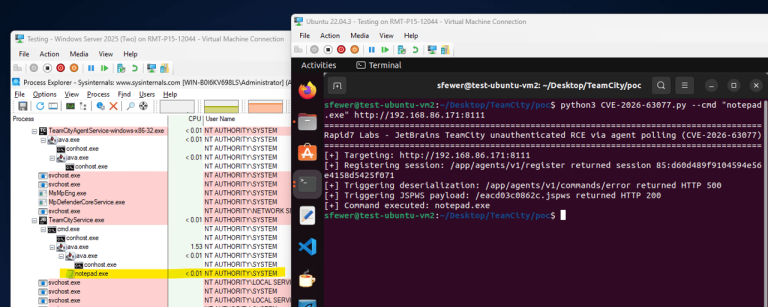
TeamCity CVE-2026-63077 enables unauthenticated remote code execution. Exploited in the wild with a public PoC. Patch your servers now.

Six SGLang vulnerabilities include unauthenticated RCE via CVE-2026-15969, plus data and model-weight theft. No patch exists yet.

A TP-Link TL-WR940N flaw, CVE-2026-12935, allows unauthenticated remote code execution via an RTSP stack buffer overflow. Update the router firmware now.

ManageEngine fixed an ADAudit Plus vulnerability, CVE-2026-6516, a CVSS 10 unauthenticated remote code execution flaw. Update to build 8606 now.

Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.

A critical Langflow RCE vulnerability (CVE-2026-10561) scores CVSS 10 and enables unauthenticated remote code execution. Upgrade to 1.9.4 now.

Urgent: Drupal releases patches for highly critical SQLi flaw CVE-2026-9082. Unauthenticated attackers can exploit PostgreSQL backends for full remote RCE.

A critical 9.8 CVSS flaw (CVE-2026-29058) in AVideo-Encoder allows unauthenticated remote attackers to execute arbitrary system commands. Patch now.
A critical 10.0 CVSS unauthenticated RCE flaw (CVE-2026-20131) in Cisco Secure FMC allows hackers root access via insecure Java deserialization. Patch now.
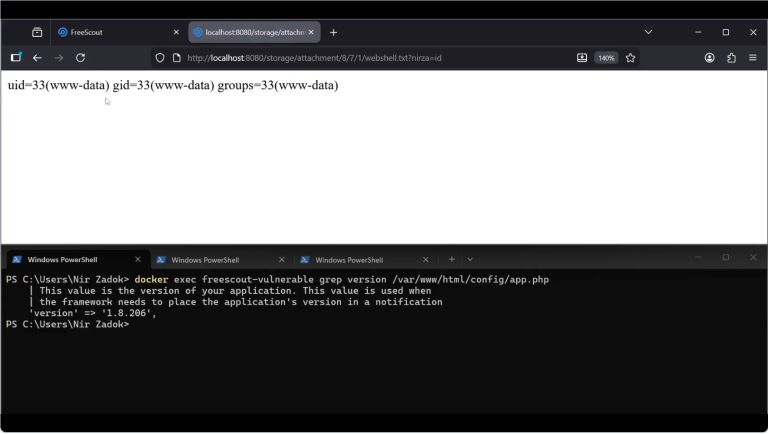
A critical 10.0 CVSS unauthenticated remote code execution flaw (CVE-2026-28289) in FreeScout allows full server takeover via an invisible character exploit.

Ivanti confirms critical EPMM RCE flaws (CVE-2026-1281) are exploited in the wild. Unauthenticated attackers can compromise MDM. Patch immediately.

A Critical RCE flaw (CVE-2025-6389) in Sneeit Framework is under active exploitation. The bug allows unauthenticated attackers to run arbitrary PHP code via call\_user\_func(). 131K+ attacks blocked.

A Critical (CVSS 9.8) RCE flaw in Sneeit Framework is actively exploited. The bug allows unauthenticated attackers to run arbitrary code via call_user_func and take over WordPress sites. Update to v8.4 immediately.

Cybersecurity firms warn of a Critical, actively exploited FortiWeb flaw that allows unauthenticated attackers to create a new administrator account on the FortiWeb Manager panel. Update to v8.0.2 immediately.

Zoho issued an urgent patch for a Critical (CVSS 9.8) Unauthenticated SQL Injection flaw (CVE-2025-8324) in Analytics Plus. The bug risks remote query execution and account takeover. Update to Build 6171.

Oracle's October CPU fixes 374 flaws, including two Critical RCE bugs (CVSS 9.8) in EBS Marketing. The vulnerabilities allow unauthenticated takeover of the application.

CVE-2024-7399 vulnerability actively exploited in Samsung MagicINFO 9 Server allows remote code execution. Arctic Wolf reports in-the-wild attacks. Upgrade now!