 Do Son
Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.
Unit 42

Unit 42 exposes CL-STA-1087, a suspected Chinese state-sponsored cyber espionage group using custom backdoors to infiltrate Asian military networks.
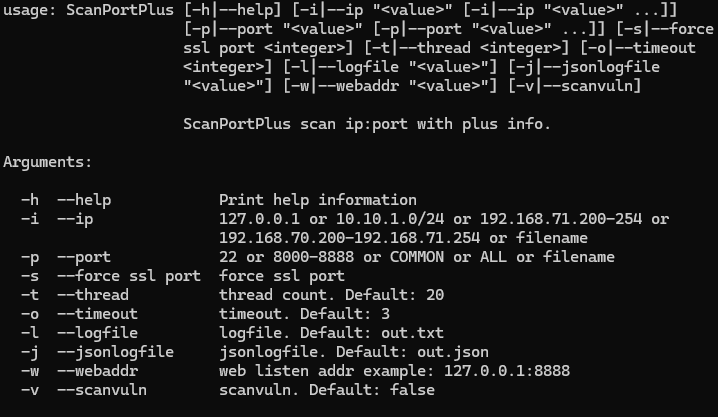
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Unit 42 reveals the first real-world cases of Indirect Prompt Injection (IDPI), where hackers weaponize website content to bypass AI security filters.

Unit 42 details the cyber fallout of Operation Epic Fury. Despite internet blackouts, autonomous hacktivists claim breaches of Israeli defense networks.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.

Ivanti EPMM under attack via zero-days CVE-2026-1281 & 1340. Hackers use bash scripts to plant dormant backdoors. Patch immediately.
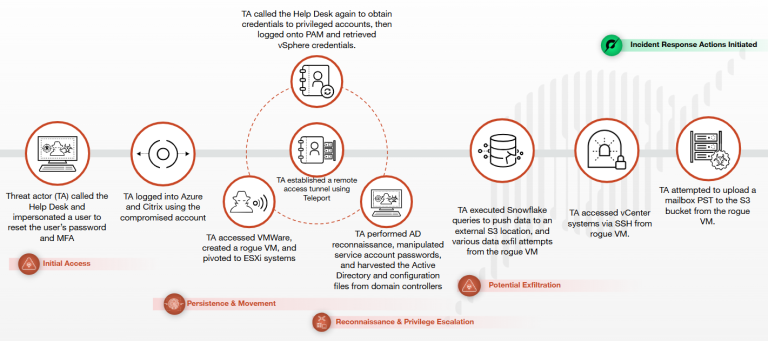
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

TGR-STA-1030 (UNC6619) hits 70+ orgs in 37 countries. The Asia-based group uses the new ShadowGuard eBPF rootkit to hide in Linux kernels.

Unit 42 reveals "living" phishing pages built by GenAI on the fly. These polymorphic attacks evade detection by generating unique code for every victim.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

Jolly Scorpius has upgraded its Mario ransomware with multi-layered, dual-key encryption and dynamic chunking to bypass recovery and lock down data.

Unit 42 reveals how malicious LLMs like WormGPT 4 and KawaiiGPT weaponize AI to automate ransomware and phishing, democratizing cybercrime for all.

Unit 42 exposed two massive campaigns (Trio & Chorus) using 2,500 spoofed domains to target Chinese users. The multi-stage attack uses MSI/VBScript and DLL sideloading via Avast to deploy Gh0st RAT.

Unit 42 exposed LANDFALL, commercial-grade spyware that exploited a Samsung zero-day (CVE-2025-21042) in the image library libimagecodec.quram.so to compromise Galaxy phones via DNG images sent over WhatsApp.

Unit 42 exposed the Smishing Triad, a PhaaS network that registered 194K+ malicious domains for global smishing. The group impersonates postal/banking services and uses Telegram for its underground market.

Unit 42 exposed Scattered LAPSUS$ Hunters pivoting to Extortion-as-a-Service (EaaS) after Salesforce leaks. The group is recruiting insiders and teasing SHINYSP1D3R ransomware on Telegram.

Unit 42 uncovers Phantom Taurus, a new Chinese APT using the fileless NET-STAR backdoor to target SQL databases and IIS servers in global espionage campaigns.
AdaptixC2, a new open-source hacking tool, is being abused by threat actors. The stealthy framework has been used in attacks, with some loaders likely AI-generated.
A new report reveals a critical flaw in the AI supply chain where attackers can hijack model namespaces on Hugging Face to deploy malicious models on major cloud platforms.

A new report reveals a stealthy attack on GeoServer using a critical RCE flaw. Instead of ransomware, attackers are hijacking servers to earn passive income.

A new report from Unit 42 reveals how cybercriminals are misusing generative AI to create realistic phishing sites, deepfake content, and fraudulent websites.