 Do Son
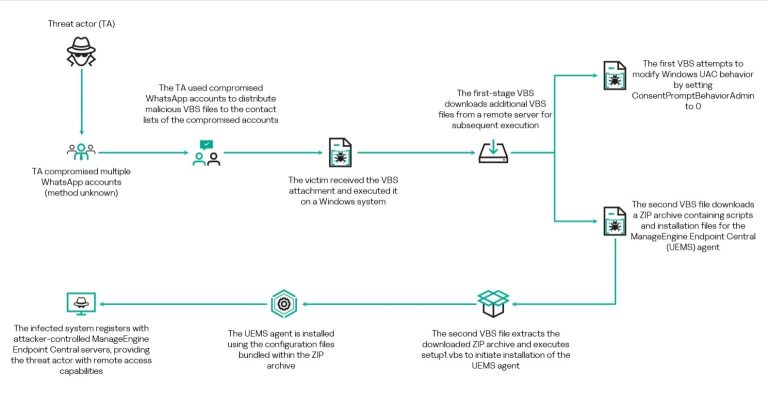
A new WhatsApp malware campaign uses a multi-stage VBScript infection chain to silently install RMM software on victim devices across multiple countries.
VBScript
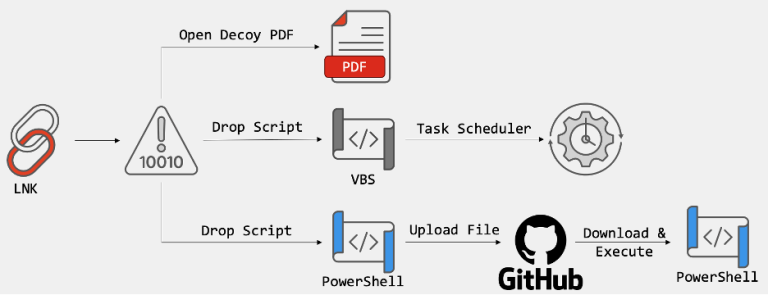
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.

ASEC uncovers Kimsuky’s evolved LNK-to-Python chain abusing Dropbox for stealthy persistence. Learn how to detect this complex multi-stage backdoor.
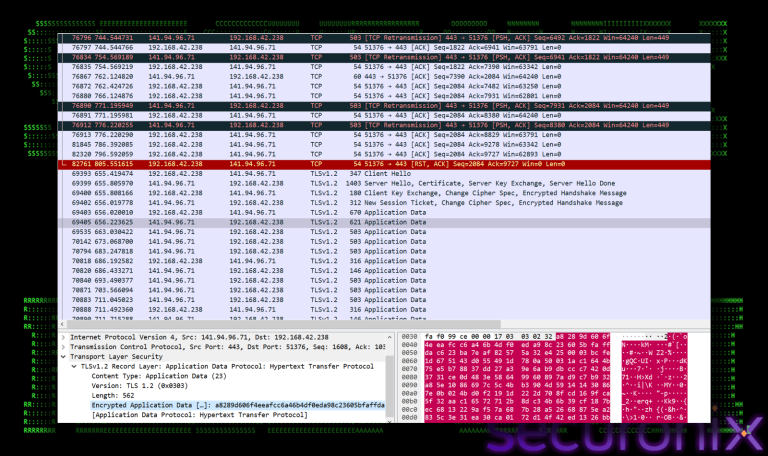
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.
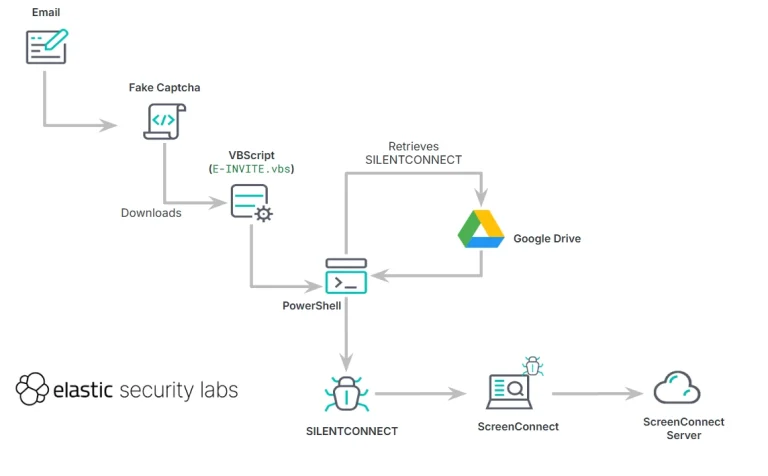
Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.

Sophos exposed STAC3150, a campaign using fake "View Once" messages to deploy Astaroth banking trojan. The malware hijacks WhatsApp Web sessions via WPPConnect/Selenium for self-propagation.

Unit 42 exposed two massive campaigns (Trio & Chorus) using 2,500 spoofed domains to target Chinese users. The multi-stage attack uses MSI/VBScript and DLL sideloading via Avast to deploy Gh0st RAT.

BitSight uncovered a Lampion banking Trojan campaign using ClickFix lures and a 700MB bloatware DLL to evade AV. The VBScript loader establishes persistence via the Windows Startup folder.

After almost 30 years, Microsoft is retiring VBScript. The legacy language will be phased out of Windows by 2027, posing a challenge for enterprises.

A new campaign uses encrypted VBScript (.VBE) to deploy a fileless Masslogger infostealer, which hides in the Windows Registry to steal credentials and evade antivirus.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

Unit 42 uncovers a sophisticated Lampion malware campaign using ClickFix social engineering tactics to target government and financial sectors in Portugal.

HarfangLab analysis details Gamaredon's PteroLNK malware, revealing its stealthy tactics and infrastructure used for espionage.

Japanese organizations are being targeted by the notorious North Korean advanced persistent threat (APT) group, Kimsuky

One of the most notable aspects of CLOUD#REVERSER is its use of Google Drive and Dropbox for C2 communication and data exfiltration