 Do Son
Veeam fixes seven vulnerabilities in Veeam Backup for Microsoft 365 and Management Pack, including RCE flaws CVE-2023-22793 and CVE-2026-106076.
Veeam
Patch 5 Veeam vulnerabilities in Veeam Backup & Replication and Veeam ONE, including critical flaw CVE-2026-108142 and MFA bypass CVE-2026-107671.
Critical Veeam Backup vulnerability CVE-2025-64393 (CVSS 9.4) enables RCE by low-privileged users. Update to 12.3.2 P4 now.
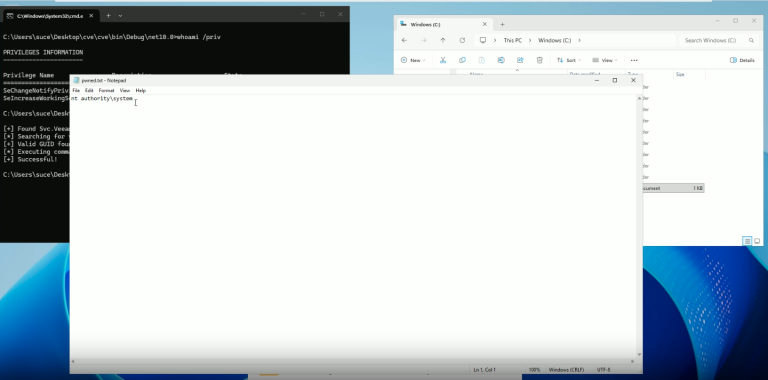
A critical exploited Veeam Agent vulnerability (CVE-2026-32996) is under active attack. Public PoC exploit code has been disclosed. Update systems now.
A critical Veeam ONE vulnerability (CVE-2026-65641, CVSS 9.3) lets an unauthenticated attacker coerce SMB authentication. Patch Veeam now.

A critical Veeam ONE vulnerability, CVE-2026-64633, allows remote unauthenticated code execution at CVSS 10.0. Update to build 13.1.0.7034 now.

A critical Veeam Service Provider Console flaw lets attackers steal agent credentials, while a second enables remote code execution. Update to 9.3 now.
A critical Veeam Backup vulnerability (CVE-2026-44963) allows remote code execution. Patch immediately to avoid ransomware targeting CVE-2023-27532.
Learn about the new Veeam security vulnerabilities, including a critical 9.4 RCE flaw in Service Provider Console, and how to patch your systems.

Veeam updates Backup & Replication v13 to fix high-severity flaws. CVE-2025-59470 and others allow RCE and root access. Update to build 13.0.1.1071.

Veeam released a critical update for Backup & Replication, patching three flaws, including a CVSS 9.9 RCE (CVE-2025-23121) allowing authenticated users to execute code.

Learn about CVE-2025-23120, a critical vulnerability in Veeam Backup & Replication with severe implications for enterprises.

Stay vigilant against the critical vulnerability (CVE-2025-23114) affecting Veeam backup and replication products. Learn how to secure your data and prevent potential attacks.
Stay informed about the critical CVE-2024-42448 vulnerability in Veeam's Service Provider Console (VSPC). Understand the risks and take necessary security measures.

Discover Frag ransomware, a newly observed threat exploiting a vulnerability in Veeam backup servers. Learn about its unique tactics and how to protect yourself.

Protect your enterprise from ransomware attacks exploiting Veeam Backup & Replication vulnerability. Patch and fortify your systems now!

To complicate matters further, a proof-of-concept (PoC) exploit for CVE-2024-40711 has been made publicly available on GitHub.
Veeam, a prominent backup and disaster recovery solutions provider, has recently addressed a critical vulnerability (CVE-2024-29855)
The impact can be significant, particularly for flaws CVE-2024-29849 and CVE-2024-29850, which allow unauthorized access and account takeover
CVE-2024-29212 carries a high severity rating with a CVSS score of 8.8, primarily due to its potential to allow remote code execution (RCE)

Carbanak malware, previously utilized for stealing banking data, is now employed by the cybercriminal group FIN7 for remote control