 Do Son
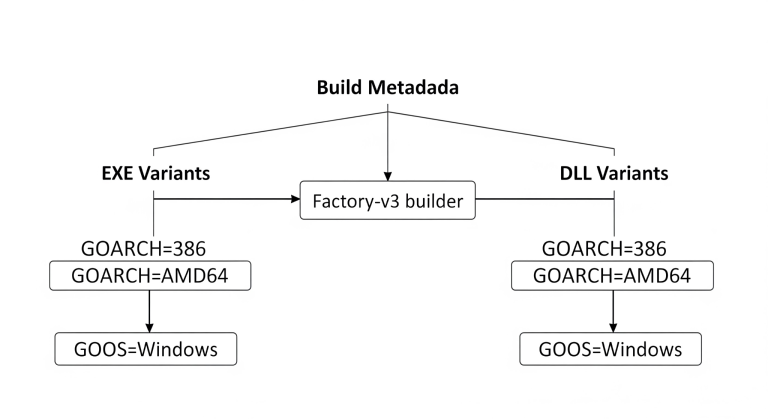
A new Vidar stealer campaign uses the Factory-v3 loader and fake certificates to deploy malware. Learn how attackers hide XMRig and bypass security.
Vidar Stealer
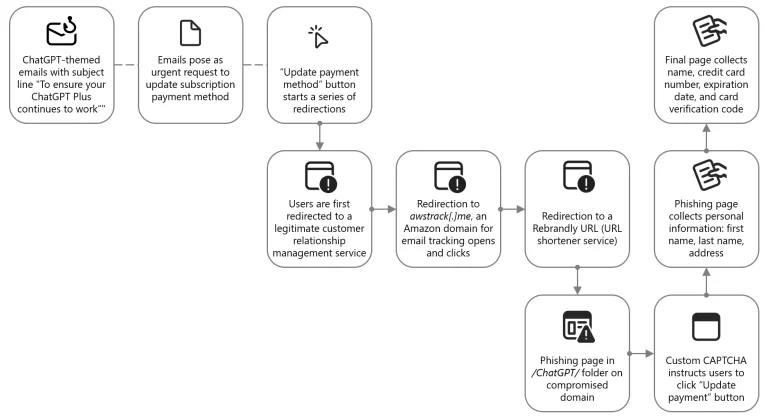
Threat actors are using AI social engineering lures to distribute malware and steal credentials. Learn how fake ChatGPT and DeepSeek campaigns work.
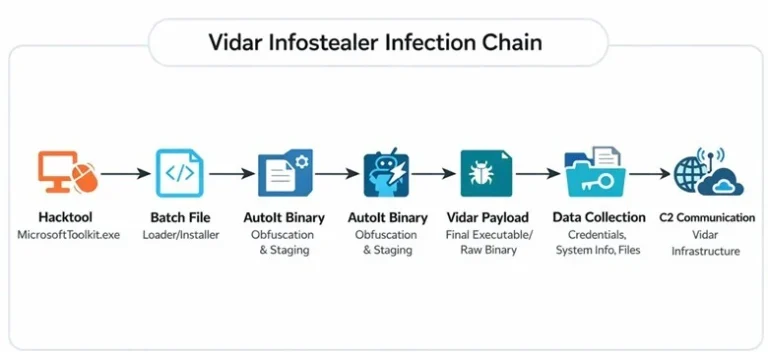
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?
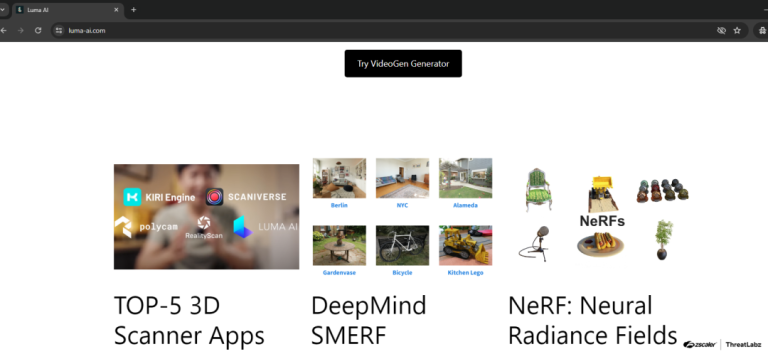
A sophisticated campaign is exploiting AI tool popularity via Black Hat SEO to poison search results, delivering Vidar, Lumma, and Legion Stealers to unsuspecting users.

Vidar Stealer malware is distributed by masquerading as BGInfo.exe, exploiting expired signatures and file discrepancies to evade detection

TRU has unveiled a sophisticated attack campaign utilizing counterfeit KMSPico activators to deliver the notorious Vidar Stealer malware

In a disturbing trend uncovered by Bitdefender Labs, malicious actors are weaponizing the growing fascination with AI to spread sophisticated malware
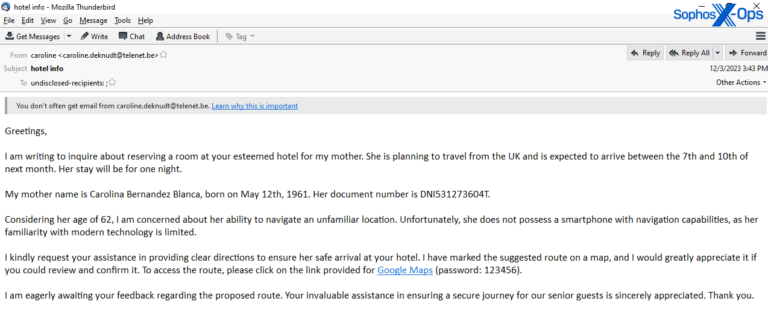
Sophos X-Ops warns that the "Inhospitality" malspam campaign represents a cunning blend of social engineering and malware