 Do Son
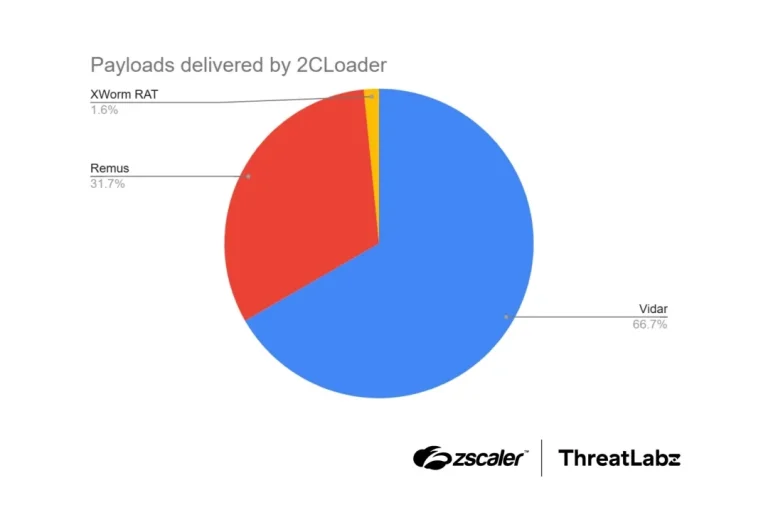
2CLoader malware dodges sandboxes and security tools to deliver Vidar and Remus infostealers. See how it works and how to detect it.
Vidar
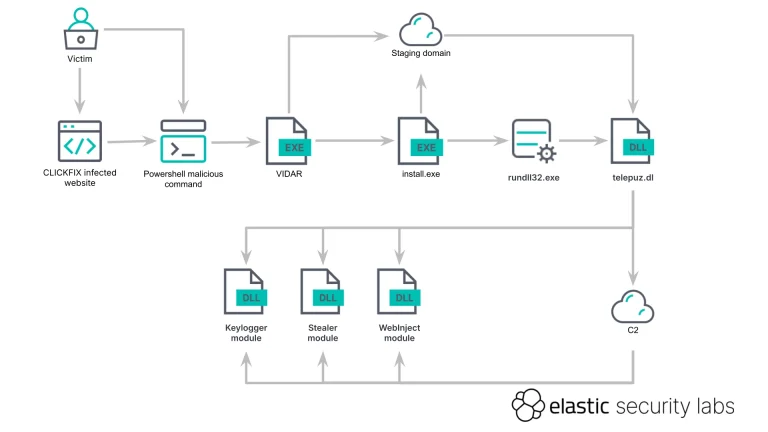
Elastic Security Labs found TELEPUZ malware spreading via a ClickFix attack chain. The modular MaaS uses WebSockets and blockchain C2 fallback.
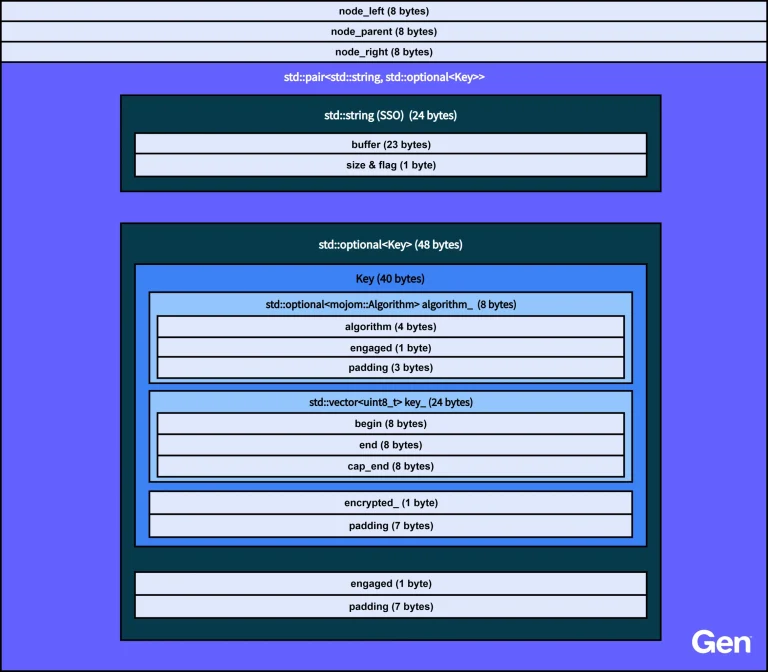
Gen Digital uncovered a new Vidar ABE bypass technique. The Vidar infostealer malware now uses memory scanning and APC injections to extract browser keys.
ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.
GoFlateLoader malware, a Golang loader, uses a giant PE overlay to evade scanners and deliver infostealers like Lumma, Vidar, and StealC.
Netskope exposes Hologram: a red-team-grade malware framework targeting OpenClaw AI users with CLR injection and WinLogon hijacking to steal crypto wallets.
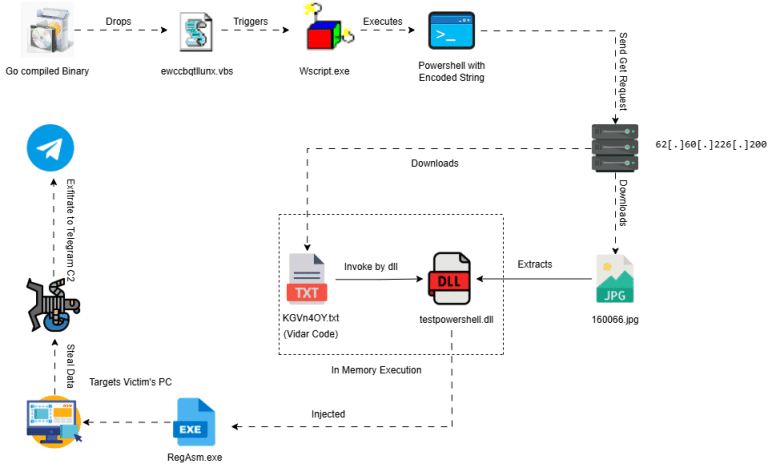
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.

Datadog exposed MUT-4831, a cluster that deployed Vidar Infostealer via 17 malicious npm packages. The malware uses postinstall scripts to download and execute the payload, stealing credentials and crypto wallets.

The new infostealer Acreed is rapidly gaining market share post-Lumma takedown. It uses BNB Smart Chain and Steam profiles for C2, with a focus on crypto theft.

AI-generated TikTok videos are instructing users to run PowerShell commands, leading to the delivery of Vidar and StealC infostealer malware.

Uncover a sophisticated malware campaign using GitHub's release infrastructure to distribute the dangerous Lumma Stealer Trojan. Learn more.

Beware of cracked software and fake installers. Discover how cybercriminals exploit user trust and spread malicious payloads.

Discover RiseLoader, a new malware family focused on efficient payload delivery. Get insights into its origins, similarities with RisePro, and advanced anti-analysis measures.
Learn about the concerns surrounding Chrome's App-Bound Encryption and the decryption of protected keys by a newly released open-source tool.

Learn about the latest threat to cybersecurity: infostealers that can bypass Chrome's App-Bound Encryption and compromise user data privacy.

Tracked as UNC5537, this financially motivated threat actor has systematically compromised hundreds of Snowflake customer accounts

The campaign exploits GitHub, a legitimate platform for software development, to distribute various malware families

threat actors are targeting consumer users, particularly younger audiences drawn to popular video games, by promoting cracked software