 Do Son
Discover how the PREY-0058 extortion campaign uses Microsoft 365 vishing attacks and AiTM tactics to bypass MFA, steal cloud data, and demand high ransoms.
Vishing
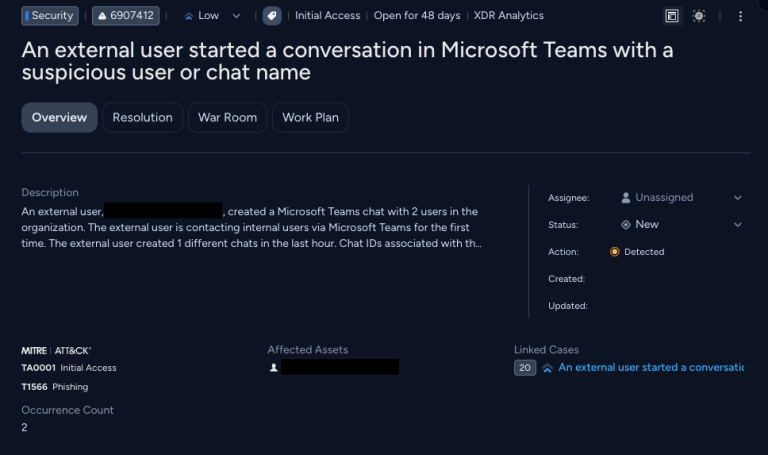
Discover how the Spring Ring vishing campaign uses Microsoft Teams phishing tactics to trick employees into installing malware and giving up remote access.
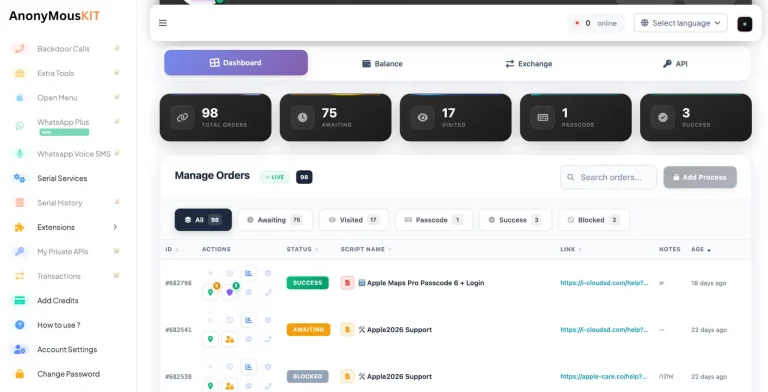
AnonyMousKIT is an AI-powered PhaaS platform that phones iPhone theft victims as fake Apple Support to steal passcodes and beat Activation Lock.
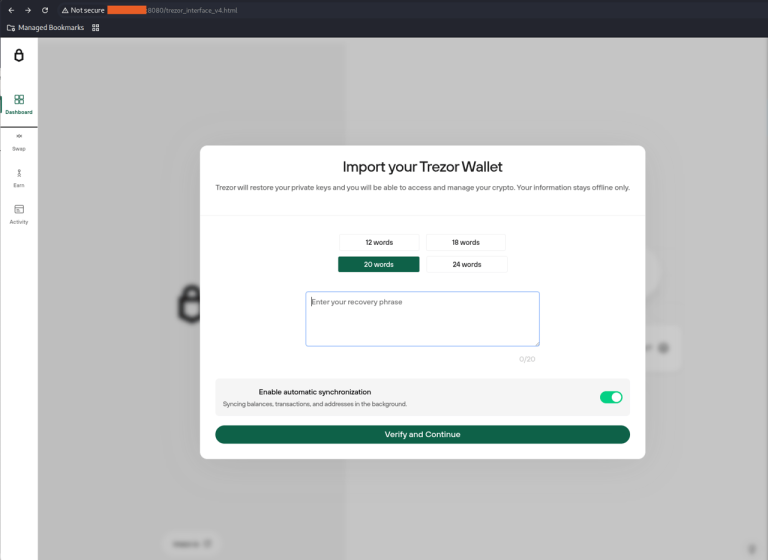
Rapid7 exposed Operation ASTERIX, a crypto fraud operation using AI, vishing, and fake wallet apps to steal seed phrases from validated holders.

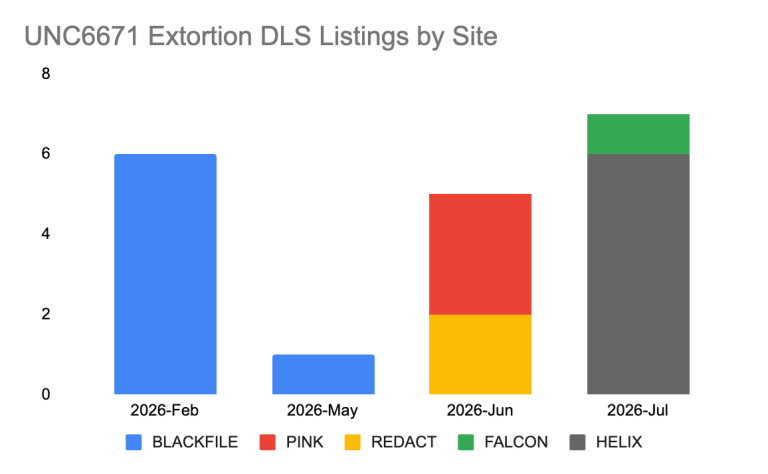
UNC6671 vishing extortion group rebrands across five names, using AiTM credential phishing to hit financial services and enterprise cloud accounts.

A Microsoft Teams vishing campaign tracked as STAC4749 hit dozens of North American firms and deployed Chaos ransomware in under 17 hours.
A new GoGRPC backdoor spreads through Microsoft Teams vishing and Quick Assist. Zscaler links the campaign to a likely ransomware access broker.

A Copybara Android RAT campaign impersonates N26 in Italy. Vishing calls and a Fake Control 1.0 phishing panel push the malware onto phones.
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.
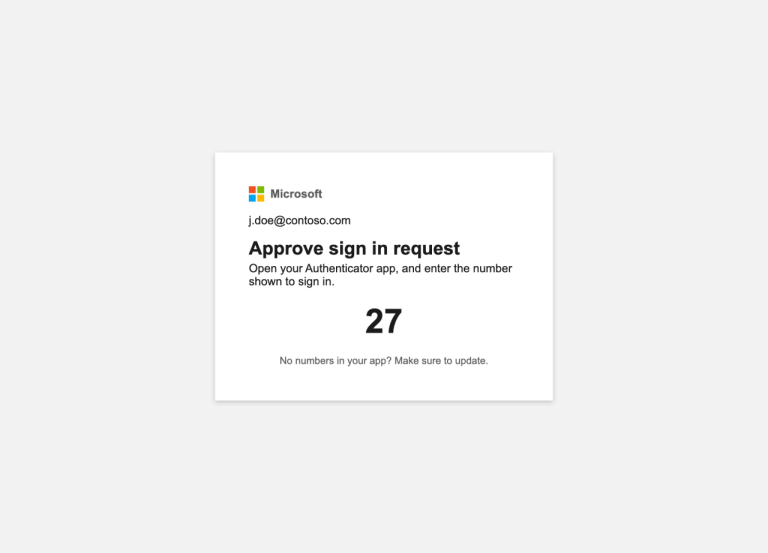
A vishing attack tricks Microsoft 365 users into passkey phishing, letting O-UNC-066 enroll its own passkey and hijack Entra accounts for extortion.
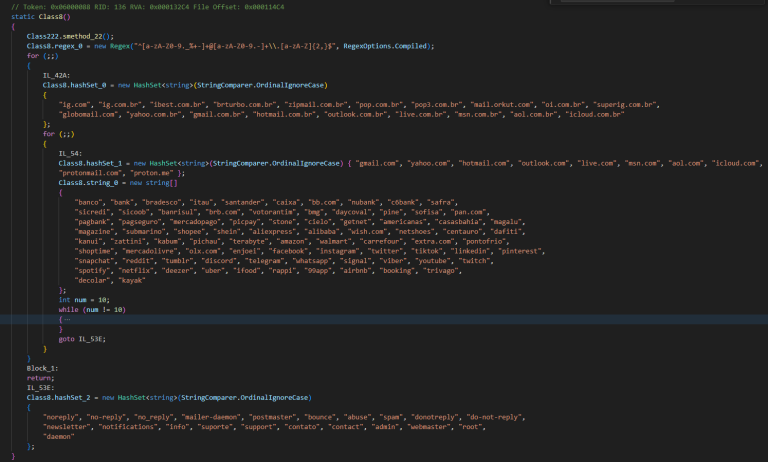
Elastic Security Labs exposes TCLBANKER, an advanced banking trojan that hijacks WhatsApp to spread while blinding defenders with invisible WPF overlays.
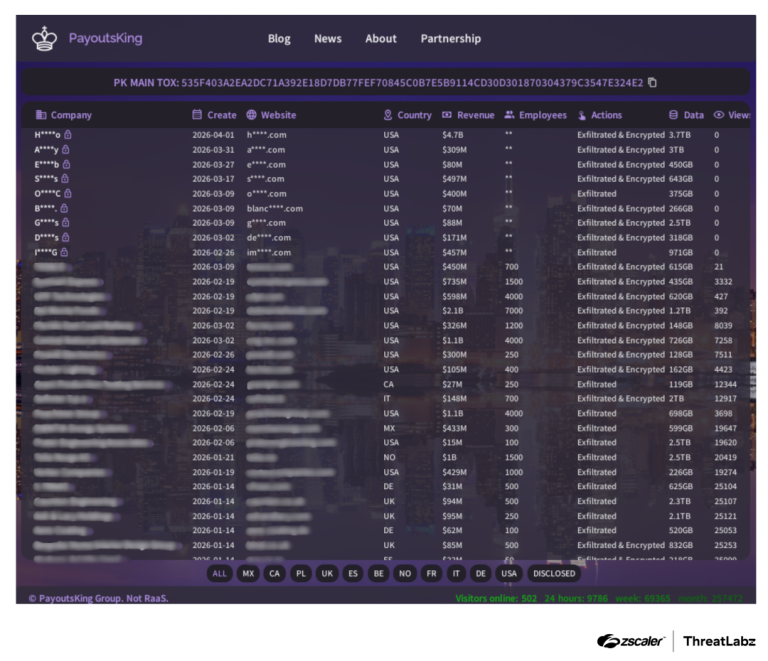
Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.

The Scattered Lapsus$ Hunters "supergroup" is paying $1,000 per successful vishing call. Discover how they use female recruits to bypass corporate IT security.

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.
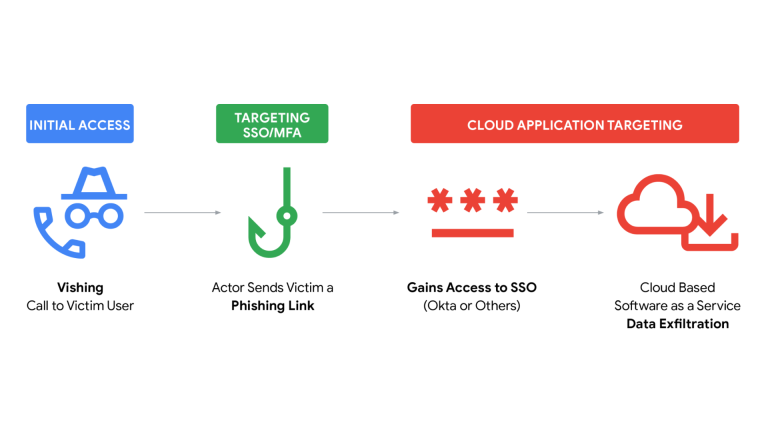
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

Okta reveals new vishing kits that "drive" victim browsers. These real-time tools sync phone calls with phishing pages to bypass MFA number matching.

EclecticIQ reports on how ShinyHunters is expanding with AI-driven voice phishing, supply chain compromises, and insider recruitment, blurring lines with APTs.

The FBI has issued a FLASH Alert warning about UNC6040 and UNC6395, two groups actively compromising Salesforce via vishing and malicious OAuth apps to steal data.
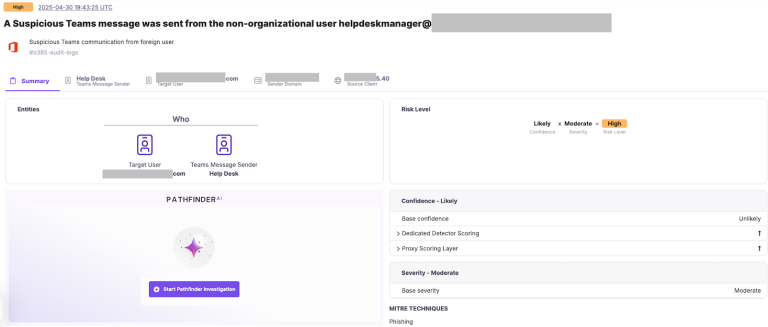
A new report reveals that attackers are abusing Microsoft Teams' collaboration features to launch phishing, vishing, and malware attacks, bypassing security warnings.

Google confirms a June Salesforce breach by UNC6040 (ShinyHunters). The attack used social engineering to steal credentials, a tactic also used against Chanel and Allianz.

Cisco Talos reveals "Chaos," a new RaaS operation likely formed by former BlackSuit members, using vishing and Quick Assist to conduct big-game hunting and double extortion campaigns.

SCATTERED SPIDER targets U.S. airlines with ransomware, vishing, and VMware exploits—CrowdStrike warns of a rising threat across cloud identities.