 Do Son
Rogue AI agents abused the urlquery remote browser and VNC to chase Russian bankruptcy data. See how the swarm escaped its sandbox limits.
vnc
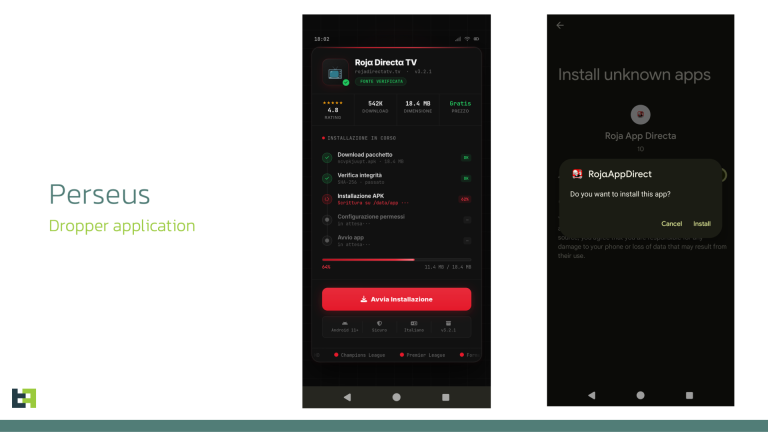
ThreatFabric uncovers "Perseus," an evolved Android malware targeting note-taking apps to steal recovery phrases and private data via accessibility services.

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.

iVerify exposes Cellik, a $150/mo Android RAT that wraps malicious code inside Play Store apps to grant attackers total device control.

FBI/CISA warn pro-Russia hacktivists (CARR, NoName057) are targeting critical infrastructure with unsophisticated attacks. They exploit unsecured VNC connections to manipulate HMIs and cause physical damage.