 Do Son
Copeland XWEB EVO flaw CVE-2026-124010 gives unauthenticated root and is exploited in the wild, alongside CVE-2026-124014. PoC details are public.
VulnCheck
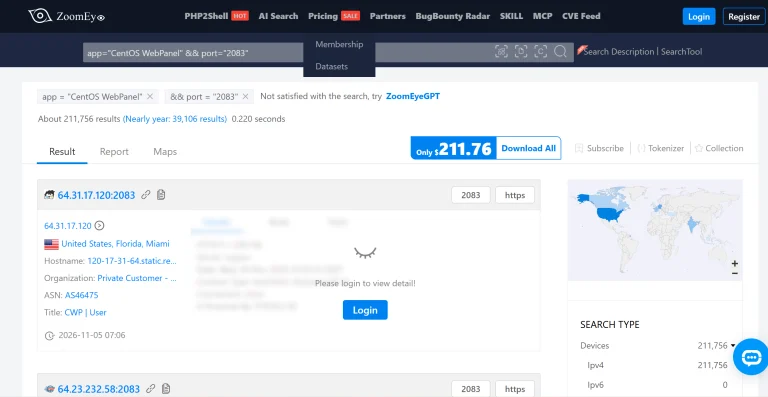
Update Control Web Panel to version 1.29 now to patch CVE-2026-73695, CVE-2026-73696, and eight other flaws allowing unauthenticated root RCE.
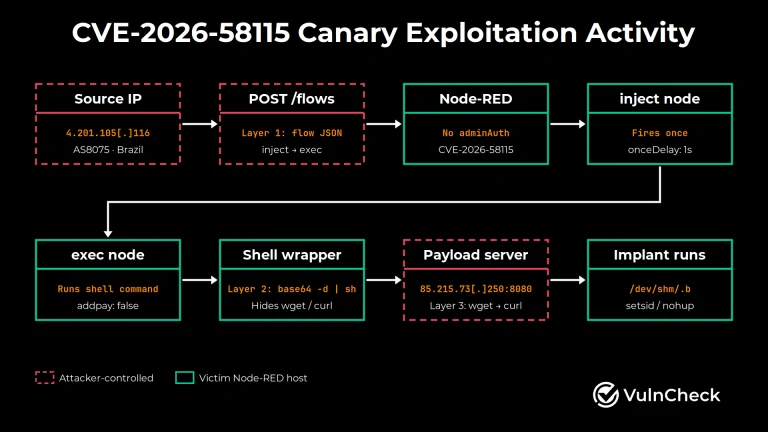
A critical 10.0 CVSS Node-RED RCE vulnerability (CVE-2026-58115) is exploited in the wild to deploy Linux bot malware. Secure your exposed instances now.
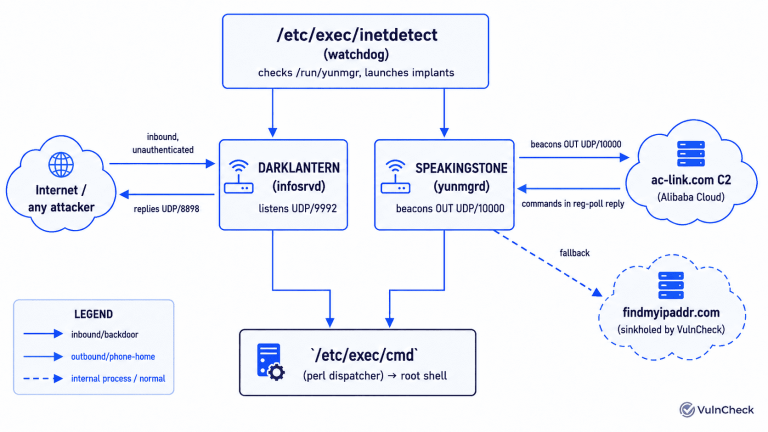
VulnCheck found a ZBT router backdoor in firmware, tracked as CVE-2026-74232 and CVE-2026-74233, granting unauthenticated root over the internet.
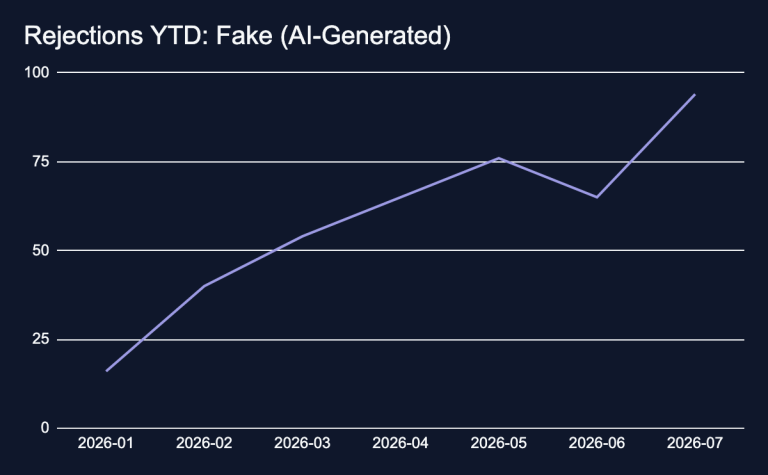
Fake AI PoCs and malicious code are taking over GitHub exploit repositories. Discover how researchers filter through the noise to find real vulnerabilities.

Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.
Researchers publicly disclosed a libssh2 vulnerability, CVE-2026-58050, with PoC code. A malicious SSH server can corrupt a client's heap. Patch now.

Critical 18-year-old "NGINX Rift" flaw CVE-2026-42945 is under active exploitation. Learn how to patch your proxies and block the unauthenticated heap overflow.

VulnCheck reveals CVE-2025-11953 (Metro4Shell) was exploited in the wild since Dec 2025. Attackers target Windows & Linux dev servers. Patch now.
CISA adds XWiki (CVE-2025-24893) and VMware (CVE-2025-41244) to its KEV Catalog after confirming active exploitation in the wild.