
 Do Son
A critical vulnerability (CVE-2025-1976) in Brocade Fabric OS allows a local admin user to execute arbitrary code with root privileges. Update immediately!
Vulnerability

RustoBot, a sophisticated botnet written in Rust, is exploiting vulnerabilities in TOTOLINK & DrayTek routers to launch DDoS attacks. Learn how this malware operates and how to protect your network.
CVE-2025-3616 in Greenshift plugin allows subscriber-level users to upload malicious files, enabling remote code execution on 50,000+ WordPress sites.

CVE-2025-32434: Critical RCE vulnerability in PyTorch’s torch.load(weights_only=True) affects ≤2.5.1. Update to v2.6.0 to patch this major flaw

Yokogawa recorders have a critical vulnerability (CVE-2025-1863) due to insecure default settings. Attackers can manipulate data. Update security now!

Critical vulnerability (CVE-2025-42599) in Active! mail allows remote code execution. Update to the latest version immediately to protect your systems.

Critical RCE vulnerability (CVE-2025-24797) in Meshtastic allows remote takeover. Update to 2.6.2 immediately to stay safe.

GCVE introduces a decentralized system for vulnerability IDs, empowering organizations with autonomy and speed. Complements CVE for smoother vulnerability management.

CISA warns of actively exploited vulnerabilities in Apple and Microsoft products. Urgent patching is required to mitigate risks from these attacks.

A vulnerability (CVE-2024-53141) in the Linux kernel's ipset component allows for privilege escalation and kernel-level code execution.

Siemens patches 66 SQL injection vulnerabilities in TeleControl Server Basic, urging users to upgrade and restrict access.

Microsoft will disable ActiveX controls in Office 365 & 2024 to enhance security. Users can re-enable manually, but it poses security risks.

CISA issues urgent alert on actively exploited SonicWall SMA100 vulnerability (CVE-2021-20035). Federal agencies must mitigate by May 7, 2025

The CVE Foundation launches to ensure the future of the CVE Program after U.S. government funding ends for MITRE's operation.
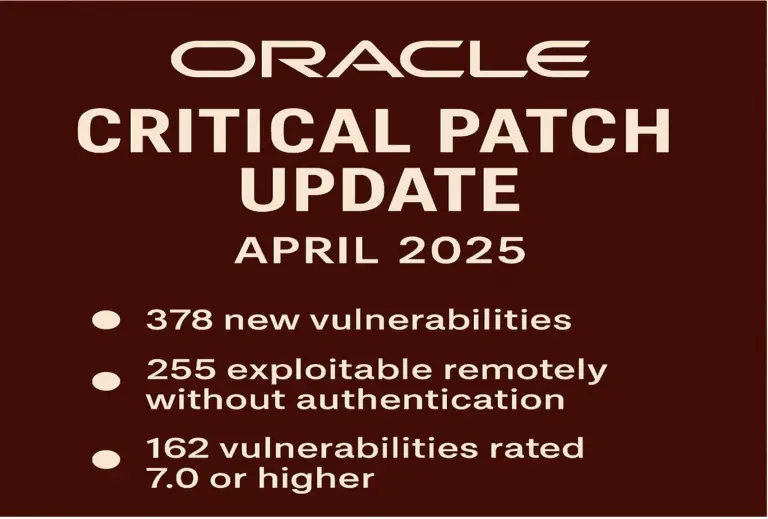
Oracle's April 2025 CPU delivers 378 security patches across its product suite. Learn about critical vulnerabilities and the urgent call to update.

Google Chrome 135 fixes critical CVE-2025-3619 and high CVE-2025-3620 flaws. Users urged to update now to avoid potential code execution threats.

Discover how Windows 11 vulnerabilities CVE-2025-24076 and CVE-2025-24994 allow unprivileged users to gain system privileges via DLL hijacking.

iFAX Solutions discloses a critical remote code execution vulnerability (CVE-2025-1782) affecting HylaFAX and AvantFAX due to improper sanitization

Google ends security updates for Android 12. Users face increased vulnerability. OEMs unlikely to provide patches. LineageOS offers an alternative.

PyPI resolved a security issue on April 14, 2025, where users retained team privileges after organization removal. The swift 2-hour fix prevented potential escalation.

CrushFTP vulnerabilities CVE-2025-32102 & CVE-2025-32103 enable SSRF and directory traversal. Update now to secure your file transfer server
Apache Roller has a security vulnerability (CVE-2025-24859) where sessions aren't invalidated after password changes, risking unauthorized access