
 Do Son
Learn about CVE-2024-43461, a newly discovered zero-day vulnerability impacting the Windows MSHTML Platform and posing a significant security risk.
Vulnerability

Discover the latest remote code execution attacks targeting WhatsUp Gold. Learn how to protect your network monitoring software from CVE-2024-6670 and CVE-2024-6671 vulnerabilities.

Learn about the cyber espionage campaign 'Operation DevilTiger' by APT-Q-12. Explore their use of zero-day vulnerabilities and advanced tactics.

Discover the details of the newly discovered security vulnerability CVE-2024-7646 in the ingress-nginx controller for Kubernetes.

Urgent security advisory: Apache OFBiz vulnerability (CVE-2024-38856) exposes ERP systems to unauthorized code execution.

Protect your systems from the ImageMagick vulnerability. Learn about the security flaw that could lead to data breaches and system compromise.

The lighttpd project has now obtained CVE-2018-25103 to formally identify the vulnerability and alert supply-chain partners

CVE-2024-38472 (Important): Server-Side Request Forgery (SSRF) vulnerability on Windows systems, potentially leaking sensitive NTML hashes

A vulnerability has been discovered in TP-Link VIGI NVR4032H network video recorder, a device widely used in surveillance systems

A high-severity vulnerability (CVE-2024-5585) has been identified in multiple versions of PHP, the widely used server-side scripting language
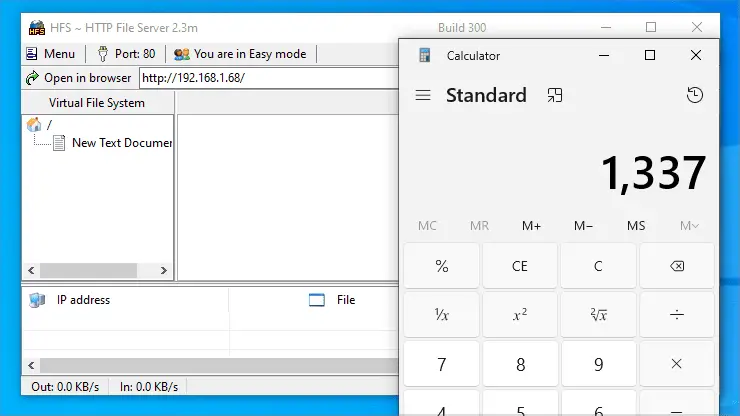
A critical vulnerability, identified as CVE-2024-23692, has been discovered in Rejetto HTTP File Server (HFS) versions 2.x

The vulnerability, tracked as CVE-2024-4577, could potentially allow unauthenticated attackers to take full control of affected PHP servers

Tenable Research has uncovered a significant vulnerability within Microsoft Azure's Service Tags functionality

CVE-2024-21512 stems from a Prototype Pollution vulnerability that could be exploited for remote code execution.

Designated as CVE-2024-35204, this vulnerability has been assigned a CVSS score of 8.4, indicating its high severity

A critical vulnerability (CVE-2024-3273) discovered in multiple end-of-life D-Link network-attached storage (NAS) devices

This RCE vulnerability was facilitated through the use of Cog, Replicate’s proprietary format for containerizing AI models.
The flaw, designated CVE-2024-4671, is a "use after free" bug located within the browser's "Visuals" component.
CVE-2024-4439 (CVSS score of 7.2) pertains to a stored Cross-Site Scripting (XSS) flaw in the WordPress Core.

CVE-2024-32971 vulnerability with a CVSS score of 9.1, has been discovered in versions 1.44.0 and 1.45.0 of the Apollo Router

The vulnerability, now patched, resided in Telegram's "Mini App" system. These mini web applications, designed to run within Telegram

Apache HugeGraph has recently addressed several critical security vulnerabilities that posed significant risks to its users