
 Do Son
CVE-2022-46718, a logic issue affecting Apple's iOS, enables unauthorized applications to access users' sensitive location information
Vulnerability
two critical security vulnerabilities have been discovered in PaperCut MF and PaperCut NG, which are currently being exploited in the wild
It's important to note that Google has acknowledged the existence of an exploit for CVE-2023-2136 in the wild.
CVE-2023-30547 flaw could enable attackers to break out of security boundaries and execute arbitrary shellcodes.
CVE-2023-2002 has been identified within the Linux kernel, posing a significant risk to systems that utilize Bluetooth communication
The CVE-2023-20862 vulnerability arises when the logout support does not properly clean the security context if using serialized sessions.

CVE-2023-2033, is a type confusion issue in the V8 JavaScript engine, and Google has already released an emergency update to protect users

The security researcher @LinusHenze unveiled a PoC exploit for the CVE-2023-28206 flaw, revealing an out-of-bounds memory move

A memory leak vulnerability (CVE-2023-26083) affects Arm Mali GPU Kernel Driver across multiple versions, exposing sensitive kernel metadata.
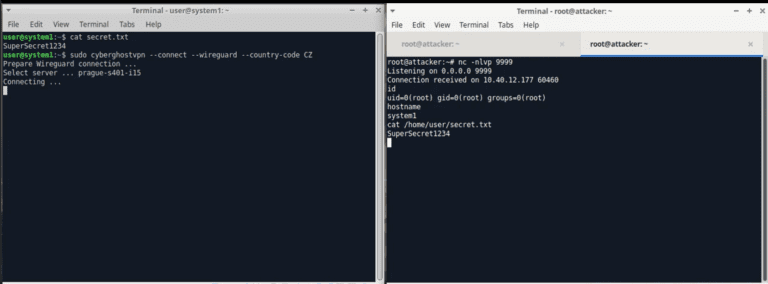
two vulnerabilities have been discovered, which, when combined, can lead to a man-in-the-middle (MITM) attack and remote code execution (RCE)

The CVE-2023-20117 & CVE-2023-20128 vulnerabilities found in the web-based management interface of Cisco RV320 and RV325 VPN Routers
CVE-2022-4939, with a CVSS score of 9.8, is a severe security flaw affecting WCFM Membership versions up to and including 2.10.0

CVE-2023-28326 is considered critical and can potentially cause serious harm to users and organizations that use this software.
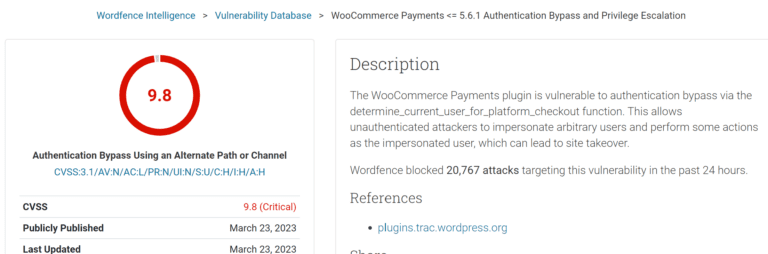
a critical vulnerability with a CVSS score of 9.8, resides in the WooCommerce Payments plugin versions 4.8.0 through 5.6.1
4 of the critical bugs patched this month reside in System (CVE-2023-20951 & CVE-2023-20954) and Qualcomm's closed-source components
CVE-2022-41223 and CVE-2022-40765 can be exploited by a remote authenticated attacker to execute arbitrary code on the system.

An attacker could exploit the CVE-2022-27677 vulnerability to execute arbitrary code with higher privileges on the system.

CVE-2023-23529, the issue has been described by the tech giant as a type confusion issue in the WebKit browser engine
Discovered by the security researcher, Erol Guven, CVE-2023-25727 is an XSS attack and affects phpMyAdmin versions prior to 4.9.11 and 5.2.1

The critical vulnerability tracked as CVE-2017-11357 is rated 9.8 out of 10 for severity on the CVSS scoring system, and was patched by Progress

The PoC exploit targets CVE-2022-42864, a vulnerability that could allow a remote attacker to execute arbitrary code on the system
CVE-2022-45461 is a high OS command injection vulnerability that affects NetBackup versions 8,9, and 10 and Appliance versions 3,4, and 5