
 Do Son
A critical risk has surfaced within Google Workspace's Domain-Wide Delegation feature, as revealed by Unit 42 researchers at PaloAlto Networks
Vulnerability
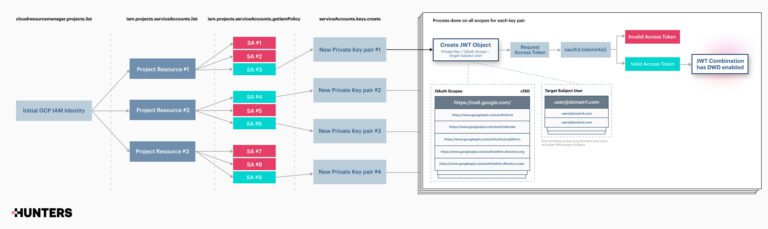
Hunters researchers dubbed the vulnerability "DeleFriend". The error enables an attacker to manipulate existing delegations

The second vulnerability, CVE-2023-47039, presents a more targeted threat, specifically for Perl on Windows systems.

The immediate, albeit inconvenient, recommendation is to consider alternative devices that do not harbor the CVE-2023-6304 vulnerability

Researchers highlight the increasing reliance on IoT devices, such as cow tracking collars, in the agricultural sector to improve efficiency

SonarSource have disclosed technical details for CVE-2023-36742 and a public proof-of-concept (PoC) exploit
Security researchers have deconstructed the patch released by Microsoft and crafted a PoC exploit for the CVE-2023-36025 vulnerability.

page displayed a weather forecast, demonstrating how a “prompt injection” attack could be executed from a page with legitimate information

Given that these energy companies are integral to Denmark's critical infrastructure, the potential impact of such a cyberattack is immense

A vulnerability in Microsoft Access that allows cybercriminals to exploit the "linking to remote SQL Server tables" feature

The zero-day flaw, CVE-2023-47246, resides in SysAid on-premises software, allowing hackers to execute arbitrary code on vulnerable systems

In summation, the HackerOne report underscores the profound influence of ethical hackers on the cybersecurity domain

To gauge the potential impact of CVE-2023-46604, Qi Anxin CERT replicated the Apache ActiveMQ remote code execution vulnerability

This vulnerability stems from a discrepancy in chunked decoder lenience, making Squid susceptible to Request/Response smuggling attacks

Interestingly, AMD's Zen 1 architecture was not impervious, being plagued by a vulnerability christened "Division by zero."

Netgear has recently addressed a high-severity vulnerability that had been lurking in its RAX30 WiFi router model

The vulnerability tracked as CVE-2023-2868 and boasting a worrisome CVSS score of 9.4, allows attackers to remotely execute system commands
The CVE-2023-32960 vulnerability could lead to a more insidious Stored Site-Wide Cross-Site Scripting (XSS) attack on the wp-admin area
CVE-2023-32956 is ranked as critical with a CVSS3 Base Score of 9.8. It is an OS Command Injection flaw found in the CGI component of SRM
A Proof-of-Concept (PoC) for CVE-2023-32233 allows unprivileged local users to start a root shell on impacted systems.

With a high CVSS score of 9.6, the CVE-2023-2478 vulnerability poses a serious risk to the integrity and security of GitLab projects.

Researcher Xkaneiki developed a PoC exploit for this vulnerability, demonstrating the potential risks posed by CVE-2023-0386