 Do Son
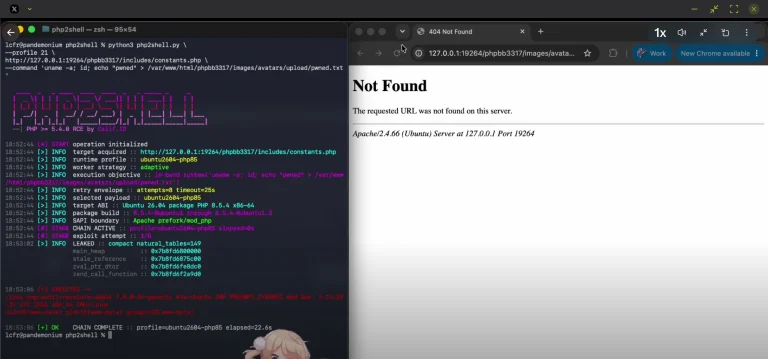
Cloudflare reports early attacks on two critical PHP flaws ahead of the PHP security release fixing remote code execution bugs CVE-2026-109618.
waf
A SiteGuard Server Edition vulnerability, CVE-2026-106931, is exploited in the wild and grants root or SYSTEM access. Update to Ver8.00 Update 5 now.
Discover the latest ModSecurity security vulnerabilities, including WAF evasion and pointer dereferences. Patch these OWASP WAF engine flaws today.
Two ModSecurity vulnerabilities let attackers slip past WAF rules via a multipart parser bug (CVE-2026-52747). Update to ModSecurity v3.0.16 now.
libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.

CISA added a FortiWeb RCE flaw (CVE-2025-58034) to its KEV Catalog due to active exploitation. The bug allows authenticated attackers to execute arbitrary code on the WAF via crafted requests. Update now.

Cybersecurity firms warn of a Critical, actively exploited FortiWeb flaw that allows unauthenticated attackers to create a new administrator account on the FortiWeb Manager panel. Update to v8.0.2 immediately.

Fortinet released a critical patch for FortiWeb (CVE-2025-25257). This unauthenticated SQL injection flaw allows remote code execution. PoC Releases!

Fortinet released a critical patch for FortiWeb (CVE-2025-25257, CVSS 9.6). This unauthenticated SQL injection flaw allows remote code execution; update immediately!

A new DoS vulnerability (CVE-2025-48866) found in ModSecurity WAF can crash your web application. Update to 2.9.10 immediately!
Radware Cloud WAF has vulnerabilities (CVE-2024-56523, CVE-2024-56524) allowing attackers to bypass filtering via crafted HTTP requests and special characters.

SonicWall urges urgent updates to SMA 100 Series devices after critical post-auth vulnerabilities expose systems to file deletion and command injection.