Skip to content
October 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Wayland

Wayland

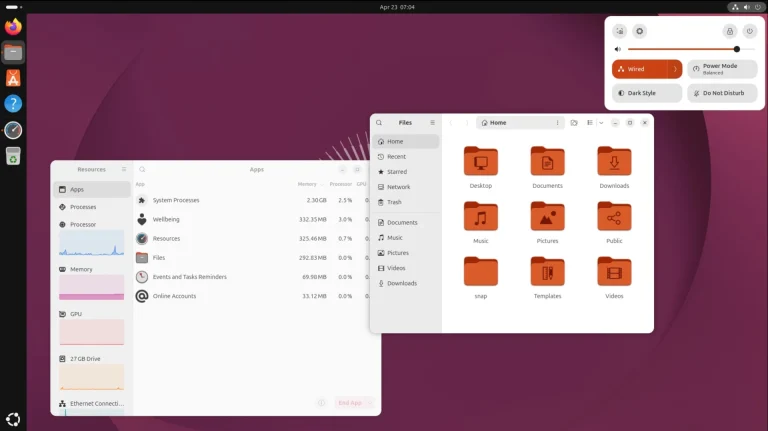
Ubuntu 26.04 Upgrade Now Open to 24.04 LTS Users Ubuntu 26.04 upgrade offered in Update Manager to Ubuntu 24.04 LTS users, showing the Resolute Raccoon desktop
  • Linux

Ubuntu 26.04 Upgrade Now Open to 24.04 LTS Users

Do Son October 5, 2026 0
Canonical Opens the Upgrade Path Canonical has begun offering Ubuntu 24.04 LTS users an automatic upgrade to...
Read More Read more about Ubuntu 26.04 Upgrade Now Open to 24.04 LTS Users
The Zena Evolution: Linux Mint 22.3 Arrives with Cinnamon 6.6 and Kernel 6.14 Linux Mint 22.3 Zena release, Cinnamon 6.6 new features
  • Linux

The Zena Evolution: Linux Mint 22.3 Arrives with Cinnamon 6.6 and Kernel 6.14

Do Son January 19, 2026 0
If you have long contemplated a transition to Linux Mint, the present moment offers a sublime opportunity...
Read More Read more about The Zena Evolution: Linux Mint 22.3 Arrives with Cinnamon 6.6 and Kernel 6.14
Android Now Runs Full Graphical Linux Apps: Google Unleashes Desktop Experience in Terminal VM Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Android

Android Now Runs Full Graphical Linux Apps: Google Unleashes Desktop Experience in Terminal VM

Do Son July 26, 2025 0
In March 2025, Google introduced a terminal application for the Android operating system—not one that merely connects...
Read More Read more about Android Now Runs Full Graphical Linux Apps: Google Unleashes Desktop Experience in Terminal VM

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-58255CVSS 9.6
    Cross-Site Request Forgery (CSRF) vulnerability in yonisink Custom Post Type Images custom-post-types-image allows Code Injection.This issue affects Custom...
    📅 Updated: Oct 11, 2026
  • CVE-2025-59434CVSS 9.6
    Flowise is a drag & drop user interface to build a customized large language model flow. Prior to...
    📅 Updated: Oct 11, 2026
  • CVE-2025-9321CVSS 9.8
    The WPCasa plugin for WordPress is vulnerable to Code Injection in all versions up to, and including, 1.4.1....
    📅 Updated: Oct 11, 2026
  • CVE-2025-10147CVSS 9.8
    The Podlove Podcast Publisher plugin for WordPress is vulnerable to arbitrary file uploads due to missing file type...
    📅 Updated: Oct 11, 2026
  • CVE-2025-10412CVSS 9.8
    The Product Options and Price Calculation Formulas for WooCommerce – Uni CPO (Premium) plugin for WordPress is vulnerable...
    📅 Updated: Oct 11, 2026
  • CVE-2025-59545CVSS 9.0
    DNN (formerly DotNetNuke) is an open-source web content management platform (CMS) in the Microsoft ecosystem. Prior to version...
    📅 Updated: Oct 11, 2026
  • CVE-2025-59834CVSS 9.8
    ADB MCP Server is a MCP (Model Context Protocol) server for interacting with Android devices through ADB. In...
    📅 Updated: Oct 11, 2026
  • CVE-2025-10542CVSS 9.8
    iMonitor EAM 9.6394 ships with default administrative credentials that are also displayed within the management client’s connection dialog....
    📅 Updated: Oct 11, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.