
 Do Son
Apache patched a Critical DoS flaw (CVE-2025-64775) in Struts. The bug causes a temporary file leak during multipart requests, allowing unauthenticated attackers to fill the disk and crash the server. Update now.
web framework

Django released urgent patches (v5.2.8+) for a Critical SQL Injection flaw (CVE-2025-64459) affecting QuerySet methods via the _connector keyword, risking remote database compromise.

The Django team released urgent updates (v5.2.7, 5.1.13, 4.2.25) to fix a High-severity SQL Injection flaw (CVE-2025-59681) affecting QuerySet methods in MySQL/MariaDB.
A new report reveals a high-severity SQL injection flaw (CVE-2025-57833) in Django's FilteredRelation. A PoC is public with technical details. Patching is urgent.

A new report reveals a high-severity SQL injection flaw (CVE-2025-57833) in Django's FilteredRelation. The bug allows attackers to manipulate queries.

A critical command injection flaw (CVE-2025-54418, CVSS 9.8) in CodeIgniter's ImageMagick handler allows remote code execution via malicious filenames or text.

A critical SSTI flaw (CVE-2025-53833, CVSS 10.0) in LaRecipe allows unauthenticated RCE on affected servers via template injection. Update to v2.8.1 immediately!
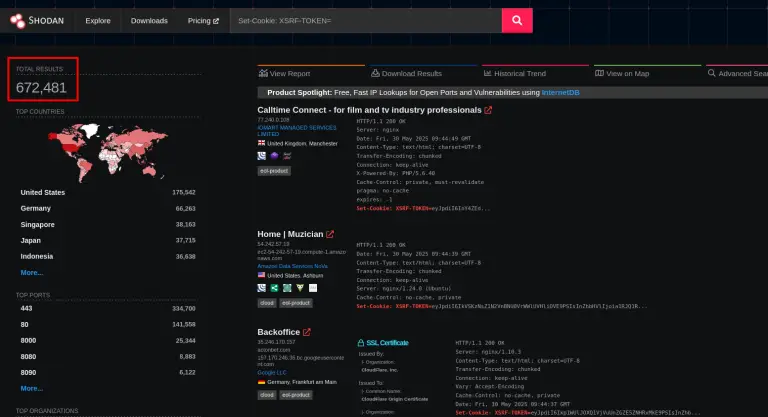
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.

Tornado is vulnerable to DoS attacks due to its default parser. Details on CVE-2025-47287 and how to mitigate the high-severity threat.

CVE-2024-58136: A security vulnerability in the Yii 2 PHP framework is being actively exploited. Learn about the risk and necessary updates.

A high-severity vulnerability (CVE-2024-38513) has been discovered in Fiber, a widely-used web framework for the Go programming language