 Do Son
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
WebDAV
Apache HTTP Server 2.4.69 fixes 20 flaws, including CVE-2026-63292, a mod_vhost_alias stack overflow that may enable code execution.

A ClearFake WebDAV infection chain deployed Amatera malware. See how the ClearFake WebDAV infection chain drops crypto stealers on targets.
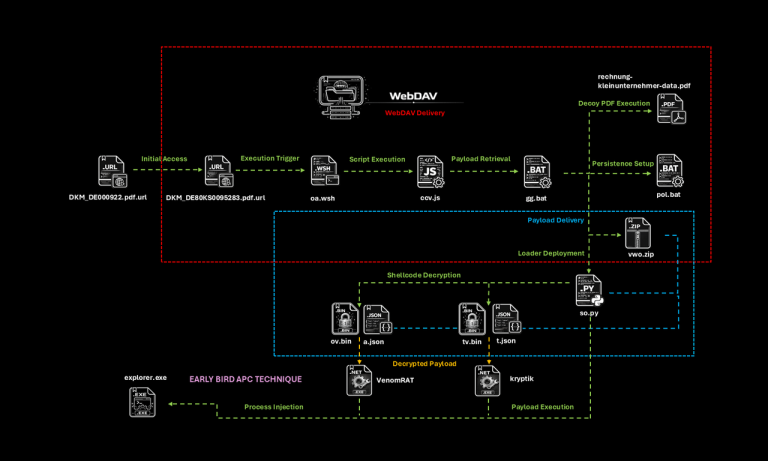
G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!

Cofense uncovers a stealthy campaign abusing legacy WebDAV in Windows File Explorer to bypass browsers and EDR, delivering XWorm and Async RAT via UNC paths.

New AsyncRAT campaign abuses free Cloudflare tunnels for stealthy malware delivery. Learn how phishing emails lead to WebDAV attacks & Python injection.

ASUS fixes 8 severe router flaws, including a critical AiCloud authentication bypass (CVSS 9.4). Users must update firmware immediately to patch vulnerabilities.

Sophos uncovers a new infection chain for GOLD BLADE's RedLoader malware, combining LNK files, WebDAV, and DLL sideloading to bypass defenses and deploy payloads stealthily.

Stealth Falcon APT is exploiting a Windows WebDAV zero-day (CVE-2025-33053) in a sophisticated cyberespionage campaign targeting defense entities in the Middle East & Africa.

Microsoft's June 2025 Patch Tuesday fixes 69 vulnerabilities, including two exploited zero-days in WebDAV and Windows SMB Client. Patch immediately!

Darktrace uncovers a SocGholish campaign using obfuscated loaders and legacy Windows exploits to harvest NTLM hashes and deliver ransomware payloads.

Stay informed about the Strela Stealer phishing campaign targeting Europe. Learn how this sophisticated malware steals sensitive data from compromised systems.