 Do Son
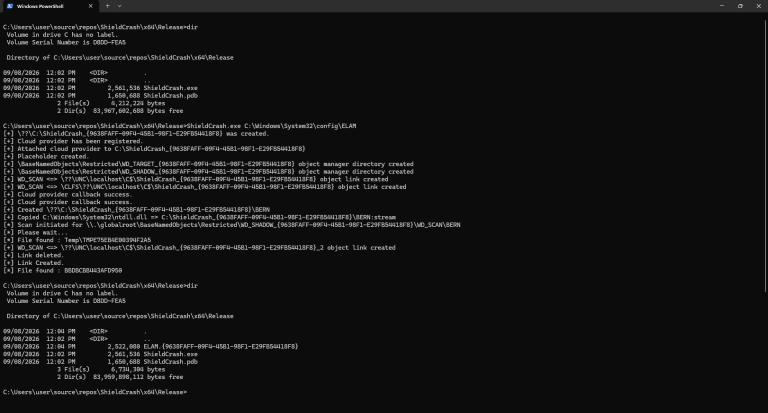
A Windows Defender 0day, CVE-2026-69414, has public PoC exploit code. ShieldCrash reads files as SYSTEM on all supported Windows versions.
Windows Defender
Silver Fox fake software installers impersonate Razer and Edge to disable Windows Defender and deploy malware. See how the campaign works.
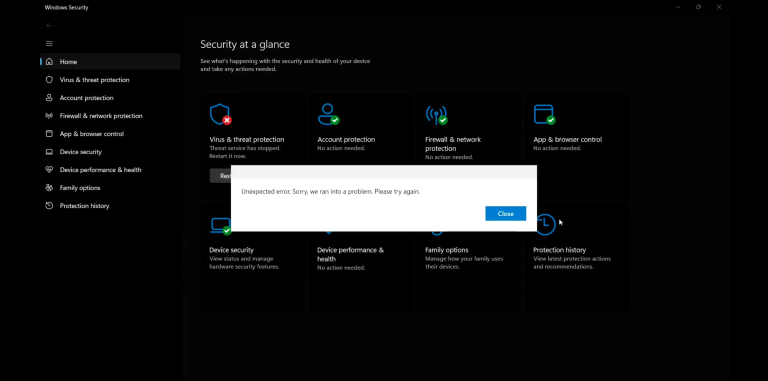
Check Point details BTR.sys driver abuse: a signed Defender component turned into a kernel EDR/AV bypass with no exploit needed.
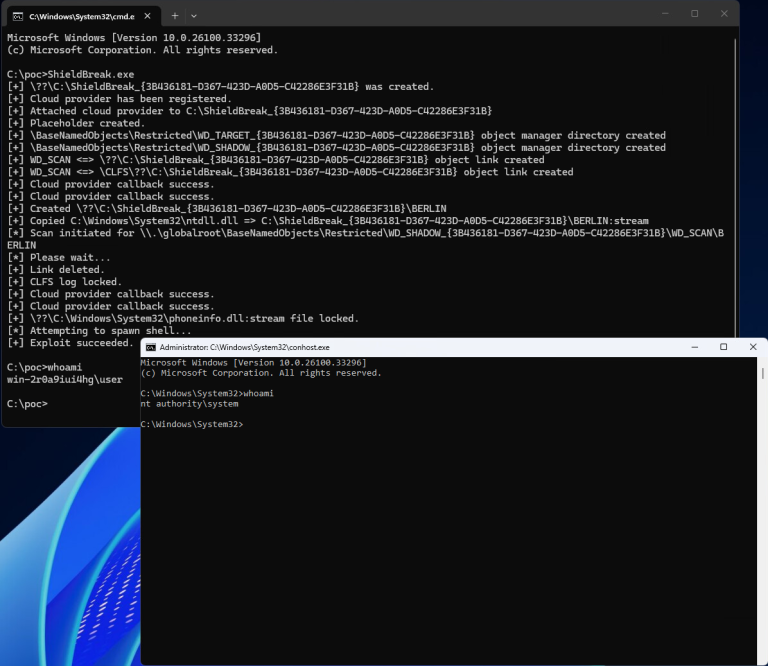
A public PoC named ShieldBreak bypasses Microsoft's CVE-2026-50656 patch, enabling Windows Defender privilege escalation to SYSTEM.
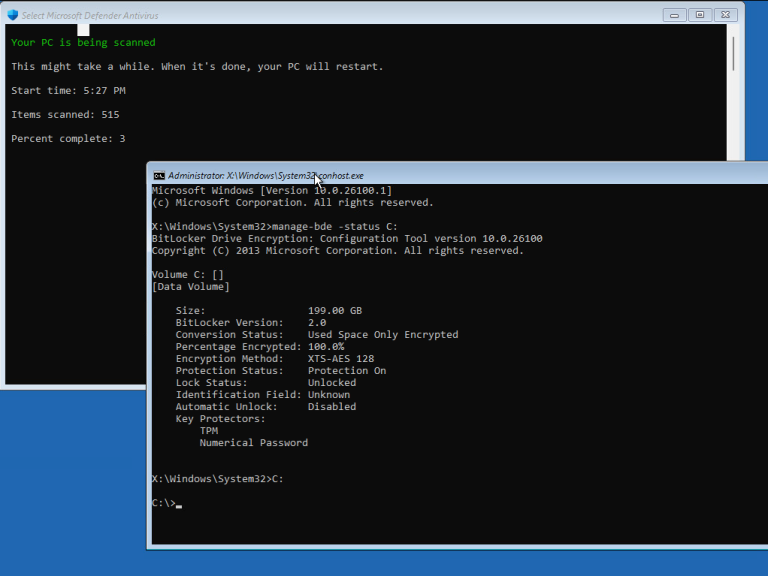
A new GreatXML BitLocker bypass PoC exploit is publicly disclosed. Learn how this Windows Defender vulnerability grants unrestricted volume access.

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!
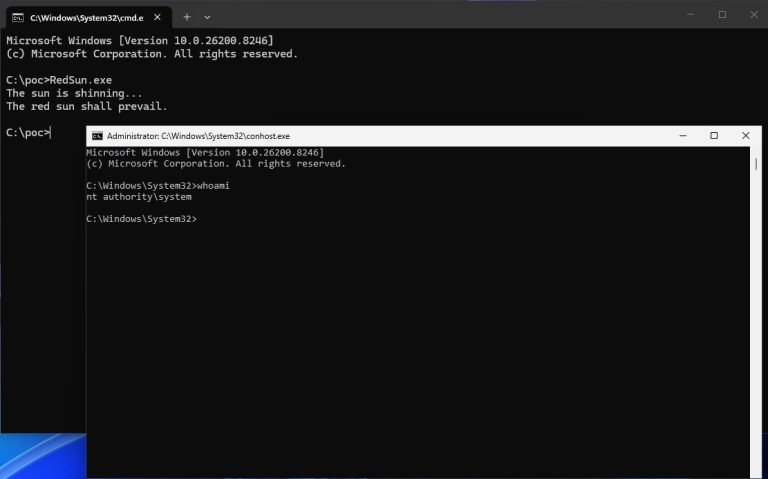
Windows Defender "RedSun" zero-day revealed! This unpatched EoP flaw turns antivirus into a delivery tool for malicious payloads. PoC is public—patch now!
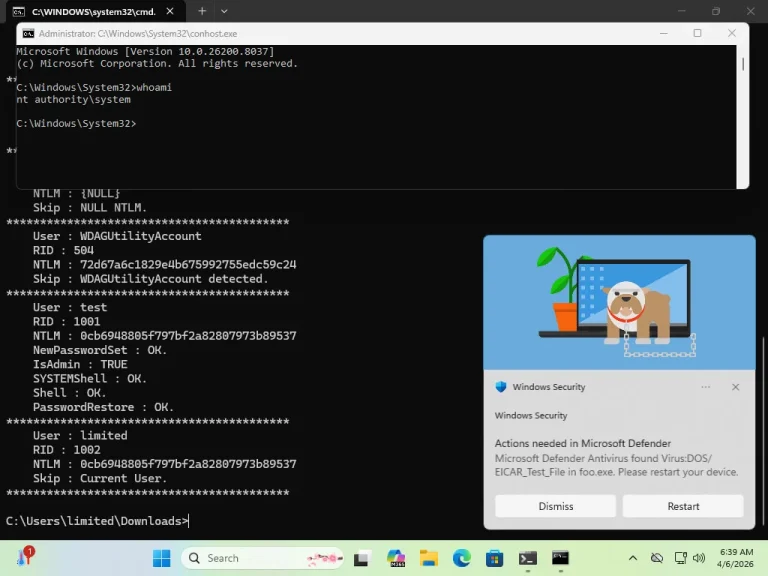
BlueHammer is a functional 0-day exploit targeting Windows Defender’s update engine to achieve SYSTEM privileges. Here is how the unpatched LPE works.

ASEC warns of Larva-25012 using fake Notepad++ installers for Proxyjacking. The malware disables Defender and sells your bandwidth. Check your tasks.

Attackers abuse GitHub, Dropbox, and the "Defendnot" research tool to disable Windows Defender and deploy Amnesia RAT & ransomware in Russia.

A new botnet, NightshadeC2, is using a technique called "UAC Prompt Bombing" to bypass sandboxes and Windows Defender by relentlessly looping UAC prompts.

Defendnot disables Windows Defender using a novel method, directly interacting with the WSC. Learn how this new security tool works.

Explore EncryptHub's attacks and discover how EncryptRAT utilizes trojanized applications to compromise systems effectively.

Discover the advanced techniques and intricate execution process of the highly sophisticated Raspberry Robin downloader.

Protect your data on public Wi-Fi networks with Defender VPN. Learn how Microsoft's updated Defender features keep you safe while connected on the go.

Beware of the evolving threat of AsyncRAT malware disguised as cracked software. Learn how cybercriminals are using this sophisticated remote access trojan to infiltrate systems.
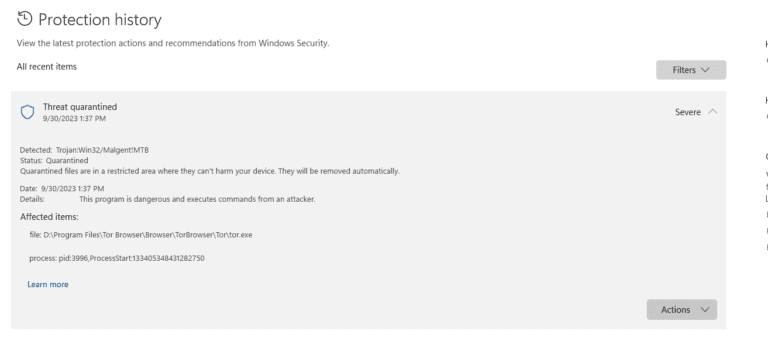
Microsoft Defender showcased its susceptibility to false positives by recognizing the Tor browser as a virus and halting its operations
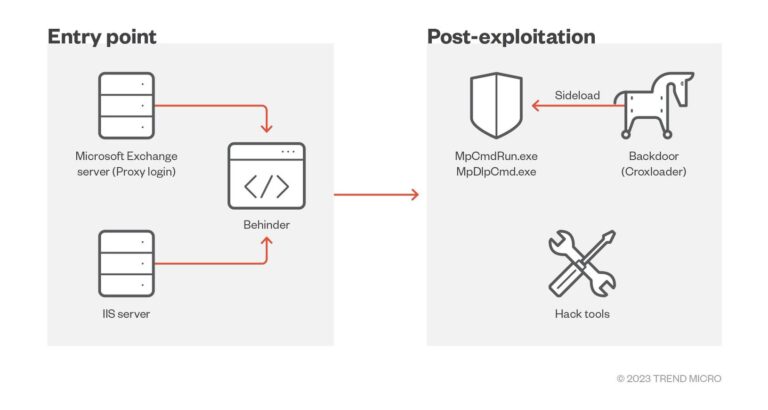
Researchers from Trend Micro have uncovered a new campaign by Earth Longzhi, a subgroup of APT41, which targets organizations