 Do Son
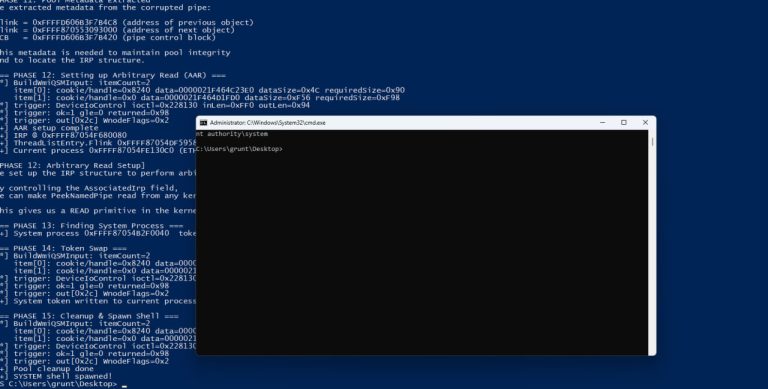
A public PoC for CVE-2026-42980 details a Windows privilege escalation flaw in the kernel WMI code. It grants SYSTEM on unpatched builds.
Windows Kernel
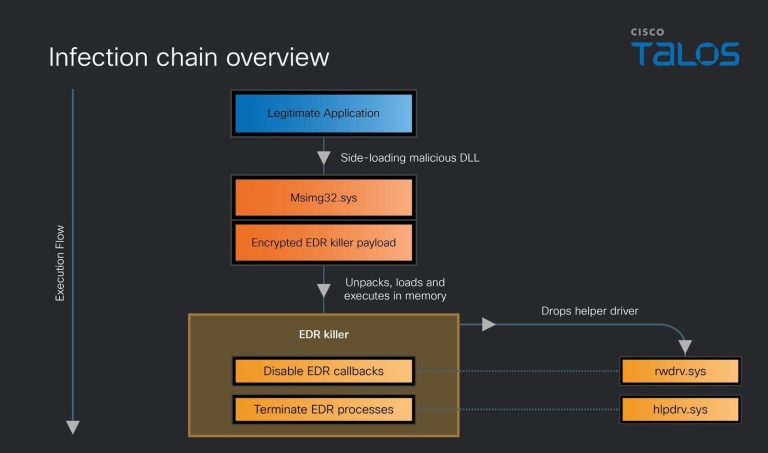
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.
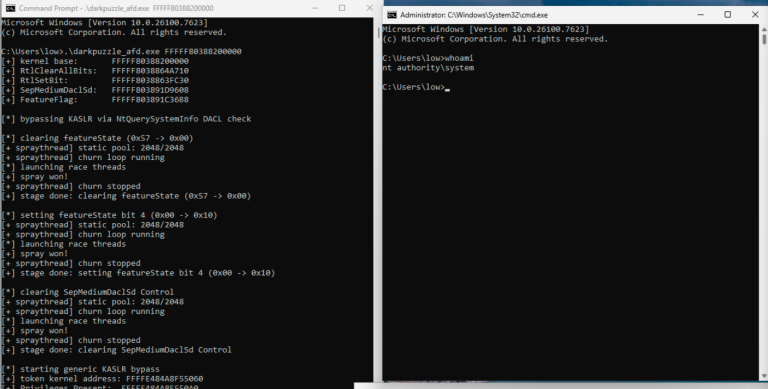
Windows kernel vulnerability CVE-2026-21241 (afd.sys) exposed! A new PoC exploit shows how local attackers can win a race condition to gain SYSTEM privileges.

Microsoft's CoreAI team aims to eliminate all C/C++ code by 2030. Using AI agents, they plan to rewrite 1 million lines of code per engineer, every month.

Microsoft's November Patch Tuesday fixes 68 vulnerabilities, including CVE-2025-62215, an actively exploited Windows Kernel zero-day allowing local attackers to gain SYSTEM privileges via a race condition.

Kaspersky exposes a new AV killer leveraging the legitimate ThrottleStop.sys driver to disable antivirus software and deploy MedusaLocker ransomware in a BYOVD attack.

Two Windows Kernel vulnerabilities allow SYSTEM-level privilege escalation. PoC exploit code is publicly available.

Learn how Microsoft tackled CVE-2025-24983 flaw after two years of exploitation in Windows NT kernel. Essential cybersecurity info.

Learn about the latest threat to Windows systems: a sophisticated UEFI bootkit that compromises the kernel during boot process.

Based on Angelboy's analysis, security researcher Varwara has released a PoC exploit code to demonstrate the CVE-2024-35250's impact
Stay informed about the latest security update from Microsoft: CVE-2024-37985, a zero-day vulnerability in the Windows kernel.

PixiePoint Security published a PoC exploit for a critical 0-day vulnerability in the Windows Kernel, identified as CVE-2024-38106

Cybersecurity researcher shared technical details and PoC exploit for a high-severity EoP flaw (CVE-2024-26218) bug affecting Windows Kernel.