 Do Son
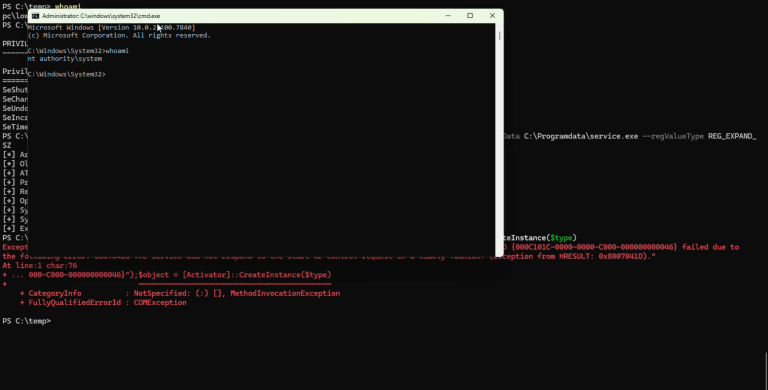
Exploit code and details for RegPwn (CVE-2026-24291) are publicly disclosed. The Windows local privilege escalation flaw grants attackers SYSTEM access.
Windows Security
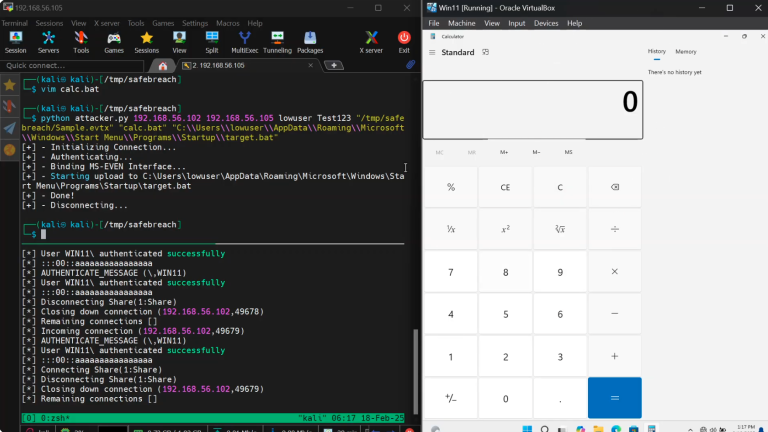
SafeBreach Labs releases PoC exploit code for EventLogin (CVE-2025-29969), a TOCTOU flaw in Windows MS-EVEN RPC allowing remote file writes. Patch now.
Zoom patches a critical 9.6 CVSS flaw (CVE-2026-30903) allowing unauthenticated remote privilege escalation on Windows. Update your clients immediately.

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.
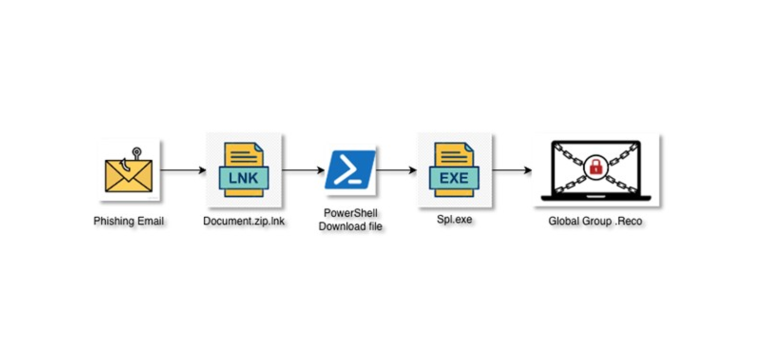
Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.
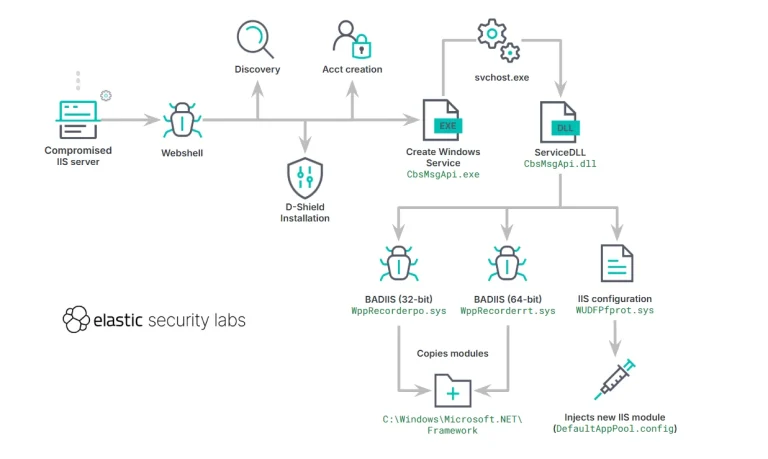
Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.

LockBit 5.0 launches with a unified codebase targeting Windows, Linux, and ESXi. Acronis reveals identical encryption and ties to SmokeLoader.

Microsoft Feb 2026 update fixes 61 flaws, including critical DWM zero-day CVE-2026-21519 exploited in the wild. Patch now to stop SYSTEM takeover.

Exploit code released for Zabbix flaw CVE-2025-27237. Low-level users can gain SYSTEM privileges on Windows via OpenSSL config. Update now.

NVIDIA patches high-severity flaws (CVE-2025-33217) in GPU drivers & vGPU software. Flaws allow code execution. Update Windows/Linux drivers now.

Critical WD Discovery flaw CVE-2025-30248 (CVSS 8.9) allows DLL hijacking during installation. Update to v5.3 immediately to prevent system takeover.
Rufus flaw CVE-2026-23988 allows local users to gain Admin rights via a race condition. Update to version 4.12 immediately to secure your system.
NVIDIA patches 4 high-severity flaws in CUDA Toolkit (up to v13.1). Vulnerabilities in Nsight Systems allow code execution & privilege escalation. Update now.

CYFIRMA reveals SolyxImmortal, a Python info-stealer using Discord webhooks for C2. It logs keys and steals files while evading detection.

A failed patch created Windows kernel flaw CVE-2025-53136. With reliable PoC exploit code now public, KASLR is bypassed. Update your systems now.
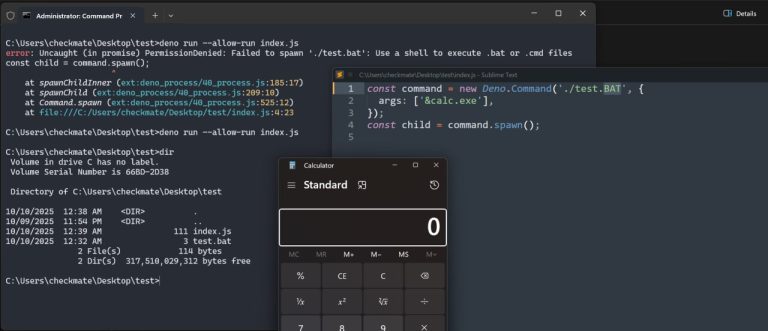
Deno, CVE-2026-22863, CVE-2026-22864, JavaScript Security, Cryptography, Command Injection, Windows Security, Node.js Compatibility, Patch Alert

Microsoft Jan 2026 Patch Tuesday fixes 114 flaws, including 3 zero-days. CVE-2026-20805 is actively exploited. Update Windows & Office immediately.

Attackers are using a fake MAS domain (get.activate.win) to deploy Cosmali Loader and XWorm RAT via PowerShell. Verify your command before running it!

TeamViewer patches high-severity flaws in its DEX line, including CVE-2025-44016, which allows attackers to bypass file integrity and execute code.

Many users are now aware that Windows 11 PCs enable device encryption by default. When a system...

Microsoft patches a high-severity Windows DWM flaw that allows low-level users to seize SYSTEM privileges via a rendering brush error. PoC availabe.