 Do Son
The October 2026 Patch Tuesday fixes 1,414 flaws and three zero-day vulnerabilities, including an exploited Windows Shell bypass. Patch now.
Windows Security
BeyondTrust patched two high-severity EPM flaws (CVE-2026-40144, CVE-2026-40145) allowing local privilege escalation on Windows. Update to 26.1.2.
Microsoft leverages advanced AI agents like MDASH to accelerate Windows vulnerability management and secure codebases.
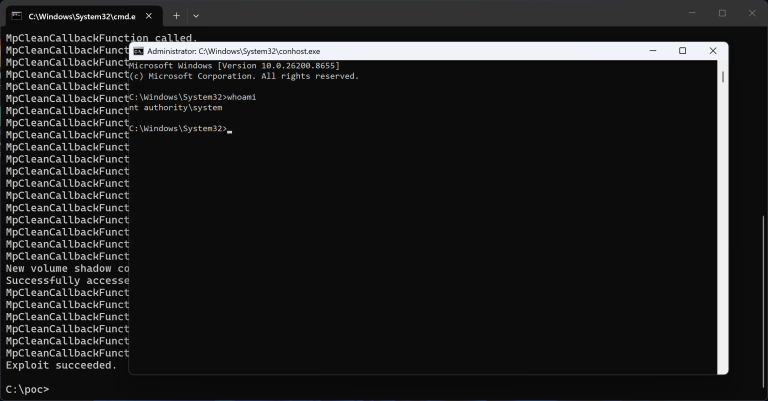
A new Microsoft Defender zero day exploit leaks online, exposing a severe race condition vulnerability affecting fully patched Windows installations.

Deploy the latest Microsoft Patch Tuesday fixes. The June release addresses severe zero day vulnerabilities and over thirty critical flaws.
Urgent: Public PoC exploit code released for YellowKey (BitLocker bypass) and GreenPlasma (SYSTEM elevation). Windows 11 and Server 2025 are at high risk.
Microsoft’s May 2026 update fixes 137 vulnerabilities, including 30 Critical RCE and EoP flaws. Prioritize patches for Netlogon, Office, and M365 Copilot now.
JDownloader's website was breached on May 6, swapping official installers for malware. If you downloaded it between May 6-7, your system may be compromised.

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!
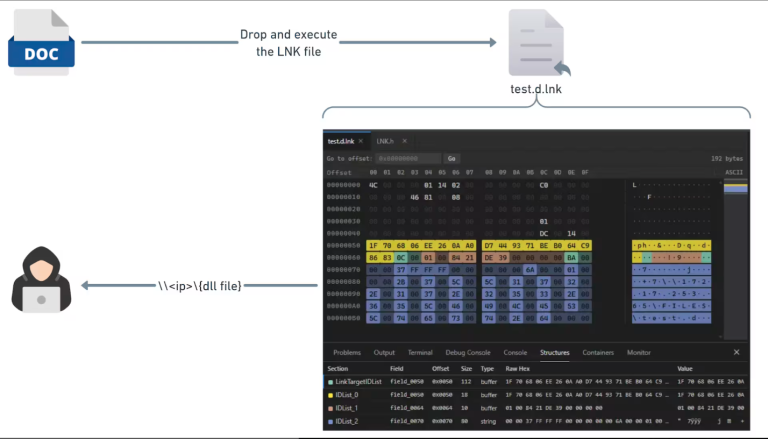
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!
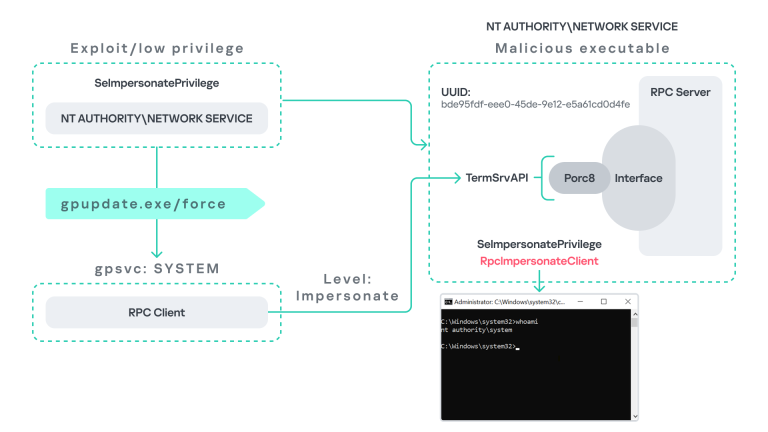
Kaspersky reveals PhantomRPC, a novel Windows architectural flaw enabling LPE to SYSTEM. Microsoft denies a patch. Monitor SeImpersonatePrivilege now.
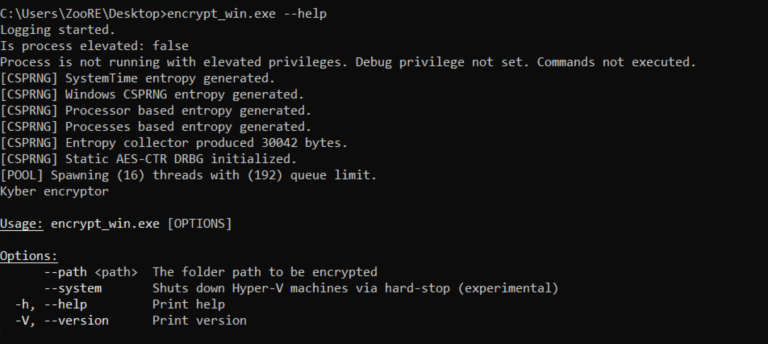
Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.
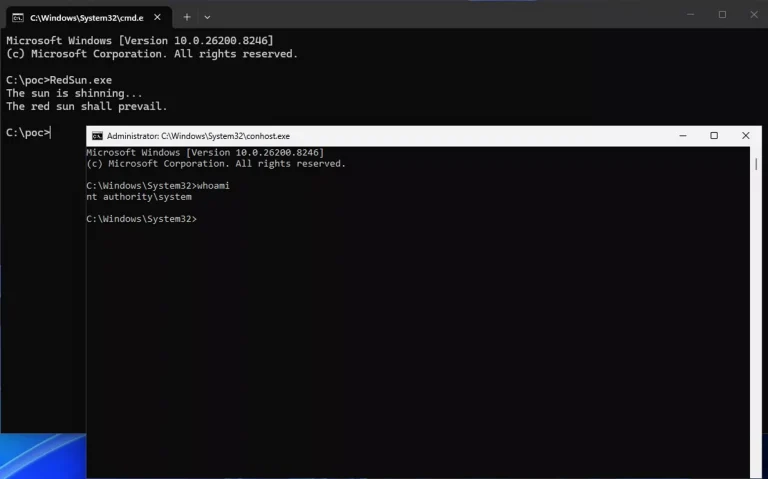
Microsoft Defender faces a critical "Red Sun" vulnerability. Learn how this zero-day exploit bypasses security to grant hackers full administrative control.

Critical 9.1 flaw in upKeeper Instant Privilege allows standard users to gain LocalSystem rights via command injection. Patch to v1.6.0.4576 immediately.

Microsoft releases KB5083769 for Windows 11, fixing BitLocker recovery loops and preparing for the critical June 2026 UEFI certificate expiration.
Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates

Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates
Microsoft’s April 2026 Patch Tuesday fixes 163 flaws, including an exploited SharePoint spoofing bug (CVE-2026-32201). Patch by April 28 per CISA mandate.
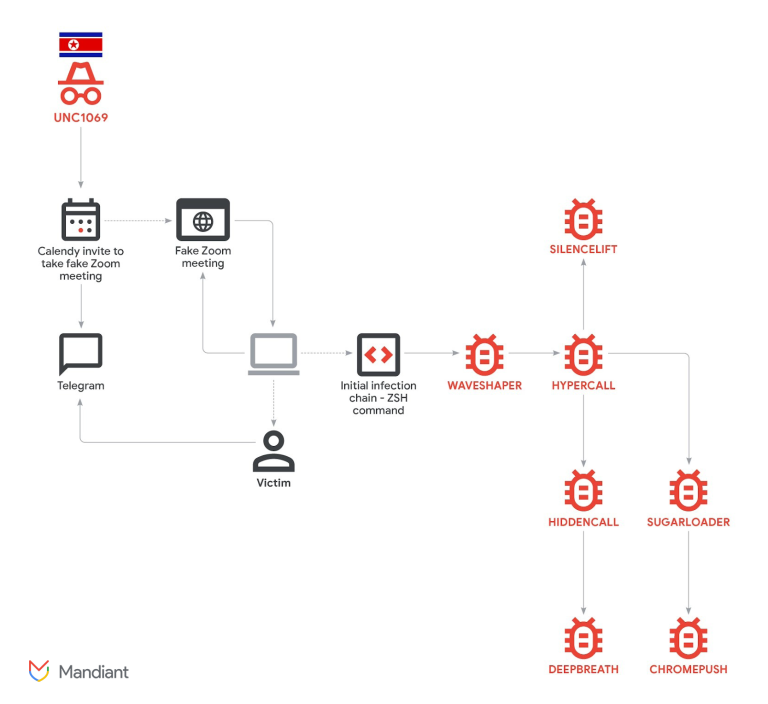
Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!

Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.
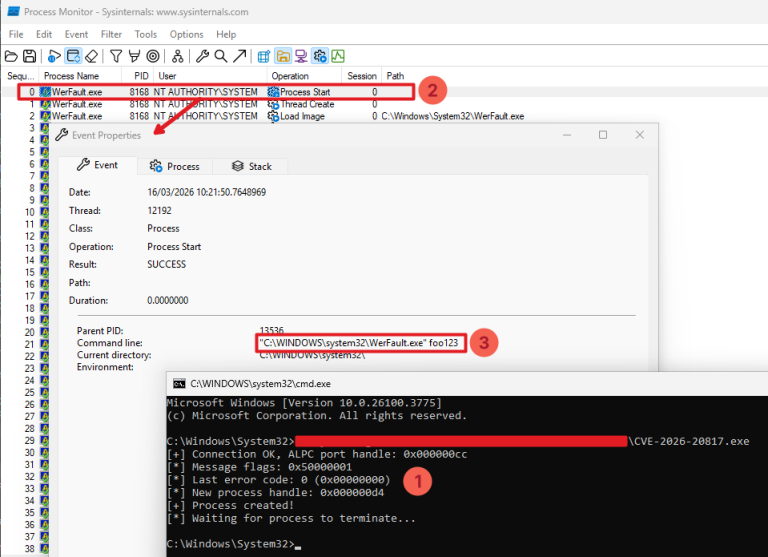
Clément Labro releases a public PoC for CVE-2026-20817, a critical Windows LPE flaw in the WER service. Patch now to prevent SYSTEM-level hijacking.
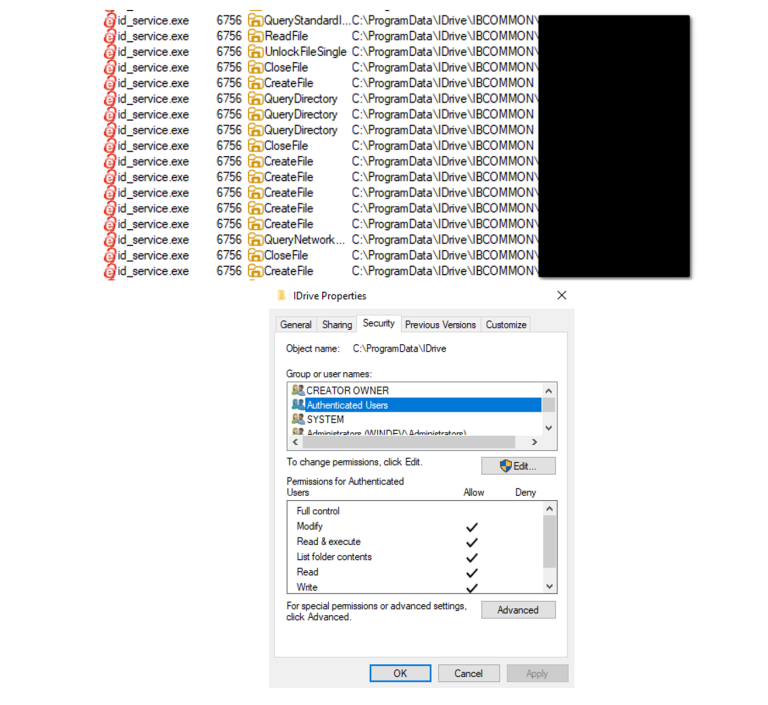
A critical flaw in IDrive for Windows (CVE-2026-1995) allows low-privilege users to seize SYSTEM control via weak folder permissions. Audit your PC today.
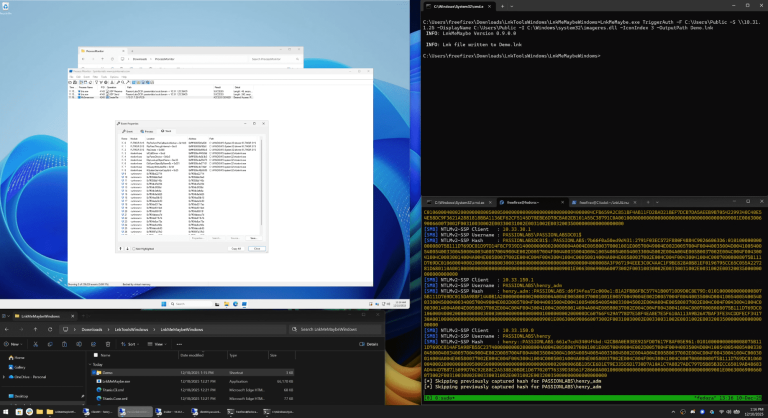
PoC exploit code is now public for CVE-2026-25185. Discover how a complex vulnerability in Windows .lnk shortcuts can be weaponized to leak network data.
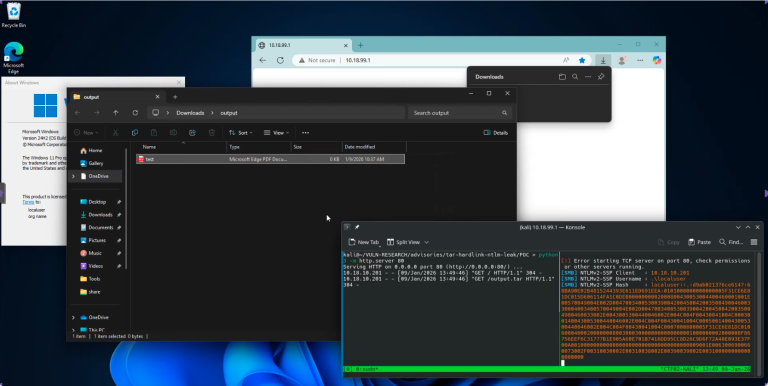
Exploit code and details for CVE-2025-59284 are now public. Discover how a Windows libarchive flaw leaks NetNTLMv2 hashes via malicious .tar archives.