 Do Son
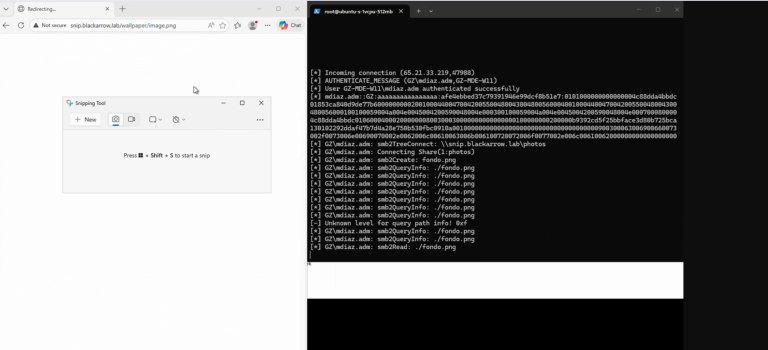
Detailed PoC and exploit code for CVE-2026-33829 are now public. See how the Windows Snipping Tool can leak NTLM hashes and how to patch the flaw.
Windows vulnerability

A new Zero-Click NTLM leak bypasses Microsoft's LNK patch, allowing unauthenticated NTLM hash theft on patched systems. The PoC works by exploiting UNC paths and the default shell32.dll icon reference.

A critical vulnerability in ASUSTOR's Windows apps, ASUSTOR Backup Plan and EZSync, allows local attackers to gain SYSTEM privileges via unquoted service paths.

CVE-2025-24054 exploited to leak NTLM hashes via .library-ms files with near-zero user interaction. Patch now to avoid exposure.

False File Immutability has raised serious concerns within the cybersecurity community due to its potential to circumvent Windows Code Integrity