
 Do Son
Wiz uncovers JINX-0132, a cryptojacking campaign exploiting misconfigured Nomad, Consul, Docker, and Gitea in DevOps environments to mine Monero.
XMRig

RedisRaider malware exploits misconfigured Redis servers to deploy cryptominers via cron jobs, evading detection with obfuscation and anti-forensics.
Outlaw botnet targets Linux servers via weak SSH, using Perl scripts and XMRig miners for crypto mining and backdoor access, Kaspersky warns.

Ten popular Visual Studio Code extensions were found secretly installing XMRig miners, exploiting users’ CPUs for unauthorized cryptomining.

Learn about the ISP Infostealer Campaign and its severe impacts on ISP infrastructure through brute force and data exfiltration.

Exploitation of CVE-2024-50603 is already occurring in the wild. Wiz Research observed attackers deploying cryptocurrency miners (XMRig) and backdoors

Discover RiseLoader, a new malware family focused on efficient payload delivery. Get insights into its origins, similarities with RisePro, and advanced anti-analysis measures.
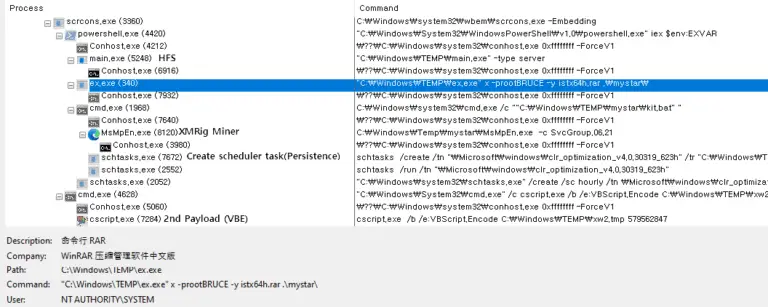
ASEC reveals the increasing sophistication of cybercriminals distributing XMRig malware through Binary Managed Object Files. Stay informed about this threat.

The persistent cyber threat known as Kinsing malware has taken a new and sophisticated approach to its cryptojacking campaign

Cato Networks reported intercepting several attempts aimed at installing the XMRig cryptocurrency mining malware using this vulnerability

A Linux-based malware family, DreamBus has been quietly evolving, honing its capabilities to exploit vulnerabilities in business applications