 Do Son
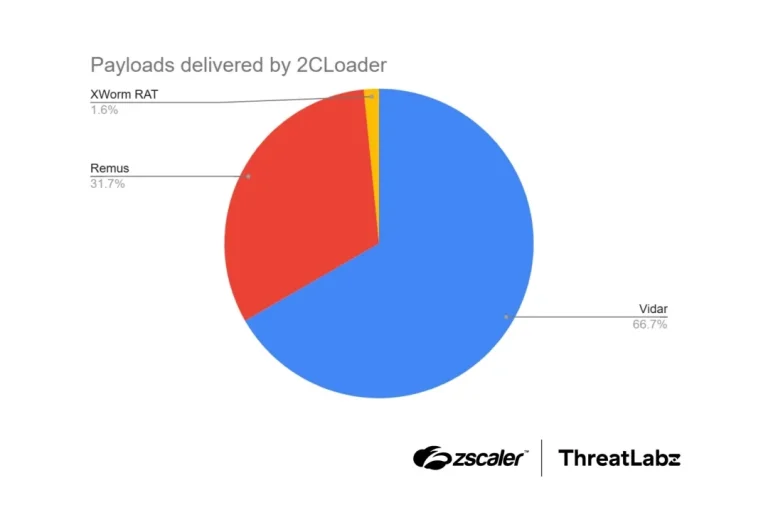
2CLoader malware dodges sandboxes and security tools to deliver Vidar and Remus infostealers. See how it works and how to detect it.
XWorm
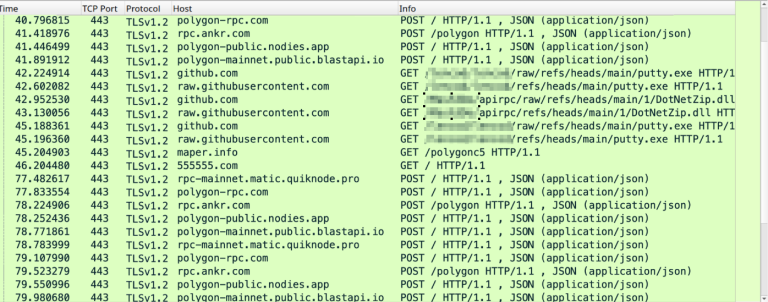
The Aeternum blockchain botnet hides C2 commands inside Polygon smart contracts, evading takedowns while dropping XWorm and XMRig payloads.
A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!

LevelBlue SpiderLabs unmasks the PhantomVAI framework: a multi-stage, fileless attack hiding XWorm and Remcos RAT inside obfuscated VBS and PNG files.

Cofense uncovers a stealthy campaign abusing legacy WebDAV in Windows File Explorer to bypass browsers and EDR, delivering XWorm and Async RAT via UNC paths.

Phishing emails use malicious Excel files to deploy XWorm RAT. The fileless attack exploits CVE-2018-0802 to steal data & control systems.

XWorm V6.0 has resurfaced with 35+ plugins, including ransomware functionality. The modular RAT uses stealth injection and obfuscated PowerShell to bypass AMSI.

A new report reveals a sophisticated XWorm backdoor campaign that uses .lnk files and a multi-stage infection chain to gain stealthy and persistent control of Windows systems.

Netskope uncovers XWorm 6.0, a new variant using VBScript droppers, AMSI bypass, and critical process marking to evade detection and force system reboots if terminated.

Splunk uncovers XWorm's evolution: a modular RAT now delivering LockBit ransomware. It uses flexible delivery, AMSI/ETW bypasses, and process injection to evade detection.

The SERPENTINE#CLOUD campaign exploits Cloudflare Tunnel subdomains and LNK files to deliver in-memory RATs like AsyncRAT and Remcos, evading detection.

Threat actors are actively compromising poorly managed MySQL servers, using UDFs to inject Gh0stRAT, XWorm, HpLoader, and legitimate Zoho agents for full system control and data theft.

A sophisticated "ClickFix" phishing campaign uses fake Booking.com CAPTCHAs to deliver RATs and info stealers to the hotel and travel industry.

Attackers exploit fake AI video tools to deploy Noodlophile Stealer and XWorm, stealing credentials and data via Telegram bots.

Stay informed about Booking Phishing schemes. Discover how attackers use social engineering to steal credentials in this campaign.
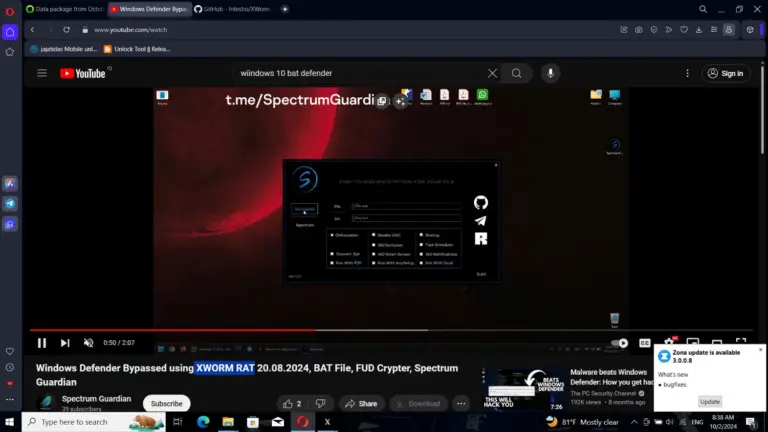
Beware of the XWorm Remote Access Trojan (RAT) builder attack. Discover how threat actors are targeting inexperienced cybersecurity enthusiasts with this malicious software.

Discover the latest cybersecurity threats during tax season. Find out how cybercriminals are targeting tax agencies and stealing sensitive information.

Protect your organization from PythonRatLoader: a sophisticated malware loader that distributes harmful remote access trojans (RATs).

Discover the latest evasive techniques and capabilities of XWorm, a sophisticated and multifaceted malware identified in 2022.

Learn about a recent government cyberattack that used a quartet of malicious software and took advantage of Cloudflare's TryCloudflare service

A new threat actor, NullBulge, has emerged with a captivating narrative: hacktivists fighting against AI's encroachment on the art world