 Do Son
The Android SMS of Death flaw crashes telephony services via malformed WAP Push messages, triggering persistent bootloops without user interaction.
Zero-Click
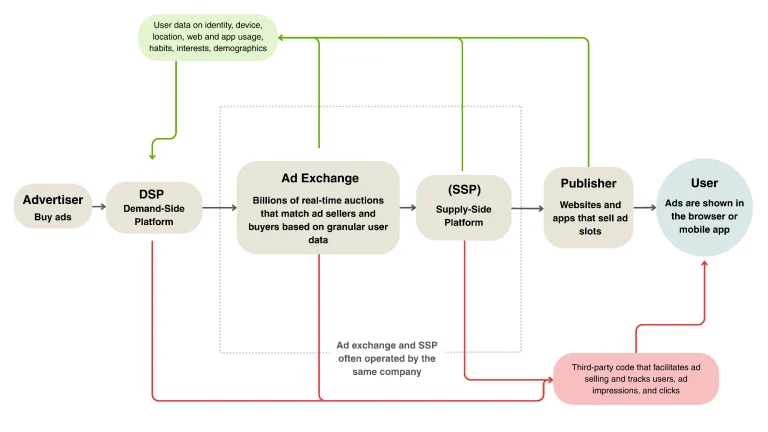
Citizen Lab exposes the AdFection spyware attack, a zero-click ad-bidding exploit that targeted at least 45 Al Jazeera devices.

A zero-click flaw in Xiaomi ShareMe (MiDrop) lets nearby attackers write files silently. Full details and PoC code are now public.
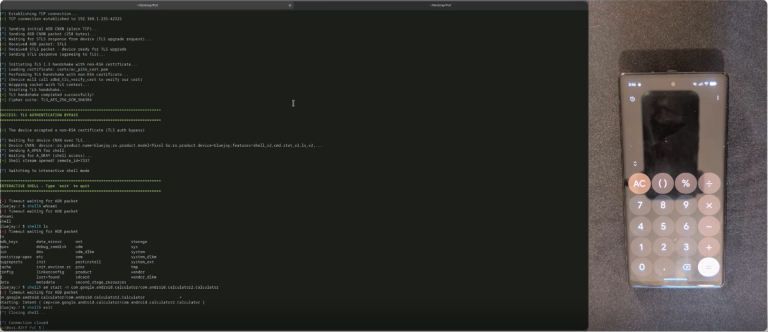
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!

Google warns of CVE-2026-0073: a critical zero-click Android vulnerability allowing remote code execution via Wireless ADB. Patch to May 2026 level now!
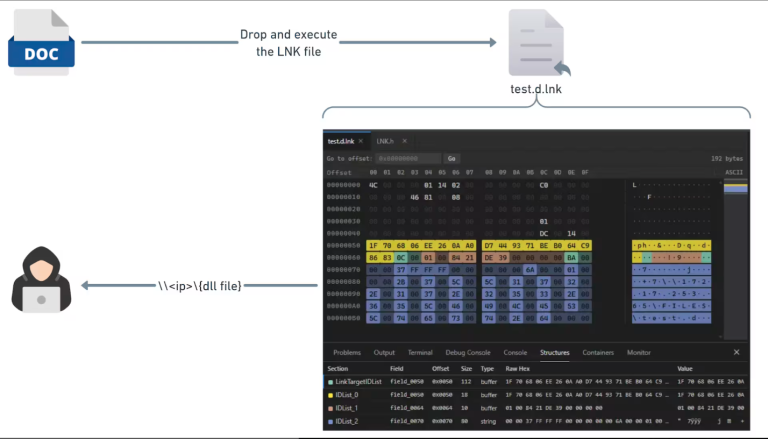
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!

A critical 9.8 CVSS zero-click flaw (ZDI-CAN-30207) hits Telegram, affecting 1 billion users. No interaction needed for full system hijack. Patching now!
Public PoC exploit for Android CVE-2024-23700 allows critical privilege escalation without user interaction. WearOS & Custom ROMs are at risk.

PrestaShop patches a 9.1 critical flaw (CVE-2025-61922) in the Checkout module. Attackers can hijack accounts via email. PoC available.

CISA issued an urgent alert: Commercial spyware is actively exploiting zero-click flaws and malicious QR codes to hijack messaging apps (Signal, WhatsApp) for espionage against government and civil society targets.

Unit 42 exposed LANDFALL, commercial-grade spyware that exploited a Samsung zero-day (CVE-2025-21042) in the image library libimagecodec.quram.so to compromise Galaxy phones via DNG images sent over WhatsApp.

Google's November 2025 update fixes a Critical RCE flaw (CVE-2025-48593) in the Android System component. Exploitation requires no user interaction and affects Android versions 13 through 16.

Google Project Zero disclosed a zero-click RCE flaw (CVE-2025-54957, CVSS 7.0) in Dolby's Audio Decoder. The integer overflow can be triggered by a single audio file and affects Android, iOS, and macOS.

A new Zero-Click NTLM leak bypasses Microsoft's LNK patch, allowing unauthenticated NTLM hash theft on patched systems. The PoC works by exploiting UNC paths and the default shell32.dll icon reference.

Apple overhauled its Security Bounty program, offering a $2M base reward (up to $5M with bonuses) for zero-click exploits that match mercenary spyware attacks and bypass Lockdown Mode.

Apple has issued new spyware alerts to French officials, journalists, and activists. These warnings are often tied to highly sophisticated, zero-click attacks.

CISA adds two flaws to its KEV Catalog: a TP-Link factory reset flaw and a WhatsApp zero-click vulnerability used in targeted spyware attacks. Patching is urgent.

A new report from Sekoia.io reveals how the global commercial spyware industry is thriving despite sanctions, selling sophisticated zero-click surveillance tools to governments.

A critical zero-click flaw in WhatsApp (CVE-2025-55177), paired with an Apple zero-day, was used in sophisticated attacks. All users must update now.

A new zero-click NTLM flaw (CVE-2025-50154) bypasses Microsoft's patch for a similar vulnerability, allowing attackers to leak credentials and drop malware.

"EchoLeak," a new AI zero-click vulnerability, allowed data exfiltration from Microsoft 365 Copilot via sophisticated prompt injection. Microsoft has patched the flaw.
