 Do Son
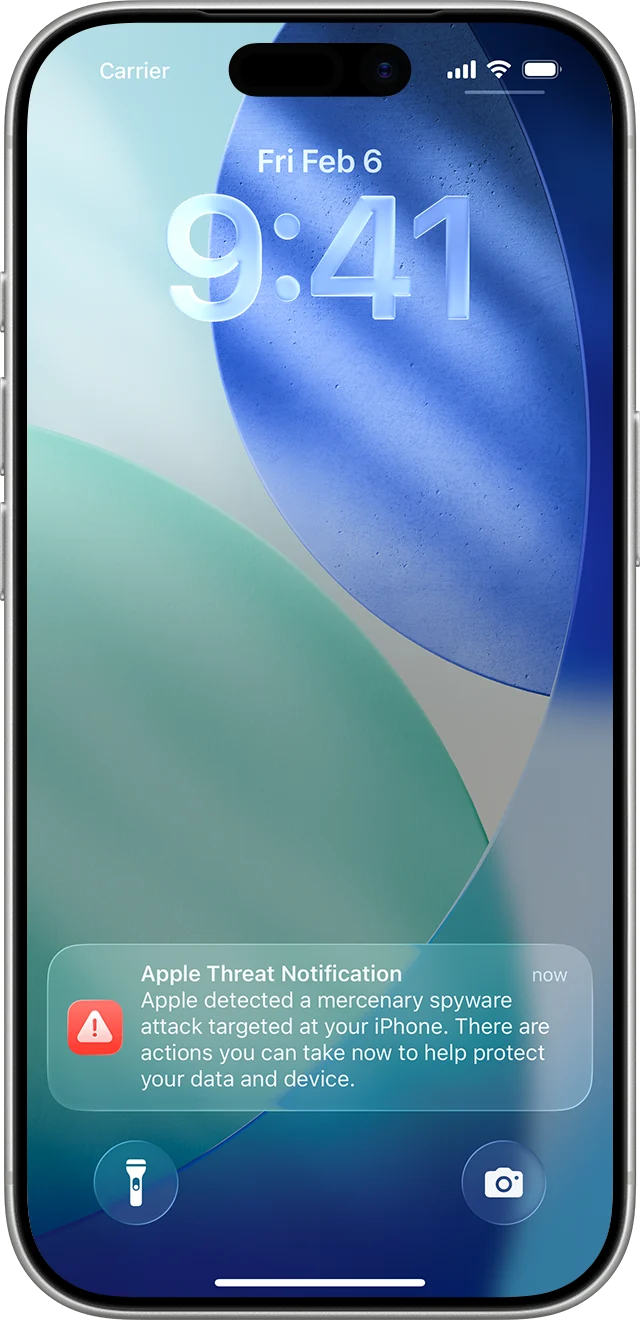
Apple recently warned targeted individuals across ninety-nine nations regarding sophisticated digital surveillance operations. Specifically, the emerging Apple mercenary spyware threat singles out journalists who previously endured device compromises. Threat researchers confirmed the legitimacy of these urgent notifications. However, initial forensic event logs reveal no definitive attribution signatures. Consequently, the covert sponsors orchestrating this global espionage wave remain unidentified.
Investigative Reporters Encounter Repeat Surveillance
Prominent investigative figures immediately disclosed receiving high-priority intrusion warnings. For example, Middle East Eye bureau chief Ragip Soylu received three separate Apple warnings throughout 2026. Soylu suspects state-backed entities repeatedly attempted to infiltrate his mobile device. Furthermore, as highlighted in the Financial Times coverage of global iPhone surveillance alerts, these digital campaigns escalate pressure on international press corps. Nevertheless, conclusive forensic evidence identifying specific state actors remains undisclosed.
Similarly, Lebanese documentary filmmaker Radwan Mortada received an urgent intrusion notification. Mortada previously survived zero-click Pegasus intrusions in 2017 and 2021. Such zero-click payloads penetrate mobile endpoints without requiring user interaction. Consequently, these silent exploits present grave risks to confidential journalistic sources.
Moreover, Mortada noted the suspicious timing surrounding this latest digital targeting. The notification arrived shortly after his documentary detailing the September 2024 pager explosions. Following the broadcast, military forces raided his family residence in southern Lebanon. However, investigators have established no direct technical correlation between the physical attack and digital espionage.
Protective Protocols and Enterprise Defensive Posture
Apple deliberately conceals proprietary technical artifacts to protect client ecosystems. Disclosing precise attack signatures could assist exploit brokers in bypassing hardware protections. Furthermore, state-backed surveillance contractors spend millions of dollars engineering bespoke zero-day exploits. In addition, these targeted campaigns mirror incidents where lawmakers experienced mercenary spyware incursions on their iPhones across Europe.
Enabling Lockdown Mode and Validating Warnings
Recipients should immediately activate Lockdown Mode to restrict susceptible operating routines. Independent security evaluations demonstrate that this hardened mode successfully blocks sophisticated zero-click payloads. As detailed in the official Apple threat notification guidance documentation, users can verify alert authenticity through their Apple Account. Furthermore, these defensive measures align with BSI cybersecurity advisories on Apple mercenary spyware defenses. Ultimately, vigilant operational security remains essential when confronting state-grade offensive cyber capabilities.
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
