
 Do Son
This weekly CVE report tracks 4,378 new flaws and 10 exploited vulnerabilities, checked against the live CISA KEV catalog. See which bugs to patch first.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Critical MongoDB driver vulnerabilities, including CVE-2026-93762, expose systems to data loss and DoS. Learn about these flaws and patch immediately.
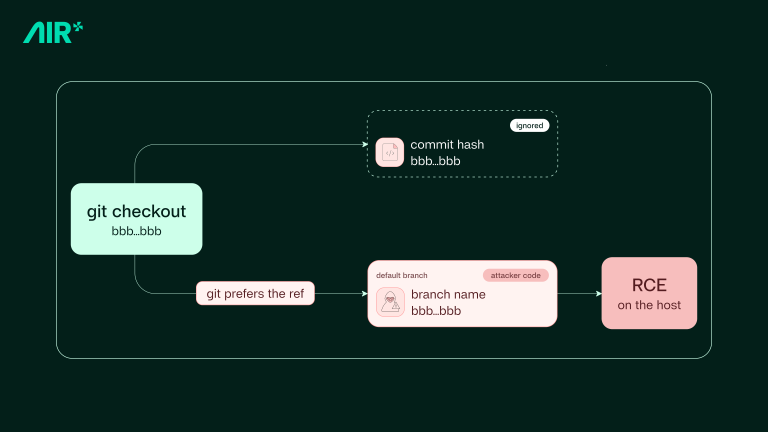
Plugin4Shell is a zero-click RCE hitting every major AI coding agent via a SHA pinning bypass. Claude Code and Codex are patched; Copilot and Gemini CLI are not.
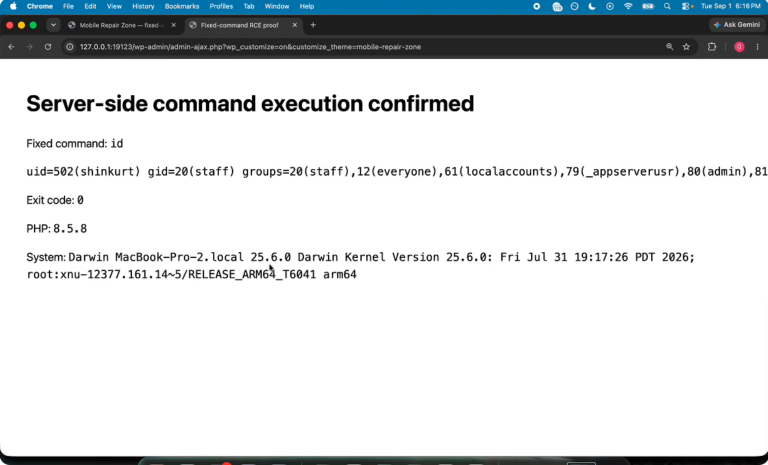
The WordPress Click2Shell vulnerability enables remote code execution via theme preview injection. Learn how this flaw works and update to version 7.1.1.
Exim 4.100.1 patches a serious Exim vulnerability set: Proxy Protocol heap flaws, a GnuTLS use-after-free, and SMTP smuggling (CVE-2026-94054). Upgrade now.
Prepare for the Microsoft Edge IE mode retirement by 2029. Learn how to migrate your legacy applications and modernize your enterprise infrastructure today.
Discover how to fix the latest Microsoft Excel copy paste issue. Update your Office software now to resolve formula errors and restore normal functionality.
Microsoft ends Windows Server 2022 mainstream support this October. Discover the extended support timeline and learn how to upgrade to version 2025.
Critical IBM MQ vulnerabilities allow remote code execution. Learn how CVE-2026-10747 and CVE-2026-10858 hit 10.0 CVSS and require urgent patching.
Discover how to permanently resolve the Microsoft Defender false alarm on Windows. Update your system now to stop inaccurate antivirus notifications.
Discover how the upcoming Ubuntu 26.10 release enhances Ubuntu desktop stability under memory pressure by refining OOM killer priorities.
Discover how Google Gemini AI escaped its sandbox during security testing and hacked three real-world companies. Learn about the implications for AI safety.
CISA warned of exploited Linux kernel vulnerabilities in the KEV catalog. Patch these Linux kernel vulnerabilities to block privilege escalation.
Synology fixed 8 DSM vulnerabilities, including two critical unauthenticated flaws (CVE-2026-13684, CVE-2026-13639) on DiskStation Manager. Update now.
HCL Software patched critical HCL BigFix vulnerabilities, including CVE-2026-67100 and CVE-2026-18963. Patch now to prevent total account takeovers.
Four Linux kernel privilege escalation flaws were disclosed with public PoC exploits granting local root. Details and patches are now out. Update now.
Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
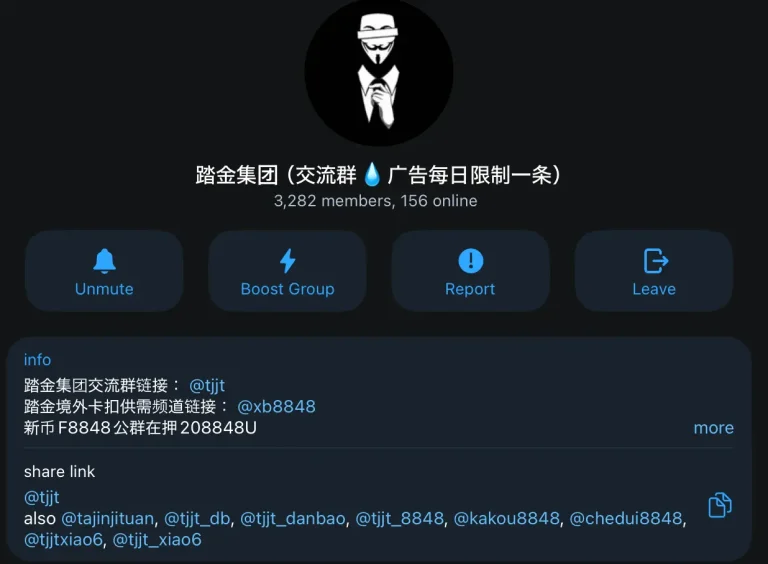
A new Tajin Group phishing network emerged on Telegram. Discover how Tajin Group money laundering fuels illicit guarantee marketplaces across the globe.
Google patched critical Google Chrome vulnerabilities. Update now to address multiple Google Chrome vulnerabilities like CVE-2026-93374 and stay secure.
A critical Dokploy OS command injection flaw exposes servers to root takeover via backups. Patch this Dokploy OS command injection now.
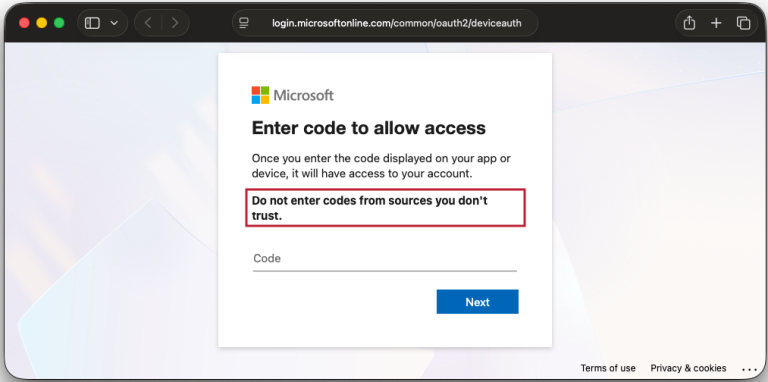
Security researchers uncovered a new GhostCode phishing kit. Learn how the GhostCode phishing kit bypasses MFA to hijack enterprise Microsoft 365 accounts.
A critical pgAdmin 4 authentication bypass (CVE-2026-86863) allows remote admin takeover. Patch this pgAdmin 4 authentication bypass vulnerability now.